 Do Son
This weekly CVE report covers 1,877 new CVEs and 6 actively exploited vulnerabilities in CISA KEV, including N-able, TeamCity, and Langflow.
CISA KEV
TeamCity vulnerability CVE-2026-63077 enables unauthenticated remote code execution. CISA added it to the KEV catalog amid active exploitation.
CISA added three bugs to its KEV list. An N-able N-central authentication bypass is exploited in the wild to deploy RMM tools. Patch by August 7.
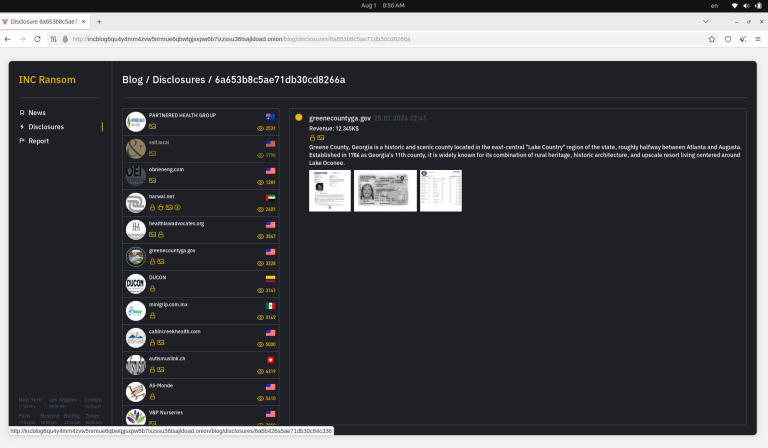
A SonicWall SMA exploit chain (CVE-2026-15409, CVE-2026-15410) grants root access and now feeds INC Ransomware attacks. Patch to 12.5.0-02835+.
CVE weekly roundup for Jul 27–Aug 2: 2,077 new flaws logged, 273 critical, 14 rated CVSS 10.0, and 3 CISA KEV additions with active exploitation.
CISA KEV additions on July 27 flag two known exploited vulnerabilities: Arista VeloCloud CVE-2026-16812 and FortiOS CVE-2025-68686. Patch both now.
Read our latest weekly threat intelligence briefing. This active vulnerability update reveals critical Microsoft Exchange and Oracle flaws for July 2026.
CISA added four flaws to its KEV catalog, including WordPress RCE (CVE-2026-63030) and Langflow RCE (CVE-2026-0770). All are exploited in the wild.
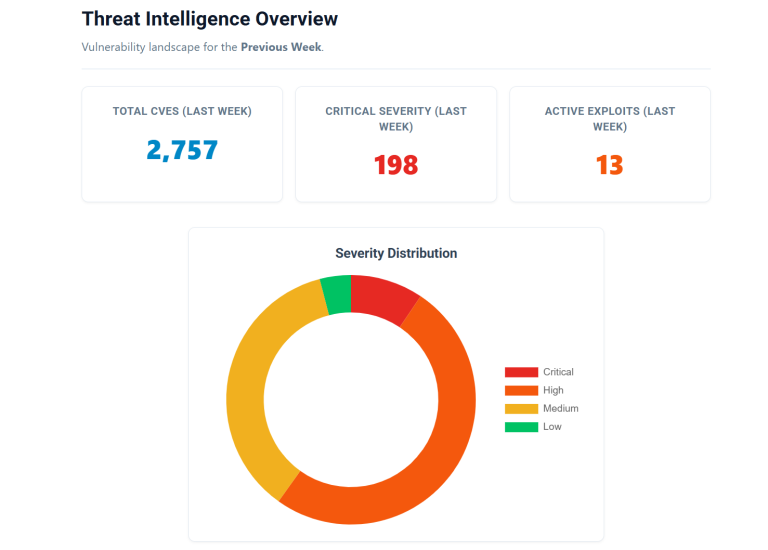
Read our mid-July weekly threat intelligence report. Stay informed on active vulnerability updates, Fortinet flaws, and CISA KEV additions.
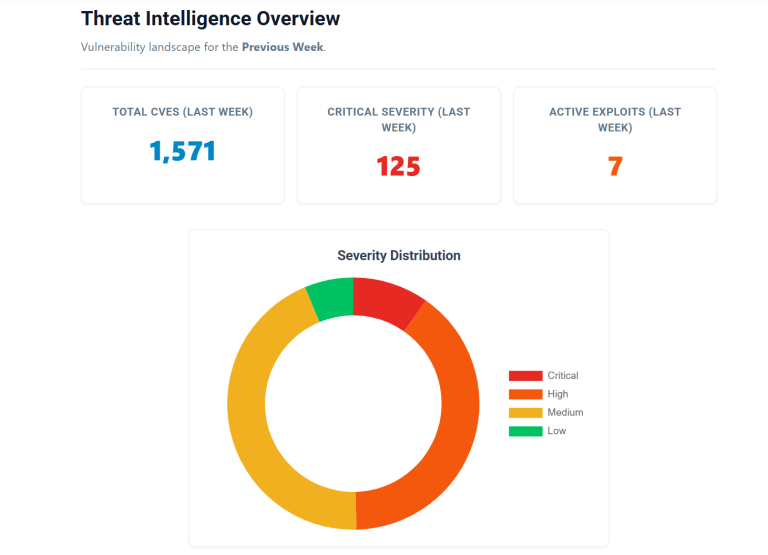
Our weekly CVE report: 1,571 new flaws and 6 actively exploited vulnerabilities hit CISA KEV, including ColdFusion and Joomla RCE.
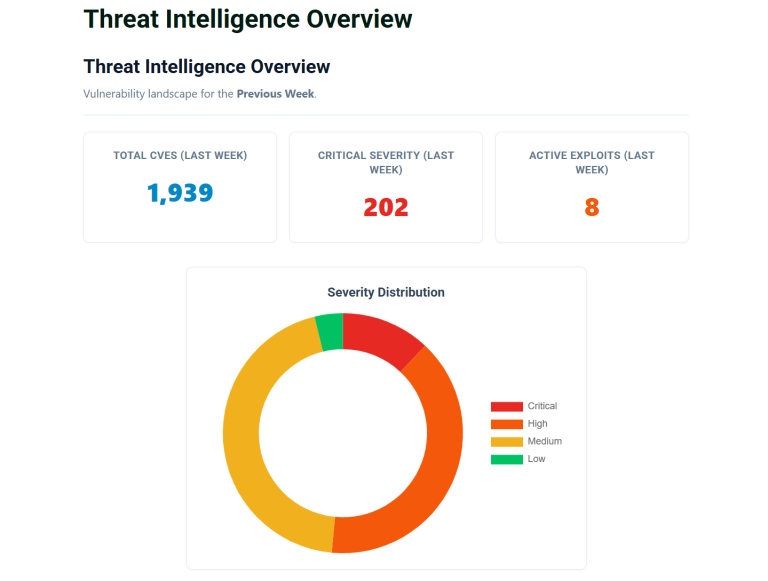
Read our weekly threat intelligence briefing. Our active vulnerability report reveals new zero-day exploits and critical CISA KEV additions.
CISA flags an actively exploited SharePoint vulnerability (CVE-2026-45659) enabling remote code execution. Patch SharePoint Server 2016 now.
Attackers exploit a Cisco Unified CM RCE flaw (CVE-2026-20230) in the wild. Public PoC code now details the SSRF-to-root chain. Patch now.
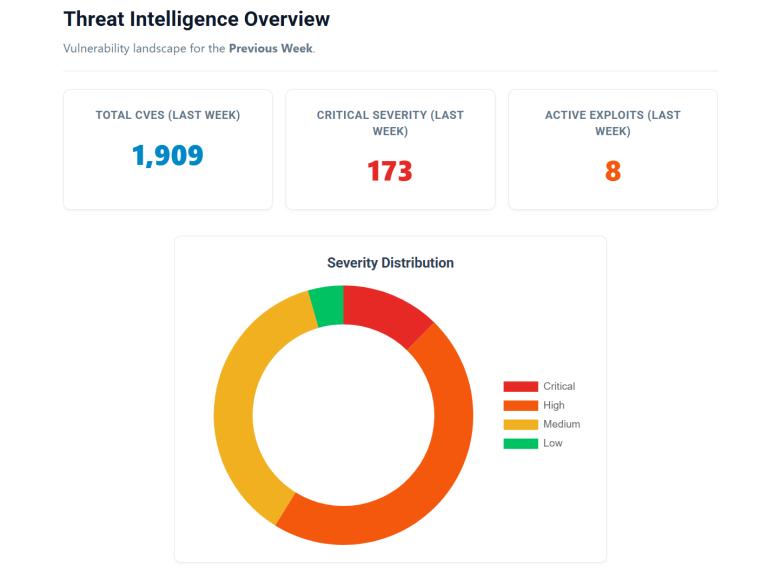
This weekly CVE report covers 1,909 new vulnerabilities from June 22-28, 2026. CISA flagged six as exploited, including CVE-2026-20230.
CISA added two flaws to its KEV Catalog: a Cisco Unified CM SSRF bug and a PTC Windchill RCE. Federal agencies must patch by June 28, 2026.
CISA added four actively exploited vulnerabilities to its KEV catalog, hitting Ubiquiti UniFi OS and Lantronix EDS5000. Patch before June 26, 2026.
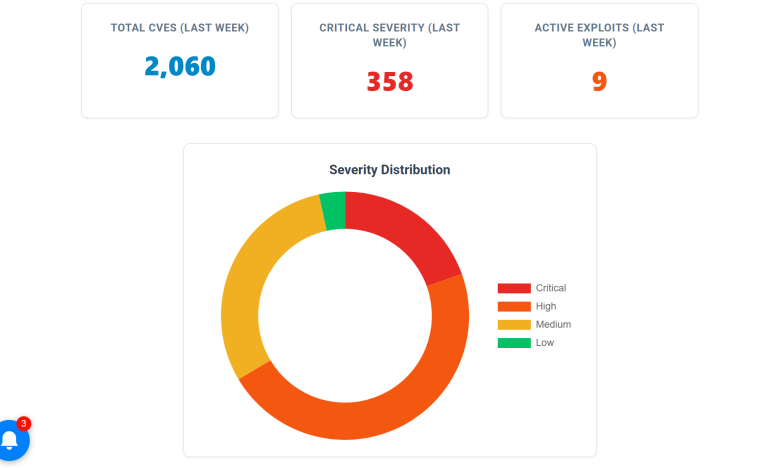
This weekly CVE report covers 2,060 new vulnerabilities from June 15-21, including 358 critical flaws and 4 actively exploited CVEs now in CISA KEV.
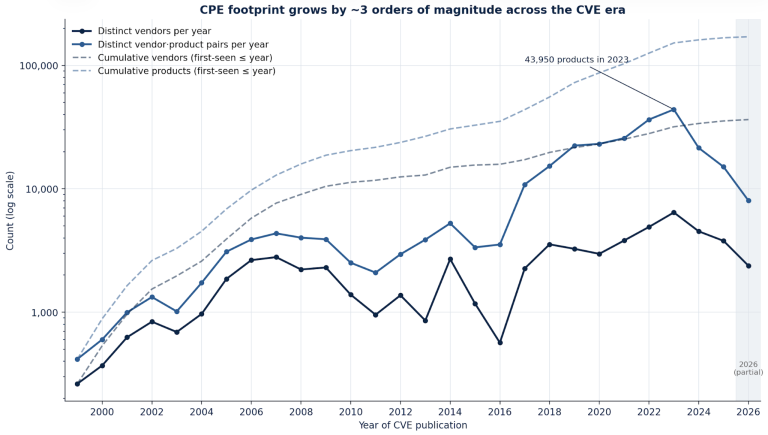
FIRST's 2026 vulnerability forecast warns AI vulnerability discovery could push CVEs to 66K, yet just 6.5% are truly actionable. Here's why.
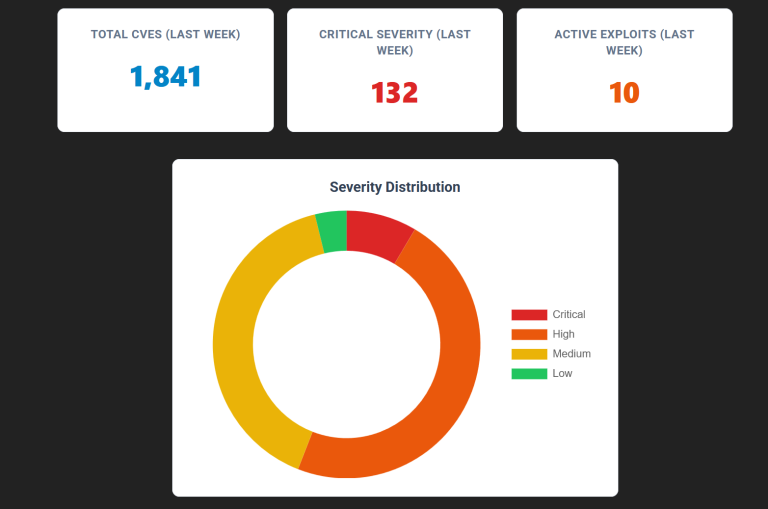
Read our weekly threat intelligence briefing. This vulnerability management report covers active exploits in Cisco, Ivanti, and Chrome for June 2026.
The CISA active exploit catalog now includes three known exploited vulnerabilities from Cisco, Arista, and Chromium. Update your systems today.

CISA expands its active exploit catalog with critical gateway flaws in BerriAI LiteLLM and Check Point configurations. Patch immediately.
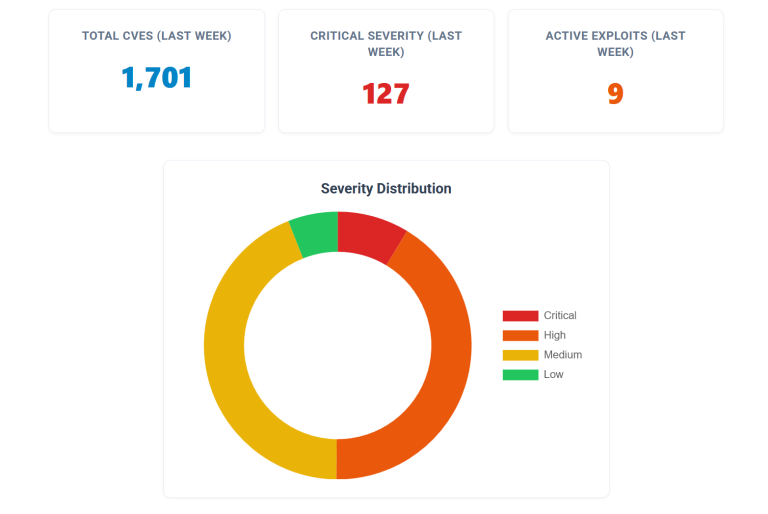
Read our weekly threat intelligence briefing. This active vulnerability management report covers June 2026 CISA KEV additions and new zero-day exploits.