 Do Son
CISA added two flaws to its KEV Catalog: a Cisco Unified CM SSRF bug and a PTC Windchill RCE. Federal agencies must patch by June 28, 2026.
CISA KEV

CISA added four actively exploited vulnerabilities to its KEV catalog, hitting Ubiquiti UniFi OS and Lantronix EDS5000. Patch before June 26, 2026.

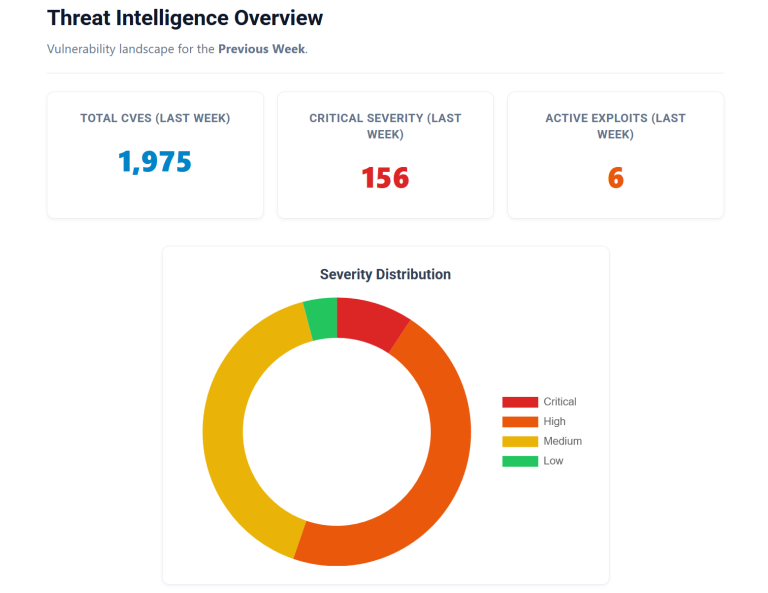
This weekly CVE report covers 2,060 new vulnerabilities from June 15-21, including 358 critical flaws and 4 actively exploited CVEs now in CISA KEV.

FIRST's 2026 vulnerability forecast warns AI vulnerability discovery could push CVEs to 66K, yet just 6.5% are truly actionable. Here's why.

Read our weekly threat intelligence briefing. This vulnerability management report covers active exploits in Cisco, Ivanti, and Chrome for June 2026.
The CISA active exploit catalog now includes three known exploited vulnerabilities from Cisco, Arista, and Chromium. Update your systems today.

CISA expands its active exploit catalog with critical gateway flaws in BerriAI LiteLLM and Check Point configurations. Patch immediately.

Read our weekly threat intelligence briefing. This active vulnerability management report covers June 2026 CISA KEV additions and new zero-day exploits.

Protect your network from active CVE-2026-28318 exploitation. Apply patches for this critical Serv-U vulnerability before the June 19 deadline.

CISA added new actively exploited vulnerabilities to its catalog. Learn how the Android privilege escalation flaw impacts corporate environments.

Read our weekly threat intelligence briefing. Our active vulnerability report reveals new zero-day exploits and CISA KEV additions for May 2026.

Read our weekly threat intelligence briefing. Discover active exploits, critical CVEs, and the latest CISA KEV additions for May 18–24, 2026.
CISA updates its KEV Catalog with critical flaws in Langflow (CVE-2025-34291) and Trend Micro Apex One. Federal agencies ordered to patch by June 4, 2026.

Sysdig exposes "NATS-as-C2" infrastructure exploiting Langflow RCE (CVE-2026-33017). Learn how to defend your AI pipelines and block the exploit.
Cisco SD-WAN (CVE-2026-20182) and Exchange Server (CVE-2026-42897) are actively exploited in the wild! Discover the top threats you must patch now.
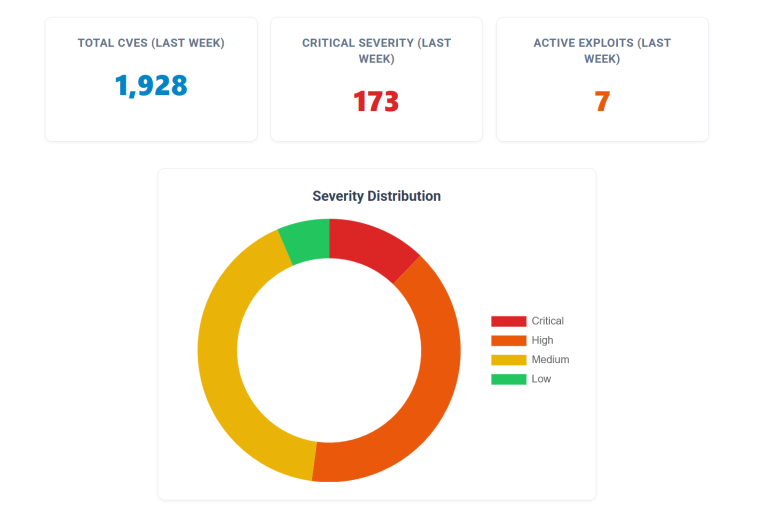
Weekly Security Digest: 1,928 new vulnerabilities hit the wire. From Palo Alto firewalls to LiteLLM AI gateways, here is how to prioritize your defense.

Weekly Triage: 1,134 new vulnerabilities found, including a 9.8 critical bypass in cPanel/WHM and active Express.js logic flaws. Patch your systems now.

CISA warns "Copy Fail" (CVE-2026-31431) is exploited in the wild. Millions of Linux systems since 2017 are vulnerable to instant root privilege takeover.
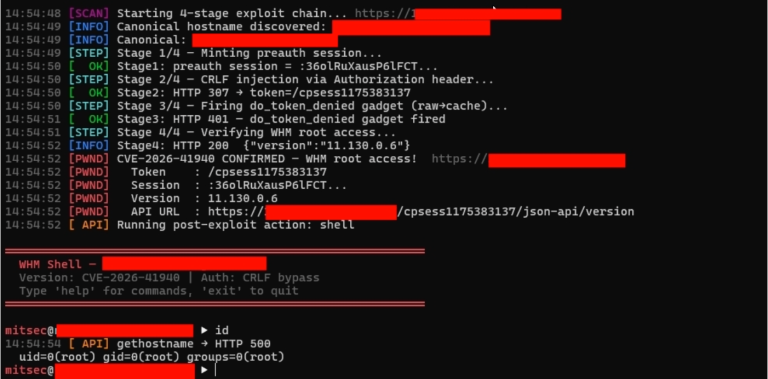
CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!
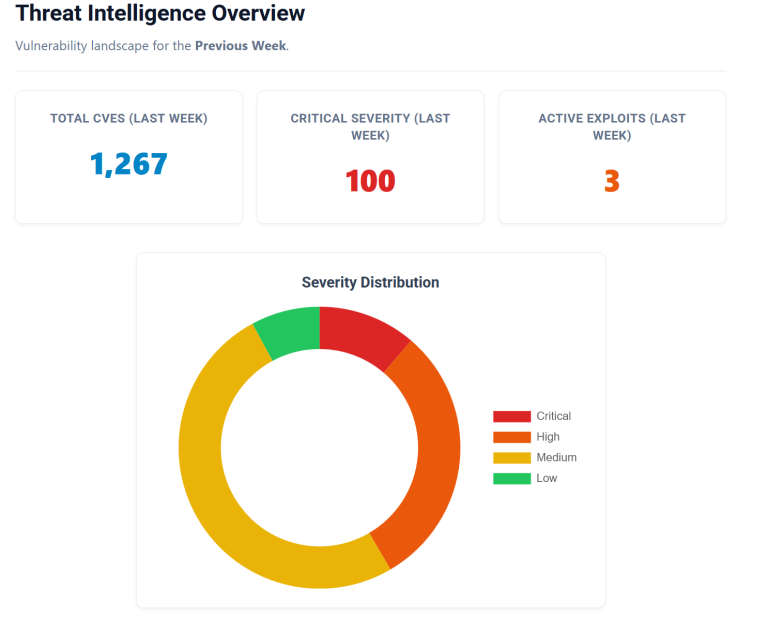
Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20,Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20, 2026. 2026.

Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.

CISA adds BlueHammer (CVE-2026-33825) to the KEV catalog. This Microsoft Defender LPE exploit uses TOCTOU to hijack SAM databases. Patch by May 6, 2026.