
 Do Son
Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!
Cisco Talos

Cisco Talos exposes UAT-9244, a China-linked APT targeting South American telecoms with stealthy malware like the BitTorrent-based PeerTime and TernDoor.
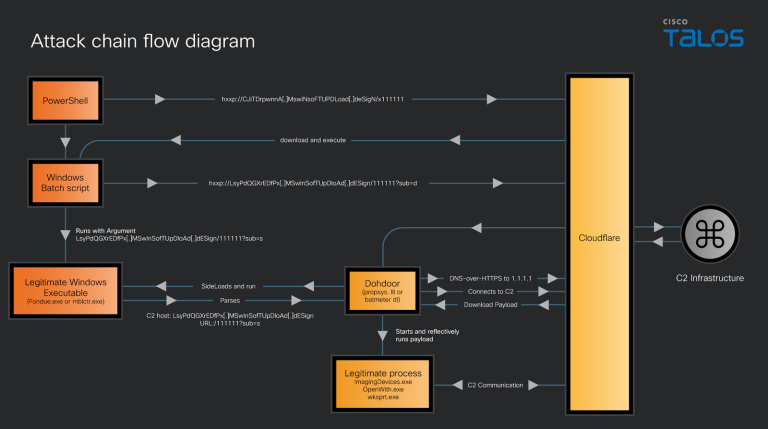
Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.

Cisco Talos warns of CVE-2026-20127, a CVSS 10 flaw in Catalyst SD-WAN exploited since 2023. UAT-8616 bypassed authentication to hijack global network fabrics.

Cisco Talos reveals VoidLink, a modular Linux malware framework by UAT-9921. Features "compile-on-demand" tools to target IoT & cloud infrastructure.

Cisco Talos exposes DKnife, a router malware that inspects traffic and swaps legitimate downloads for ShadowPad backdoors. Active since 2019.

Cisco Talos warns of UAT-8099 targeting Asian IIS servers with region-locked BadIIS malware. New variants now attack Linux systems.

Cisco Talos warns: China-linked UAT-8837 targets North American infrastructure using zero-days (CVE-2025-53690) & open-source tools.
High-severity Hikvision stack overflow flaws (CVE-2025-66176) allow attackers to crash cameras & NVRs via LAN. Update firmware now to prevent DoS.

Cisco Talos reveals UAT-7290, a China-nexus group targeting global telecoms. They act as both spies and infrastructure builders for other hackers.

Cisco warns of a CVSS 10 zero-day (CVE-2025-20393) exploited by Chinese APT UAT-9686 to backdoor Secure Email Gateways with the Aqua malware suite.

Cisco Talos exposed UAT-8099, a Chinese group compromising IIS servers for SEO fraud, using BadIIS malware and Cobalt Strike to steal credentials and manipulate search rankings.

Cisco Talos uncovers a long-running espionage campaign using a new PlugX backdoor. The malware shows strong links to Chinese APT groups Naikon and BackdoorDiplomacy.
A new report from Cisco Talos details UAT-7237, a Chinese-speaking APT group targeting Taiwan's web infrastructure with customized open-source tools.

A new report from Cisco Talos details PS1Bot, a modular PowerShell-based malware campaign using malvertising to steal data and maintain stealthy persistence.

Cisco Talos' Q2 2025 report reveals phishing is the top access method. Ransomware, including Qilin, dominated, with a surprising trend of attackers abusing PowerShell 1.0 to evade security.

Cisco Talos uncovers a sophisticated MaaS operation leveraging public GitHub repos and the Emmenhtal loader to distribute Amadey, SmokeLoader, and AsyncRAT, often via phishing.

North Korean APT Famous Chollima (Wagemole) is using a new Python-based RAT, PylangGhost, in fake job interviews to target crypto professionals and steal credentials.

Cisco Talos reveals "PathWiper," a new destructive malware used in a highly confident Russia-nexus APT attack against Ukrainian critical infrastructure.

Cisco Talos uncovers ToyMaker's IAB activity, paving the way for Cactus ransomware. Learn how LAGTOY backdoor & credential theft led to a major breach.

Cisco Talos reveals a new VIP version of XorDDoS with centralized control, enabling global DDoS attacks. U.S. targeted in over 70% of observed campaigns.

A widespread smishing campaign targeting toll road users across multiple U.S. states is stealing payment credentials. Learn how scammers are impersonating E-ZPass and other toll systems to trick victims