 Do Son
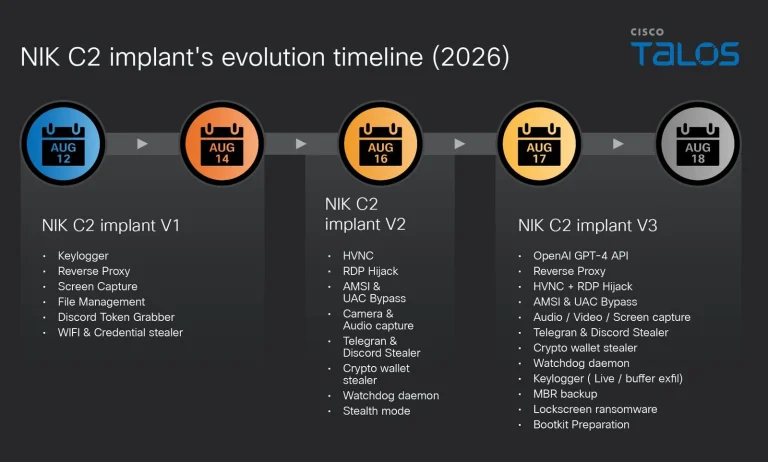
Cisco Talos uncovers the NIK C2 framework. This Windows NIK C2 framework abuses OpenAI APIs to analyze stolen victim data and deploy screen lockers.
Cisco Talos
Cisco Talos uncovered the KeyDrift malware UAT-11473 campaign exploiting CVE-2026-20127 to steal IPsec keys from Cisco SD-WAN controllers.
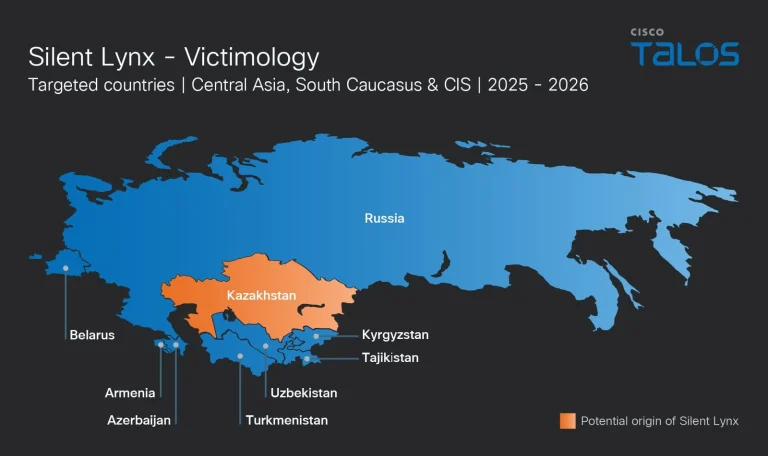
Cisco Talos and Recorded Future exposed the UAT-6275 threat actor targeting CIS governments with WinRAR exploits and custom reverse shells.
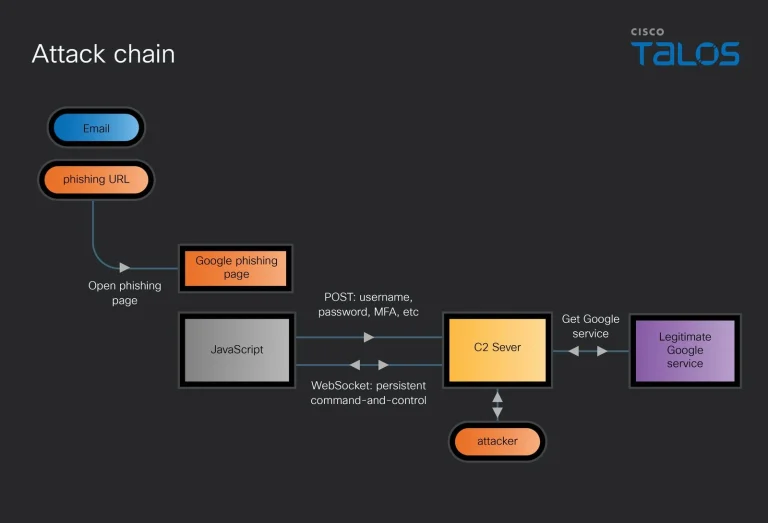
UAT-11985 used AI-written lures and an AitM phishing kit in a Taiwan spear-phishing campaign that steals Google logins and bypasses MFA.
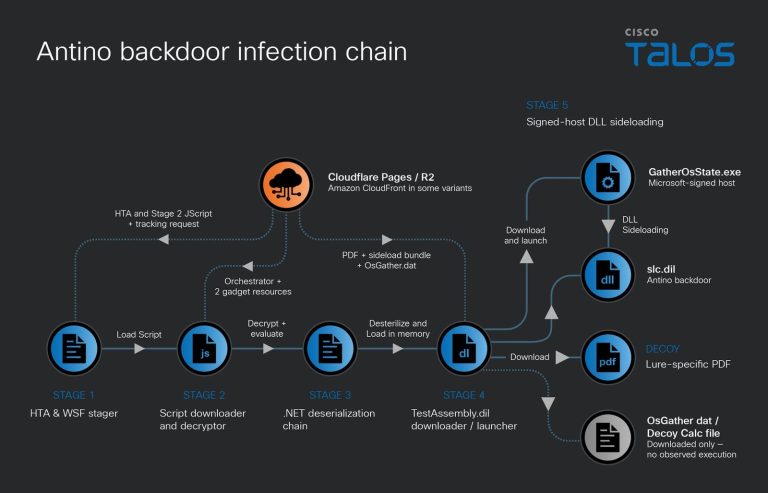
UAT-11587 Antino backdoor attacks hit Asian targets. Cisco Talos reveals how the Antino backdoor abuses Microsoft 365 for cyberespionage.
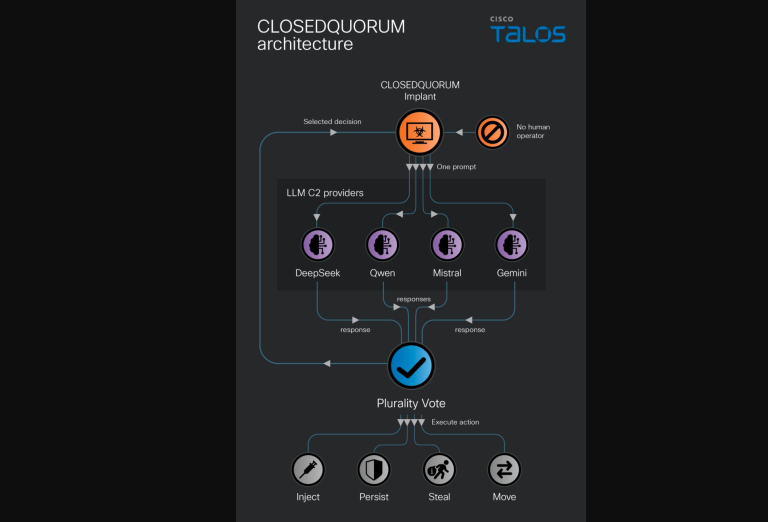
Cisco Talos discovered autonomous CLOSEDQUORUM AI malware. The CLOSEDQUORUM AI malware uses multiple LLMs to guide cyberattacks independently.
A ClickFix browser attack uses Google Sheets C2 to inject a crypto web skimmer into Chrome. See how Cisco Talos traced the theft.
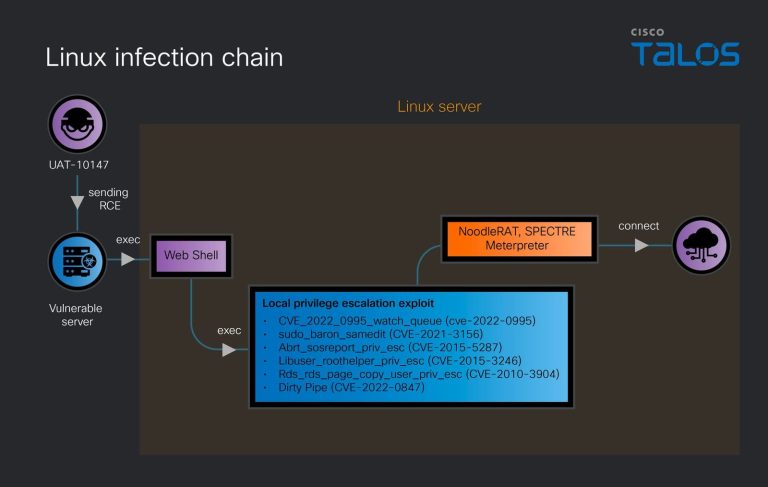
Cisco Talos revealed how UAT-10147 agentic AI attacks target global servers. Learn how UAT-10147 agentic AI tools automate intrusions and data theft.

Cisco Talos found msaRAT malware, a Rust RAT from the Chaos ransomware group that hides C2 traffic inside headless Chrome and Edge sessions.

Starland RAT is new malware from Russian-speaking actor UAT-11795. It steals crypto wallets and credentials via fake Zoom and WebEx installers.

UAT-7810, a China-nexus APT, grows its LapDogs ORB network with new router malware including LONGLEASH, DOGLEASH, and JARLEASH. Cisco Talos reports.
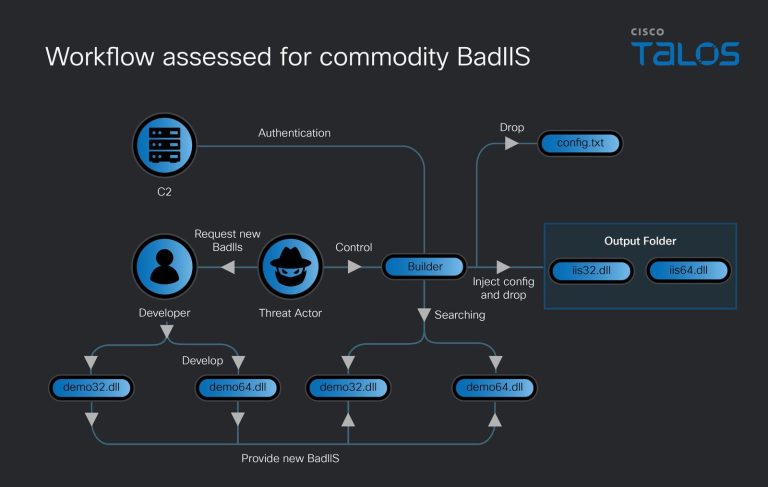
Cisco Talos exposes a commodity BadIIS variant sold as a service by dev "lwxat," featuring automated builders for traffic hijacking and reverse proxying.

Cisco Catalyst SD-WAN CVE-2026-20182 (CVSS 10) exploited in the wild. Attackers bypassing auth to seize admin control. Upgrade your network fabric now!
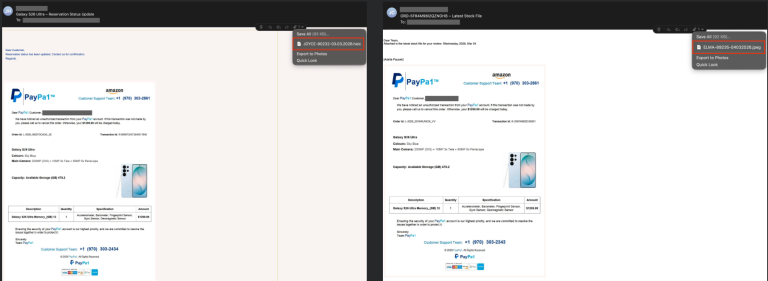
Cisco Talos reveals the rise of TOAD attacks. 55% of scam campaigns now use VoIP "anchors" to bypass email filters and trick victims into calling fraud centers.

Cisco Talos exposes Pheno, a malware plugin that hijacks Microsoft Phone Link to steal SMS and 2FA codes without touching your phone. Secure your PC today!
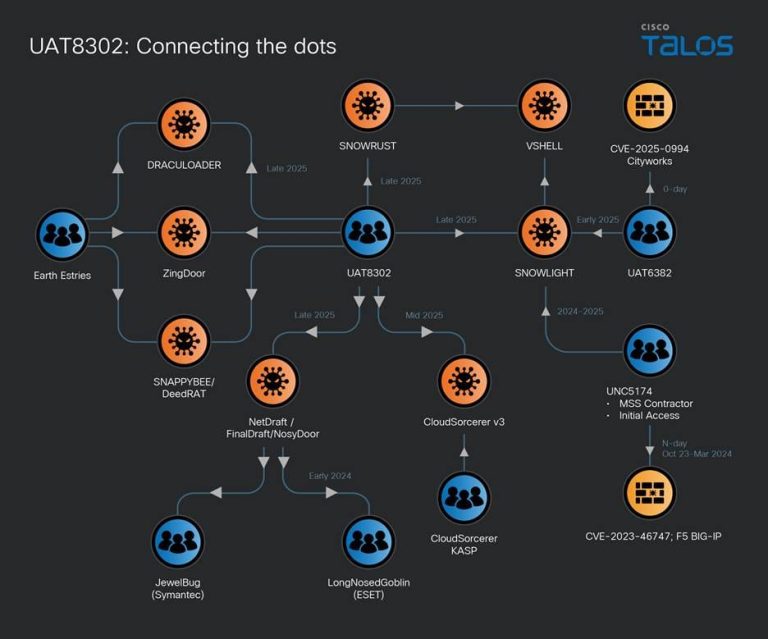
Cisco Talos exposes UAT-8302, a China-linked APT group infiltrating governments via NetDraft and CloudSorcerer. Learn how they share tools with notorious APTs.
Cisco Talos uncovers the FIRESTARTER backdoor in Arcane Door's latest attack on Firepower devices. Patch CVE-2025-20333 now to stop state-sponsored espionage.
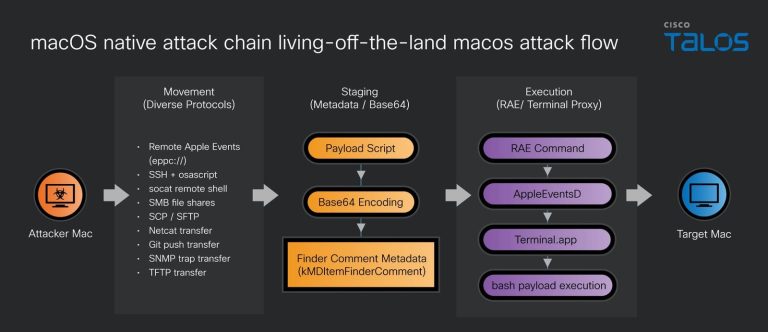
Cisco Talos reveals how attackers use native macOS features like Spotlight and SNMP to hijack enterprise workstations. Secure your DevOps environment today.
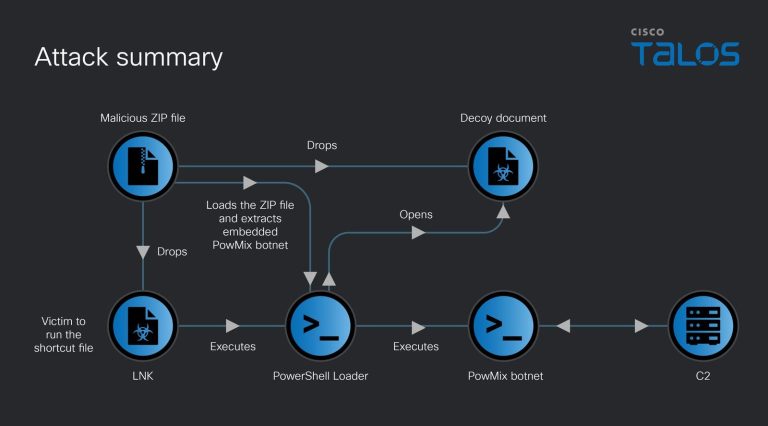
Cisco Talos uncovers PowMix, a stealthy botnet targeting Czech HR via AMSI bypass and Heroku-hosted C2. Learn how this malware evades modern EDR systems.

Cisco Talos reveals UAT-10362’s "Lucid" malware family targeting Taiwan. Using Lua, Rust, and regional locks, this threat prioritizes extreme stealth.

Cisco Talos exposes "Platform-as-a-Proxy" (PaaP). Hackers are abusing GitHub and Jira's trusted mail servers to bypass SPF/DKIM and deliver phishing lures.
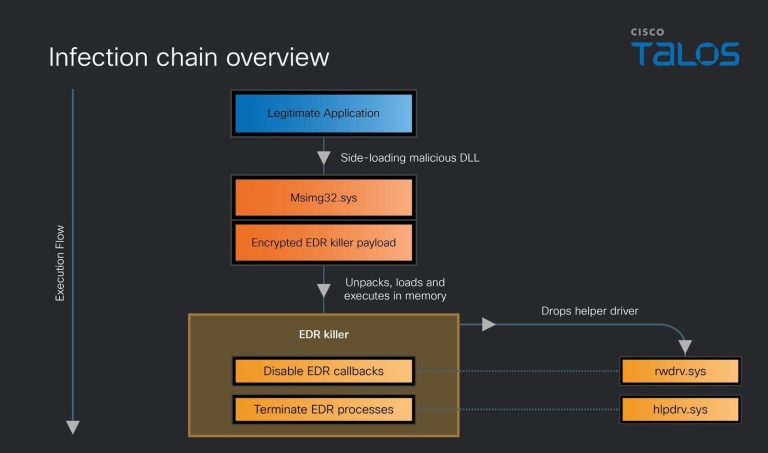
Cisco Talos unmasks a Qilin ransomware payload that terminates 300+ EDR drivers and manipulates the Windows kernel. See how this "EDR Killer" stays invisible.