 Do Son
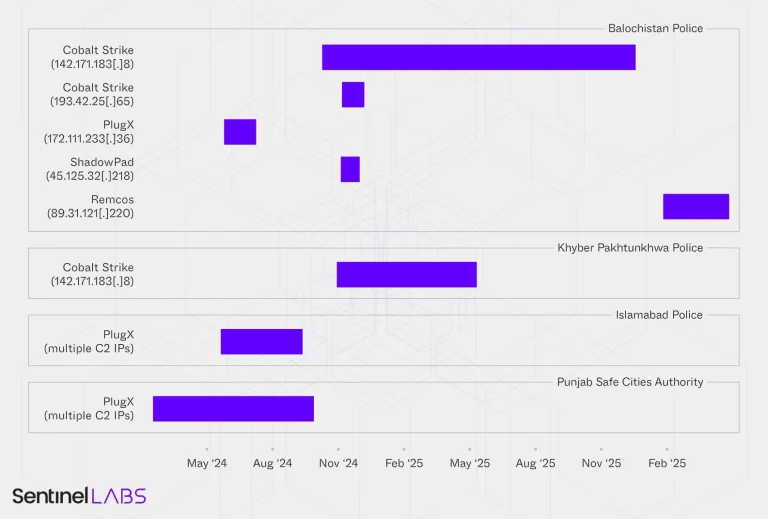
SentinelLABS found Chinese cyberespionage and India-nexus actors converging on Pakistani law enforcement, hitting Balochistan Police records and citizens.
Cobalt Strike
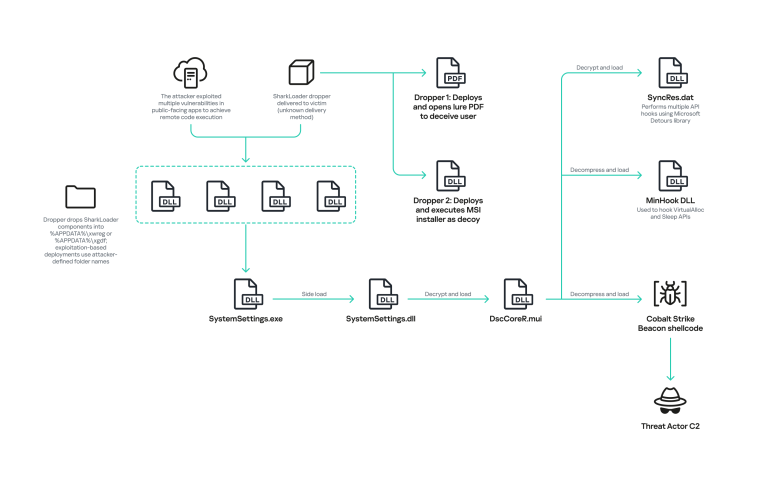
Kaspersky details SharkLoader malware, which deploys Cobalt Strike Beacon in the global StrikeShark campaign via DLL sideloading and exploited apps.
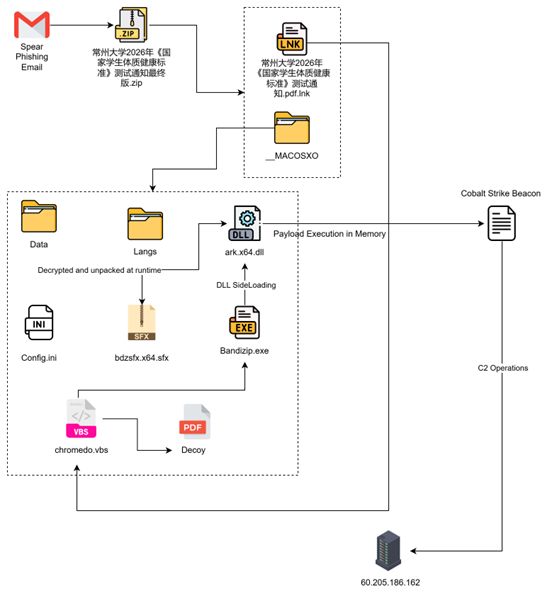
Discover how the Operation Dragon Whistle phishing campaign leverages student fitness lures to deploy stealthy memory-only malware.
CYFIRMA uncovers an elite stealth framework hijacking signed Intel utilities via AppDomain Manager. It targets EMEA finance with undetectable memory-only code.

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.

Lotus Blossom hijacked Notepad++ updates to target admins. The supply chain attack deployed Chrysalis backdoor. Update to v8.9.1 immediately.
Group-IB reveals ShadowSyndicate is evolving. The cybercrime cluster now rotates SSH keys to hide its infrastructure. Is it a BPH or IAB?

Darktrace dissects SnappyBee (Deed RAT), a stealthy Salt Typhoon backdoor. Learn how it uses DLL side-loading & memory hooking to evade modern AV.

New "cloud-first" malware VoidLink targets Linux & containers with advanced stealth. Written in Zig, it mimics Cobalt Strike to evade EDR. Check your cloud.

Operation FrostBeacon targets Russian B2B with Cobalt Strike. The dual attack uses LNK files and chained legacy exploits (CVE-2017-0199/11882) to gain persistent, financially motivated access.

ASEC confirmed Kinsing is exploiting Apache ActiveMQ RCE (CVE-2023-46604) to deploy XMRig cryptominer. The group now integrates Sharpire, Cobalt Strike, and Meterpreter for advanced post-exploitation.

Cisco Talos exposed UAT-8099, a Chinese group compromising IIS servers for SEO fraud, using BadIIS malware and Cobalt Strike to steal credentials and manipulate search rankings.

A JPCERT/CC report reveals a new attack campaign using CrossC2 and a custom loader to compromise both Linux and Windows systems.

Kaspersky exposes a stealthy cyberespionage campaign targeting Russian IT firms and global businesses, using DLL hijacking, social media C2, and obfuscation to deploy Cobalt Strike.

JPCERT/CC details a sophisticated, ongoing malware campaign exploiting Ivanti Connect Secure (CVE-2025-0282, -22457) using MDifyLoader, Cobalt Strike, vshell, and Fscan for stealthy persistent access.
Kaspersky uncovers a sophisticated APT41 cyberespionage campaign targeting African government IT, showcasing the Chinese group's full TTPs, including Impacket and Cobalt Strike.

Proofpoint reveals a surge in China-aligned cyber espionage targeting Taiwan's semiconductor industry with spearphishing, Cobalt Strike, and new malware like Voldemort.

Trellix has uncovered SquidLoader, a highly obfuscated malware targeting Hong Kong financial institutions to deploy Cobalt Strike beacons for persistent control.

BlackSuit, a rebranded Royal/Conti ransomware, unleashes destructive multi-stage attacks. It uses Cobalt Strike, rclone for data exfil, and deletes shadow copies for stealth and speed.

Symantec reports a Fog ransomware attack on an Asian bank that used unusual tools like employee monitoring software and an APT-linked backdoor, suggesting possible espionage.

A trojanized KeePass installer is spreading malware! Learn how this sophisticated attack steals credentials and deploys Cobalt Strike.

Swan Vector cyber-espionage campaign uses sophisticated malware to target institutions in Japan and Taiwan. Learn how they evade detection and steal data