 Do Son
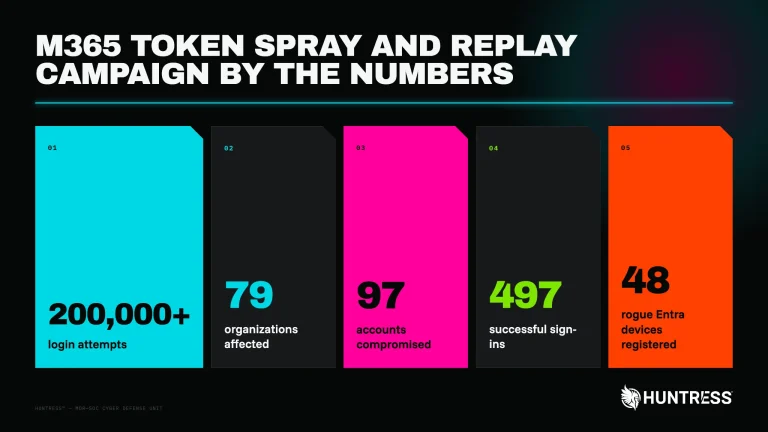
A token replay attack hit 79 organizations, bypassing MFA to set up Microsoft 365 BEC with rogue devices and hidden inbox rules.
Conditional Access
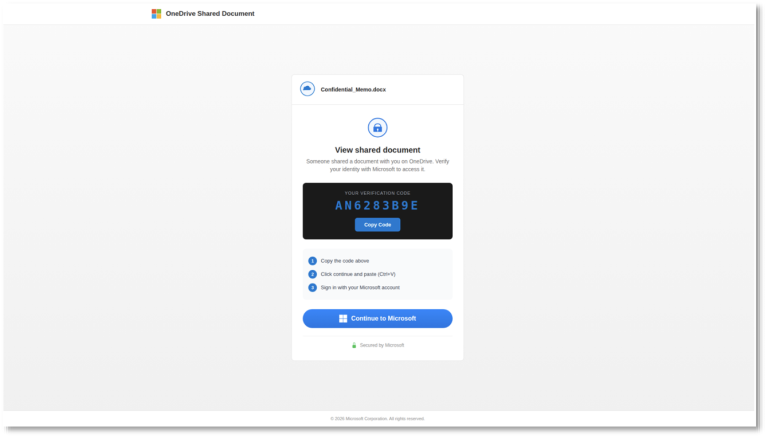
AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!

"ConsentFix" phishing tricks users into pasting OAuth codes from Azure CLI, bypassing MFA and Conditional Access. Detect this "fix" scam now.