 Do Son
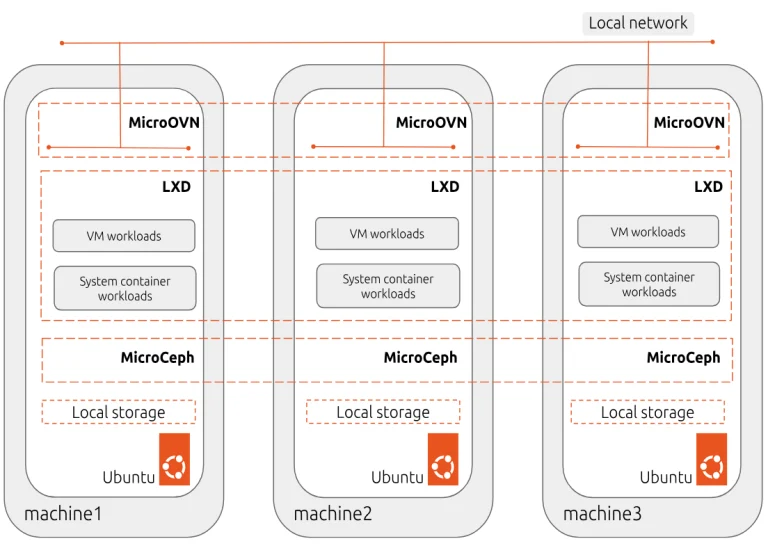
Canonical fixes LXD vulnerability CVE-2026-112816 (CVSS 10) in LXD and MicroCloud, letting attackers impersonate trusted TLS clients. Update now.
container security
Two critical Portainer vulnerabilities enable a bind mount bypass and Docker host takeover by standard users. Upgrade to Portainer 2.45.2 now.
A CVSS 10.0 Podman vulnerability, CVE-2026-94603, lets container images disable sandboxing in podman run. Upgrade to Podman 6.1.3 or 5.8.8 now.
Three critical LXD vulnerabilities, including CVE-2026-87799 (CVSS 9.9), let container users write files as root on the host. Patch to 5.21.8 or 6.10.
CVE-2026-77176 lets a malicious operator mount arbitrary guest rootfs paths in Kata Containers Confidential Containers. Upgrade to Kata 4.1.0.

CVE-2026-17106 (CVSS 7.1) is the Docker CopyEscape vulnerability, letting malicious containers overwrite host files and trigger code execution.

CVE-2026-44945 lets a default Rancher user gain full admin control via cross-cluster impersonation. Privilege escalation rated CVSS 9.1.

Six Incus vulnerabilities, all rated CVSS 9.9, are fixed in v7.2.0. CVE-2026-48769 and CVE-2026-48755 enable root attacks. Update now.

Three containerd critical vulnerabilities, including CVE-2026-53492, allow attackers to execute host commands and poison image caches. Patch immediately.

SUSE Rancher v2.14.1 fixes an 8.4 CVSS path traversal flaw (CVE-2026-25705) in UI Extensions. Prevent binary hijacking and host access—upgrade immediately!
A high 8.8 CVSS flaw (CVE-2026-3288) in ingress-nginx allows arbitrary code execution and massive Kubernetes secret leakage. Patch immediately.

CVSS 10.0 Alert: Kubernetes Local Path Provisioner flaw (CVE-2025-62878) allows host file overwrites. Upgrade to v0.0.34 immediately.

High-severity Rancher CLI flaw (CVE-2025-67601) exposes credentials via MitM attacks when using --skip-verify. Update or use -cacert immediately.

Critical Ingress-Nginx flaws (CVE-2026-1580) allow RCE and secret theft via config injection. Upgrade to v1.13.7 or v1.14.3 immediately to secure K8s.

New "cloud-first" malware VoidLink targets Linux & containers with advanced stealth. Written in Zig, it mimics Cobalt Strike to evade EDR. Check your cloud.

OCI patched three critical runc flaws allowing container escape and host DoS/RCE. Attackers exploit mount race conditions in maskedPaths and /dev/console bind-mounts. Update to v1.2.8+.
SUSE patched a Critical RCE flaw (CVE-2025-54469, CVSS 10.0) in NeuVector Enforcer that allows attackers to inject commands via unsanitized environment variables, risking container root shell access.

A high-severity flaw (CVE-2025-9566) in Podman allows malicious containers to overwrite host files via a symlink traversal attack. A patch is available in Podman v5.6.1.

A critical flaw in NeuVector (CVE-2025-8077) allows attackers to bypass authentication with a hardcoded password, exposing Kubernetes clusters to full compromise.

A critical vulnerability (CVSS 9.3) in Docker Desktop could allow malicious containers to gain full control of the host system. Update now to version 4.44.3.

A year after its discovery, the XZ backdoor remains in multiple Docker Hub images, posing a risk to developers and the software supply chain.
Trend Micro reveals misconfigured Kubernetes containers in AWS EKS can expose sensitive AWS credentials via unencrypted HTTP API, leading to privilege escalation risks.