 Do Son
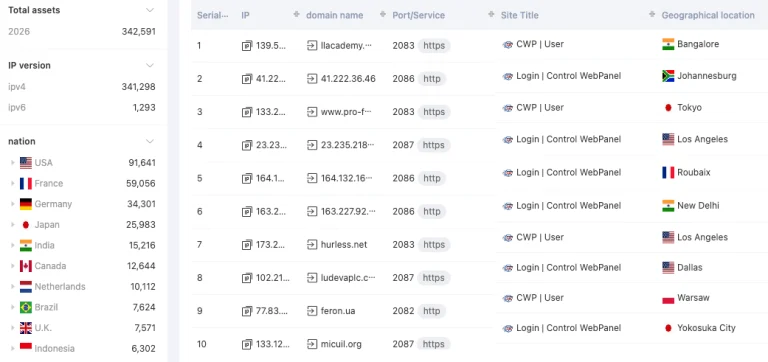
QiAnXin XLab uncovers the cwpdoor backdoor on Linux servers. See how the Control Web Panel cwpdoor backdoor hides in cwpsrv and suppresses access logs.
Control Web Panel
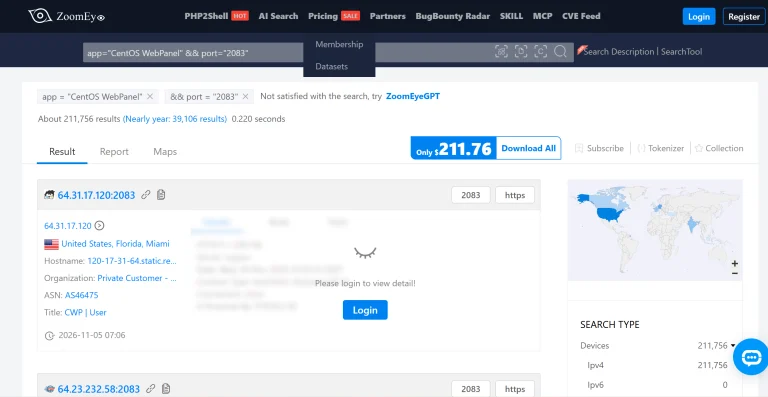
Update Control Web Panel to version 1.29 now to patch CVE-2026-73695, CVE-2026-73696, and eight other flaws allowing unauthenticated root RCE.
A public PoC is available for CVE-2026-57517, a critical CVSS 9.8 Control Web Panel SQLi flaw allowing unauthenticated remote code execution.

Fenrisk releases full PoC exploit for CVE-2025-48703, a critical CWP RCE flaw. Learn how unauthenticated attackers hijack non-root users. Patch now!
CISA added two critical, actively exploited flaws to its KEV Catalog: Gladinet LFI (CVE-2025-11371) risks RCE via machine key theft, and CWP RCE (CVE-2025-48703) allows unauthenticated admin takeover.

CVE-2023-42121 allows remote attackers unbridled access to execute arbitrary code on affected installations of the Control Web Panel

Successfully exploiting CVE-2022-44877 allows a remote attacker to gain full remote code execution on the server.