
 Do Son
Kaspersky uncovered the new HoneyMyte CoolClient rootkit. The HoneyMyte CoolClient rootkit deploys a kernel driver to hide malware on Windows.
Coolclient
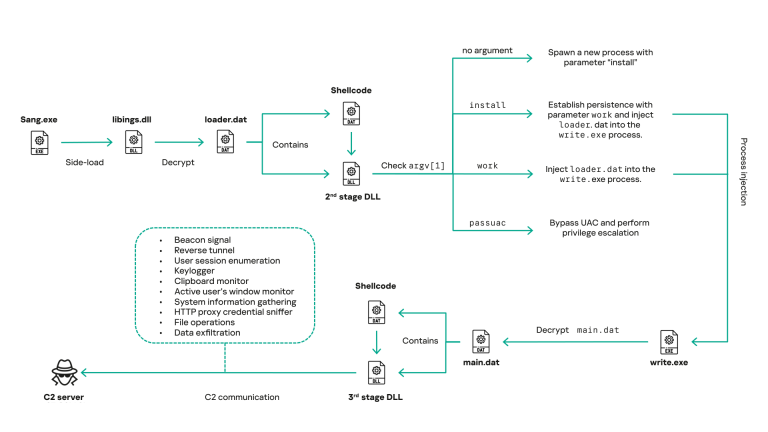
HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.

The perpetrators, utilizing tools linked to various Chinese espionage groups, have successfully penetrated these telecom networks