 Do Son
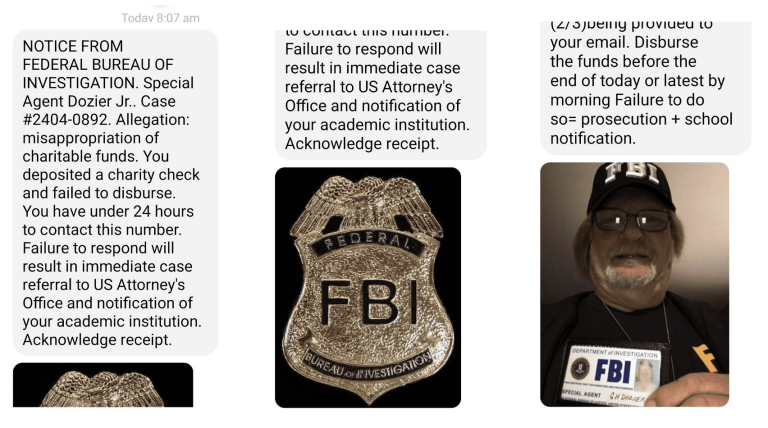
University job scams are spreading through .edu account takeover. Proofpoint shows how fraudsters phish logins, then send fake jobs and bogus checks.
Credential Phishing
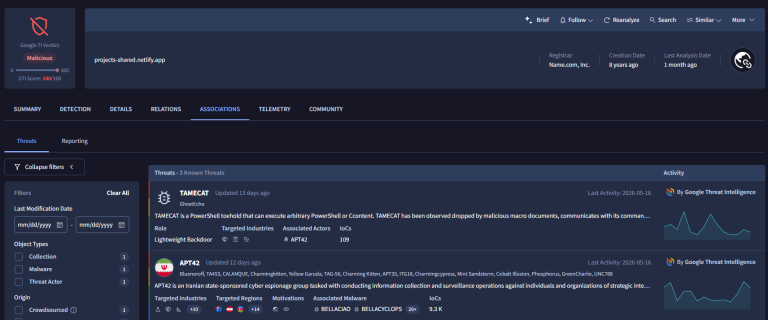
APT42 TAMECAT malware now blends AI-assisted phishing with cloud C2 to steal credentials from defense and nuclear-sector targets.
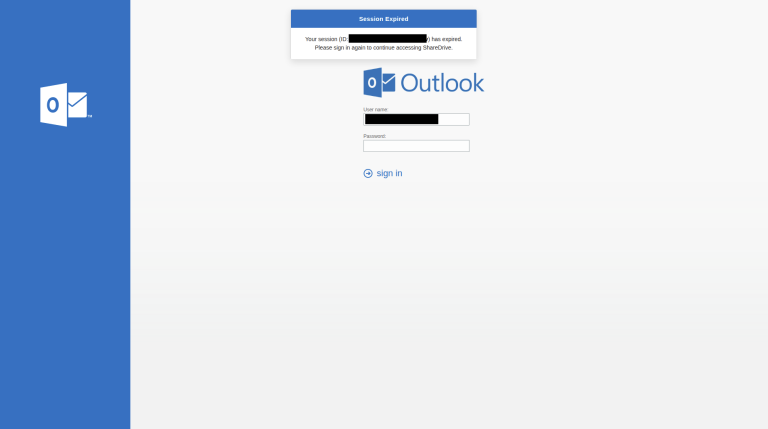
Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.

Microsoft blocked a credential phishing campaign that used AI to generate complex, verbose code in an SVG file to obfuscate its payload and evade defenses.

Cofense Intelligence reports a new phishing tactic using blob URIs to bypass Secure Email Gateways. Attackers use these local URIs to hide phishing pages.

The CoGUI phishing kit uses advanced evasion to target Japan with high-volume campaigns impersonating Amazon, PayPay, and more.

A new "Pick Your Poison" phishing campaign tricks users into choosing between having their credentials stolen or infecting their systems with malware. Cofense analysis reveals how this double-edged attack uses files.fm to deliver malicious payloads.