
 Do Son
Google Chrome patches 79 vulnerabilities, including 14 "Critical" RCE threats. Update to version 148.0.7778.167 now to protect your data and browser.
Critical Vulnerability

Juniper Networks warns of a critical 9.8 CVSS root vulnerability (CVE-2026-21902) in PTX Series routers. Unauthenticated attackers can gain complete control.
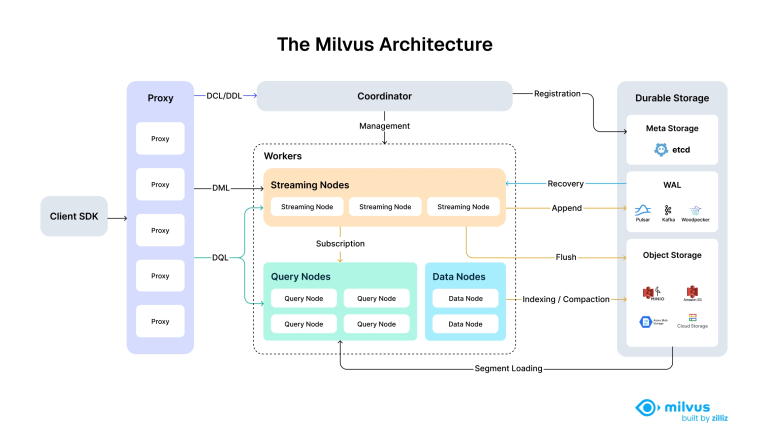
Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.

HPE Aruba patches critical Private 5G Core flaws. CVE-2026-23595 allows unauthenticated admin creation. Update to v1.25.1.0 now to prevent takeover.

IBM warns of critical flaw CVE-2025-13375 (CVSS 9.8) in CCA software. Unauthenticated attackers can hijack HSMs. Update to v7.5.53/v8.4.84 now.

Moxa warns of critical auth bypass (CVE-2024-12297, CVSS 9.2) in industrial switches. Flaw allows brute-force attacks. Patch TN-series devices now.

Critical ASUSTOR ADM flaw CVE-2026-24936 (CVSS 9.5) allows remote file overwrite. Unauthenticated attackers can seize NAS control. Update to v5.1.2 now.

CISA warns of CVSS 10 flaw CVE-2025-26385 in Johnson Controls Metasys. Remote SQL execution possible. Patch now or close TCP port 1433.
CVSS 10 flaw CVE-2026-23830 in SandboxJS allows RCE via unpatched Async functions. Attackers bypass all limits. Update to v0.8.26 immediately.
Critical ibaPDA flaw CVE-2025-14988 (CVSS 9.8) exposes industrial systems to file tampering. Update to v8.12.1 or harden settings now.

Critical n8n RCE (CVE-2026-1470) lets attackers bypass sandbox defenses via malicious expressions. CVSS 9.9. Check versions 1.123.17 & 2.x now.

CVSS 9.8 vm2 flaw (CVE-2026-22709) affects 3.7 million users, allowing total sandbox escape via async functions. Update to v3.10.2 immediately.

Open5GS WebUI vulnerability CVE-2026-0622 uses the default secret "change-me," allowing attackers to forge admin tokens. Patch now or update your keys.

RondoDox botnet targets HPE OneView with 40k attacks in 4 hours. Critical RCE CVE-2025-37164 allows full system takeover. Patch immediately.

Urgent: Siemens Edge flaw CVE-2025-40805 (CVSS 10) allows remote account takeover. Update SIMATIC & IOT2050 devices immediately to secure ops.
Critical Advantech flaw CVE-2025-52694 (CVSS 10.0) allows remote SQL injection. Unauthenticated attackers can seize control. Update IoTSuite now.

Critical alert: Undertow CVE-2025-12543 (CVSS 9.6) exposes WildFly & JBoss to cache poisoning and hijacking via Host Header Injection. Patch now.

Critical flaw CVE-2025-60262 hits H3C wireless devices. A misconfigured FTP setting grants anonymous users root access. Check your firmware now.
Urgent: n8n CVE-2026-21877 (CVSS 10.0) allows full server compromise via Git node. Update to v1.121.3 now to prevent RCE and arbitrary file writes.

IBM issues a 9.8 critical alert for API Connect! CVE-2025-13915 allows unauthenticated remote access. Update to v10.0.11 or apply iFixes now.

CISA warned of a Critical (CVSS 9.4) flaw in D-Link DCS-F5614-L1 cameras. Missing Authentication allows attackers to bypass login, steal admin credentials, and hijack video feeds. Patch immediately.

A Critical RCE (CVSS 10.0) flaw, React2Shell, in React/Next.js's Flight protocol allows unauthenticated system takeover. North Korean and Chinese state actors are actively exploiting the deserialization bug.