 Do Son
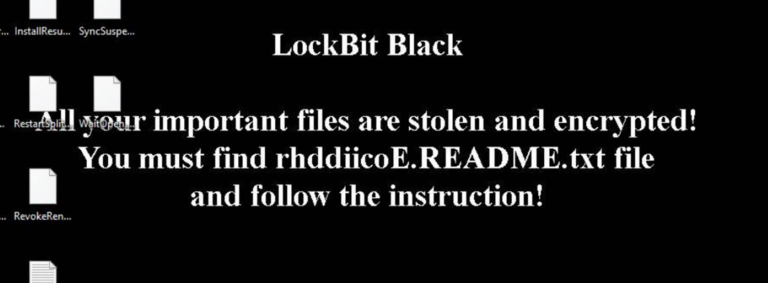
Uncover the details of the LockBit encryption attack using remote code execution vulnerabilities in Confluence. Learn more.
CVE-2023-22527

Learn about the recently disclosed Atlassian Confluence vulnerability and how attackers exploit it to hijack victim resources and conduct cryptomining activity on compromised systems.

Learn about the critical vulnerability CVE-2023-22527 in Atlassian Confluence. Find out how attackers exploit the flaw for cryptocurrency mining.

Arctic Wolf Labs uncovered threat actors are leveraging CVE-2023-22527 to deploy C3RB3R ransomware alongside a suite of other malicious payloads
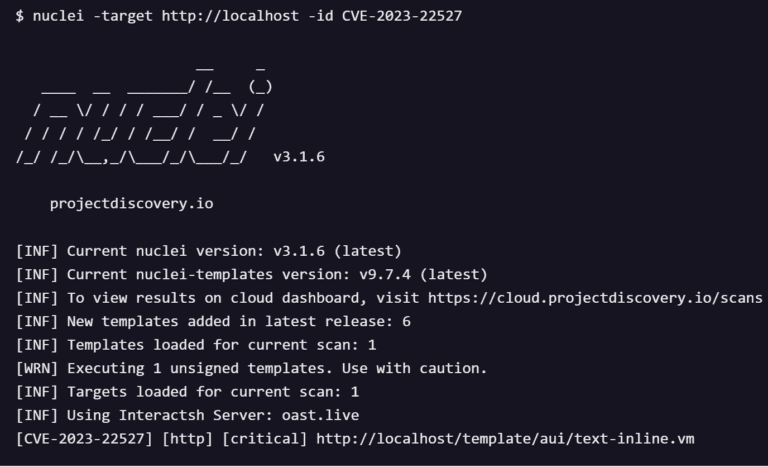
the researchers have created a nuclei template to detect CVE-2023-22527, CVSS score of 10.0, signifies maximum severity

CVE-2023-22527 vulnerability, with a CVSS score of 10, signifies the highest level of severity in the realm of cybersecurity threats.