 Do Son
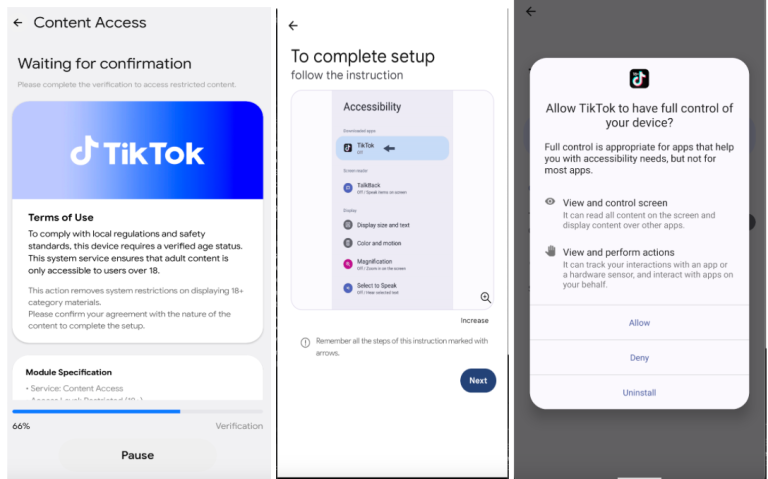
The Rokarolla Android banking trojan executes a complete device takeover. It targets 217 apps and steals credentials through fake overlays and keyloggers.
CVE-2023-35674
CVE-2023-35674 could significantly elevate local privileges, all without the need for any user interaction or additional execution privileges