
 Do Son
Uncover the cyberespionage campaign attributed to TAG-110. Learn about the Russia-aligned threat group targeting organizations and their motives.
CVE-2024-23692

To mitigate the risk posed by CVE-2024-39943, users of HFS are strongly advised to update their software to version 0.52.10 or later
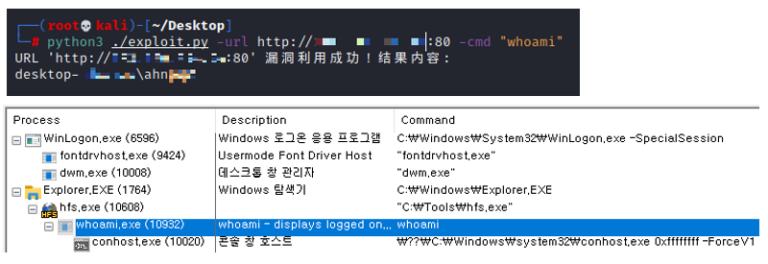
ASEC has observed a variety of attacks targeting HFS servers, including: Cryptomining, RATs and Backdoors, and Infiltration of GoThief malware
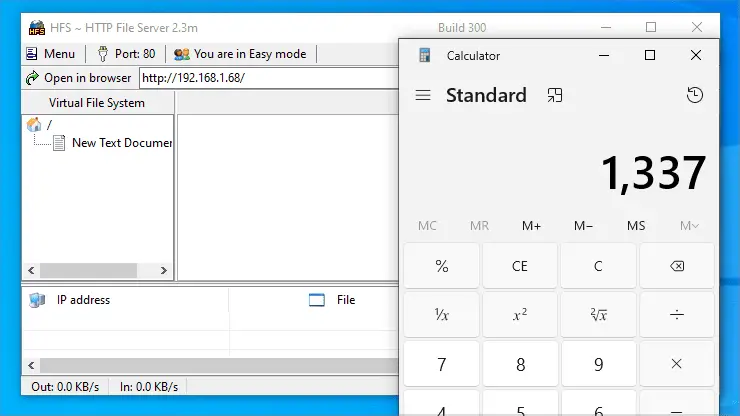
A critical vulnerability, identified as CVE-2024-23692, has been discovered in Rejetto HTTP File Server (HFS) versions 2.x