 Do Son
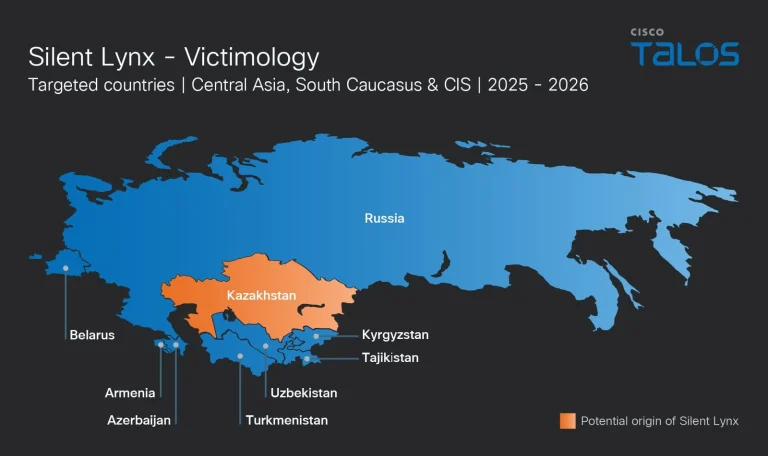
Cisco Talos and Recorded Future exposed the UAT-6275 threat actor targeting CIS governments with WinRAR exploits and custom reverse shells.
CVE-2025-8088
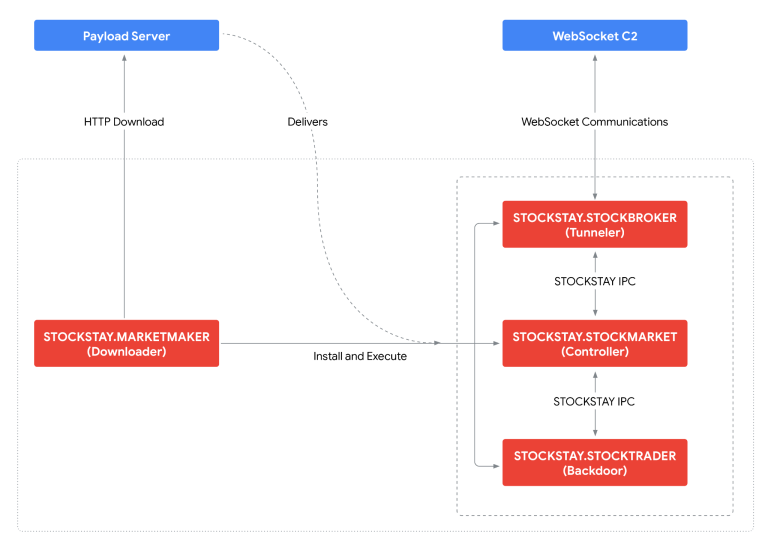
Turla STOCKSTAY backdoor attacks Ukrainian military targets. Russian cyber espionage groups deploy this .NET malware via malicious RDP and WinRAR flaws.

Gamaredon targets critical systems by exploiting WinRAR vulnerability CVE-2025-8088 to drop GammaDrop malware. Secure your entry points now!

Amaranth-Dragon (APT-41 nexus) weaponized WinRAR flaw CVE-2025-8088 in just 10 days. Southeast Asian govts targeted with malicious RAR archives.

Critical WinRAR flaw CVE-2025-8088 is exploited by spies & cybercriminals. "Zeroplayer" sells the exploit. Update to v7.13 to stop Startup folder attacks.

Intezer reveals EchoGather, a new Paper Werewolf backdoor using XLL files and AI-generated decoys to target Russian defense and high-tech firms.

ESET warns of an actively exploited WinRAR zero-day (CVE-2025-8088). The path traversal flaw allows attackers to execute code by crafting malicious archives.