 Do Son
CVE-2026-48558, a SimpleHelp authentication bypass, is exploited in the wild to deploy TaskWeaver and Djinn Stealer. CISA added it to KEV. Patch now.
CVE-2026-48558
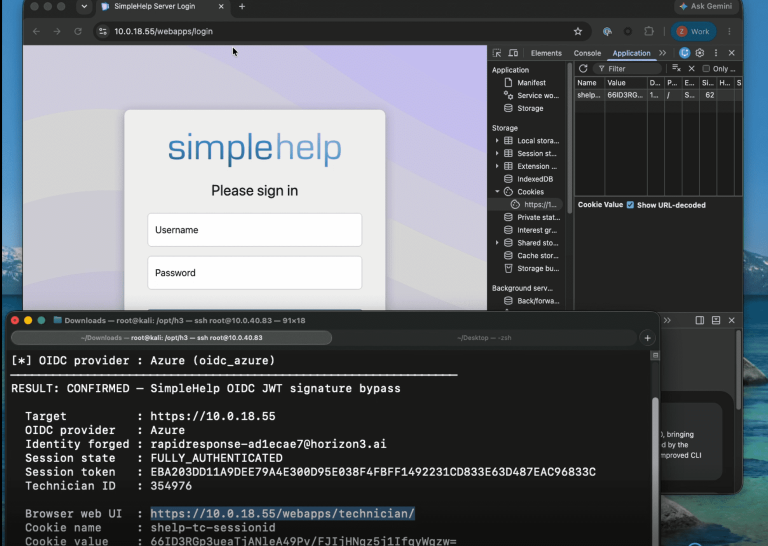
A critical SimpleHelp authentication bypass flaw leaves servers open. Attackers exploit the OIDC authentication flow to gain technician control.