 Do Son
An attacker targeted GitLab vulnerability CVE-2026-97229 (CVSS 10 RCE) on Alpine Linux's server. Alpine rebuilt GitLab and reset all passwords.
CVE-2026-97229
Ruby security update 4.0.9, 3.4.12 and 3.3.13 fixes Onigmo regex bugs behind GitLab RCE flaws CVE-2026-110264 and CVE-2026-97229. Upgrade now.
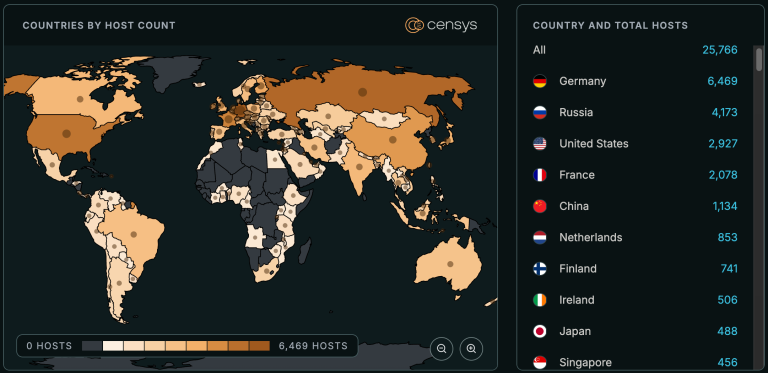
Technical details and PoC exploit code for CVE-2026-97229, a CVSS 10.0 GitLab RCE vulnerability exposing 25,766 hosts, are now public. Patch to 19.4.2 now.
A GitLab critical vulnerability, CVE-2026-97229 (CVSS 10.0), allows unauthenticated arbitrary code execution. Upgrade to GitLab 19.4.2 now.