Public PoC Exploit Disclosed for CVSS 10.0 GitLab Remote Code Execution Flaw CVE-2026-97229 Affecting 25,766 Hosts
 Do Son
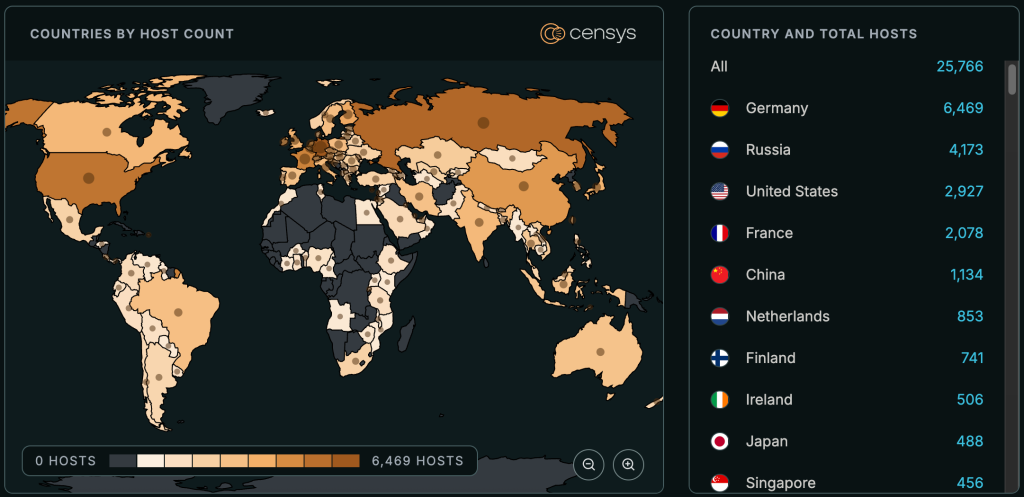
Image: Censys
TL;DR
GitLab patched CVE-2026-97229, a maximum-severity (CVSS 10.0) integer overflow flaw in its CI/CD regular expression compiler. Shortly after the patch, Rapid7 researchers publicly disclosed technical details and proof-of-concept exploit code for this critical GitLab RCE vulnerability. Meanwhile, Censys estimates that 25,766 internet-facing hosts and 79,224 web properties currently run vulnerable versions.
- CVE: CVE-2026-97229
- CVSS: 10.0 (Critical · CVSSv3)
- Product: GitLab
- Affected: 19.2, 19.3, 19.4
- Impact: Integer Overflow or Wraparound in GitLab
- Status: No confirmed exploitation yet
- Patched in: 19.2.8, 19.3.5, 19.4.2
- EPSS: 0.6% (30-day)
- Action: Update to 19.2.8, 19.3.5, 19.4.2 now
Why CVE-2026-97229 Matters for DevSecOps Teams
According to the Censys exposure advisory for CVE-2026-97229, 31% of 82,454 detected GitLab hosts run an unpatched release. Germany (6,469 hosts), Russia (4,173), and the United States (2,927) account for the largest concentrations of exposed instances. Furthermore, researchers published a public CVE-2026-97229 proof-of-concept repository on GitHub on October 13, 2026. Although a working PoC is now public, neither GitLab nor Censys has confirmed active exploitation in the wild, and the flaw is not listed in the CISA KEV catalog.
How the GitLab RCE Attack Works
Onigmo Regex Compiler Integer Overflow
To set up the attack, an ordinary user first commits a crafted .gitlab-ci.yml configuration file and a UTF-8 repository path to a public project branch. Afterward, an unauthenticated attacker can trigger the CI lint endpoint against that branch reference without credentials. Specifically, the exploit embeds an inline comment inside a quantifier to evade GitLab’s repeat scanner and initial US-ASCII size checks.
Ruby VM Stack Redirection
When the CI linter evaluates the rule against the UTF-8 repository path, Ruby’s Onigmo regular expression engine recompiles the expression for the new encoding. Consequently, an integer overflow occurs in the compiler’s program-size calculation and generates invalid bytecode instructions. Attackers can redirect the Onigmo virtual machine stack to bypass ASLR and execute arbitrary operating system commands as the git user.
Affected GitLab Versions
While GitLab.com is already patched, self-managed GitLab Community Edition (CE) and Enterprise Edition (EE) installations are vulnerable across three branches:
- GitLab 19.2.0 through 19.2.7
- GitLab 19.3.0 through 19.3.4
- GitLab 19.4.0 through 19.4.1
Patch Details and Mitigation Steps
Administrators should review the official GitLab 19.4.2 patch release announcement and upgrade to versions 19.4.2, 19.3.5, or 19.2.8 immediately. If teams cannot patch this GitLab RCE vulnerability right away, they should restrict inbound network access to the GitLab web interface and disable untrusted public project creation.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
