 Do Son
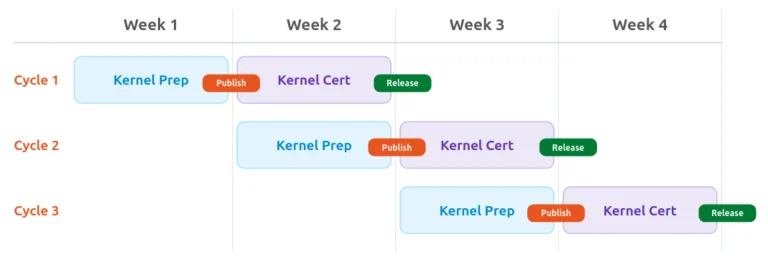
Learn why Canonical accelerated Ubuntu kernel updates. A surge in CVEs prompted a shift to an overlapping two-week SRU cycle for faster vulnerability patching.
CVE
Critical MongoDB driver vulnerabilities, including CVE-2026-93762, expose systems to data loss and DoS. Learn about these flaws and patch immediately.
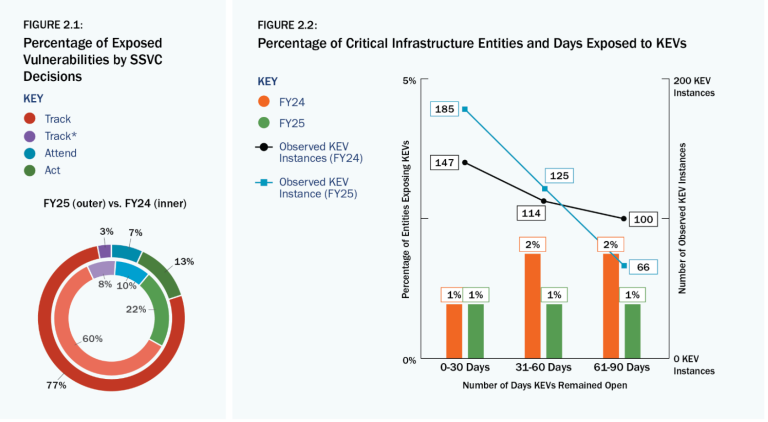
The CISA Vulnerability Review finds known exploited vulnerabilities and decades-old software flaws drive most compromises across FY2024 and FY2025.

Apache NiFi vulnerabilities, including CVE-2026-68979, CVE-2026-62354, and CVE-2026-68981, expose users to code execution and resource consumption.
Linux kernel CVEs surged to 440 advisories in just 24 hours, with many flaws found by AI. Most are already patched, so update your kernel promptly.

Read our mid-July weekly threat intelligence report. Stay informed on active vulnerability updates, Fortinet flaws, and CISA KEV additions.
Recent NVIDIA security updates address critical vulnerabilities, including CVE-2025-23351. Apply patches to secure your ConnectX and BlueField devices.

This weekly CVE report covers 1,909 new vulnerabilities from June 22-28, 2026. CISA flagged six as exploited, including CVE-2026-20230.

This weekly CVE report covers 2,060 new vulnerabilities from June 15-21, including 358 critical flaws and 4 actively exploited CVEs now in CISA KEV.

Two critical FreePBX RCE vulnerabilities in Superfecta and UCP modules expose servers to authenticated arbitrary code execution and command injection.

Read our weekly threat intelligence briefing. This active vulnerability management report covers June 2026 CISA KEV additions and new zero-day exploits.

Kaspersky reports a record surge in CVEs for Q1 2026. Discover how AI-driven exploits, authentication bypasses, and new C2 trends are reshaping cyber defense.

Angular patches a critical 8.7 SSRF flaw in @angular/platform-server. Attackers can hijack SSR origins via URL normalization. Patch v19, v20, or v21 now!

Faced with a massive surge in CVEs, NIST has overhauled the NVD. Starting April 2026, only high-risk flaws get full analysis. Check the new triage rules.

A Notepad++ flaw (now patched in v8.8.9) allowed attackers to hijack the WinGUp update process, serving malware instead of the legitimate executable. Manual update is urged.

 ddos-admin
Introducing CVE Watchtower: your go-to service for real-time intelligence on security vulnerabilities in the cybersecurity landscape.

Two critical vulnerabilities (CVSS 10 & 9.8) in Digiever NVRs allow unauthenticated attackers to steal credentials and execute commands. Update your firmware immediately.
A critical Angular SSR vulnerability (CVE-2025-59052) could expose user data. Learn about the flaw, affected versions, and how to protect your application.

Critical design flaws in Workhorse Software's municipal accounting platform could allow unauthenticated users to download full database backups with sensitive PII and financial records.

A new vulnerability in AMI Aptio UEFI firmware allows for arbitrary code execution in System Management Mode, a privileged environment that can bypass OS controls.

A critical directory traversal vulnerability (CVE-2025-48387) in the popular NPM package tar-fs allows attackers to write arbitrary files and gain RCE.

A new security update for PostgreSQL fixes three vulnerabilities, including two critical flaws that could lead to remote code execution.