
 Do Son
Critical SandboxJS flaws (CVSS 10.0) allow sandbox escape & host takeover via prototype pollution. Update to v0.8.29 immediately to stop code execution.
CVSS 10.0
CVSS 10.0 Alert: Kubernetes Local Path Provisioner flaw (CVE-2025-62878) allows host file overwrites. Upgrade to v0.0.34 immediately.

CISA warns of CVSS 10.0 flaw in Synectix LAN 232 TRIO. With no auth and the vendor gone, these devices are unpatchable. Replace immediately.
HPE issued an urgent alert for a CVSS 10.0 RCE in OneView. Attackers can seize unauthenticated control of data centers. Upgrade to v11.00+ now.

Developers using the modern stack of Next.js and React are facing a “red alert” situation today. A...

Grafana Enterprise released emergency patches for CVE-2025-41115 (CVSS 10.0), a critical flaw in SCIM provisioning that could allow attackers to impersonate high-privilege users.
CISA warned of four flaws in Lynx+ Gateway. The Critical (CVSS 10.0) Auth Bypass allows unauthenticated remote reset and cleartext credential theft. Vendor GIC has not responded to CISA.

CISA warned of three Critical flaws (CVSS 10.0) in Radiometrics VizAir weather systems. Unauthenticated attackers can manipulate wind shear alerts and runway configurations, risking hazardous flight conditions.

Ubiquiti issued an urgent patch for a Critical Auth Bypass flaw in UniFi Access. Attackers with network access can fully take over door management systems.

CISA warned of 9 flaws in AutomationDirect PLCs. The Critical RCE (CVE-2025-61934, CVSS 10.0) allows unauthenticated file manipulation on a simulator service. Patch to v4.5.0.x immediately.
SUSE patched a Critical RCE flaw (CVE-2025-54469, CVSS 10.0) in NeuVector Enforcer that allows attackers to inject commands via unsanitized environment variables, risking container root shell access.

Rockwell issued an urgent fix for a Critical (CVSS 10.0) auth bypass in its 1783-NATR router (CVE-2025-7328). The flaw allows remote admin takeover and configuration disruption.

A critical flaw (CVE-2025-41243) in Spring Cloud Gateway with a CVSS 10.0 score allows unauthenticated RCE via SpEL injection. A PoC has been released.
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
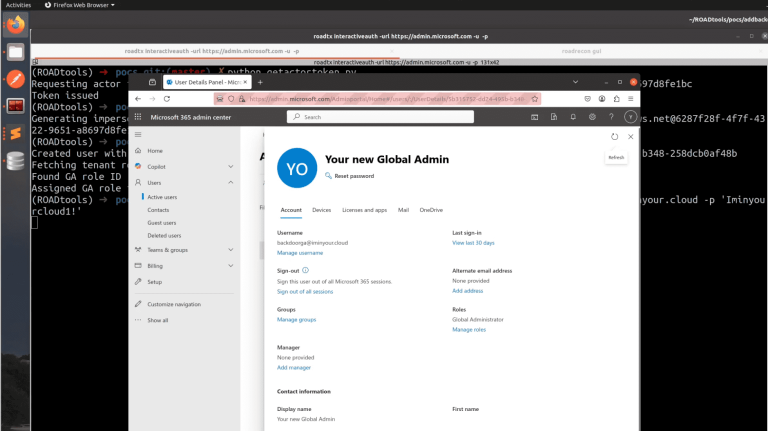
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
A critical flaw (CVE-2025-55241) in Microsoft Entra ID could have allowed a compromise of every tenant worldwide by bypassing security with "Actor tokens."

Today, SAP released 21 new Security Notes and 4 updates as part of its monthly Security Patch...

A critical flaw in Spring Cloud Gateway (CVE-2025-41243) has a CVSS 10.0 score. The bug allows property modification when actuator endpoints are exposed. Update now.

A critical vulnerability in Plex Media Server, with a CVSS score of 10.0, has been patched. Users are urged to update immediately to prevent exploitation.

A critical flaw (CVE-2025-41672, CVSS 10.0) in WAGO Device Sphere allows unauthenticated attackers full admin control via shared default JWT certificates. Update to v1.0.1 immediately!

Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.
Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.

Quest KACE SMA faces critical flaws, including a CVSS 10.0 auth bypass (CVE-2025-32975) allowing full admin control. Update immediately to prevent RCE and compromise.

A critical flaw (CVE-2025-52562, CVSS 10.0) in Convoy KVM panel allows unauthenticated remote code execution via directory traversal.