 Do Son
A critical MariaDB security flaw affects millions of servers. Learn about the 10.0 CVSS bug impacting recent community server releases.
CVSS 10.0

The Samba Team dropped fixes for critical Samba vulnerabilities. Read about the remote code execution flaws carrying perfect 10.0 CVSS scores.
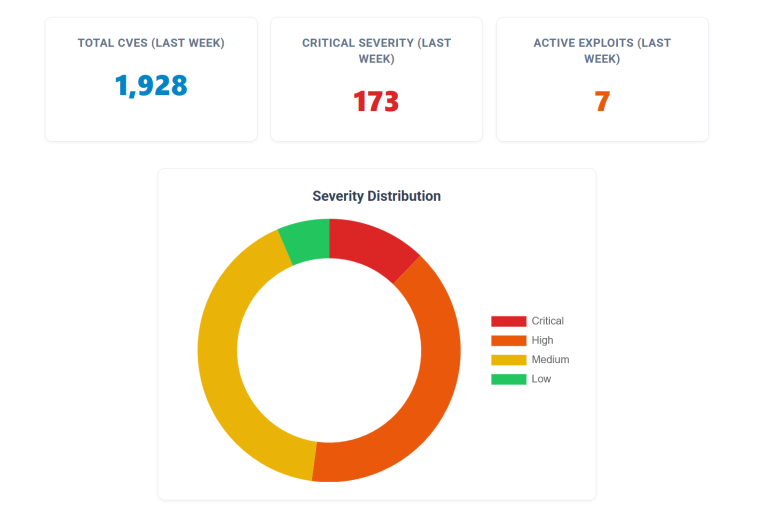
Weekly Security Digest: 1,928 new vulnerabilities hit the wire. From Palo Alto firewalls to LiteLLM AI gateways, here is how to prioritize your defense.
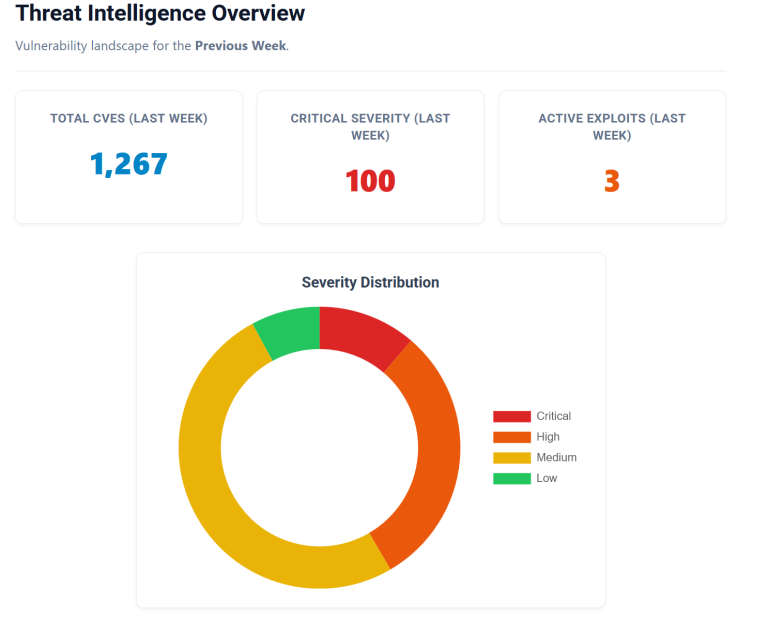
Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20,Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20, 2026. 2026.
Critical 10.0 CVSS flaw in Firebird Database allows RCE via path traversal in the engine loader. Attackers gain root/SYSTEM privileges. Patch to 5.0.4+ now.

Two critical CVSS 10.0 RCE flaws in Spinnaker's Clouddriver and Echo services allow full JVM and shell access. Patch your multi-cloud pipelines immediately.

Dgraph patches a critical 10.0 CVSS flaw (CVE-2026-33976). Unauthenticated attackers can overwrite databases and read local files. Update to v25.3.1 now!
Juju hits a perfect 10.0 CVSS score (CVE-2026-4370). A TLS flaw on port 17666 lets attackers hijack clusters. Update to 3.6.20 or 4.0.5 now!

CloudSEK warn of instant exploitation for Oracle WebLogic's CVE-2026-21962. With a 10.0 CVSS score, this RCE allows full server takeover. Patch now!
AVideo faces a security crisis with 5 unpatched critical flaws (CVSS 10.0). Attackers can hijack streams and execute code. Learn how to protect your server.
GeoVision fixes a critical 10.0 CVSS flaw in GV-Edge Recording Manager. CVE-2026-4606 allows local users to gain SYSTEM-level control. Update to V2.3.2 now.
A critical 10.0 CVSS flaw in WAGO managed switches (CVE-2026-3587) allows unauthenticated remote takeover via an undocumented CLI backdoor. Update immediately.

This week in cybersecurity: 1,348 new vulnerabilities discovered, including seven critical 10.0 CVSS flaws and the highly active DarkSword exploit chain.
Ubiquiti warns of a critical 10.0 CVSS Path Traversal flaw (CVE-2026-22557) in UniFi Network Applications allowing total system takeover. Patch immediately.
Google Chrome zero-days and a CVSS 10.0 building controller flaw top this week's 1,388 new CVEs. Patch the perimeter before threat actors automate the exploit.

A critical 10.0 CVSS flaw (CVE-2026-3611) in Honeywell IQ4x BMS controllers leaves web HMIs exposed without authentication. Secure your systems immediately.
A critical 10.0 CVSS zero-click flaw (CVE-2026-20079) in Cisco Secure FMC gives unauthenticated attackers root access. Patch your systems immediately.
A critical 10.0 CVSS flaw (CVE-2026-29000) in the pac4j-jwt library allows attackers to forge JWTs and bypass authentication. Patch immediately.
A critical 10.0 CVSS unauthenticated RCE flaw (CVE-2026-20131) in Cisco Secure FMC allows hackers root access via insecure Java deserialization. Patch now.
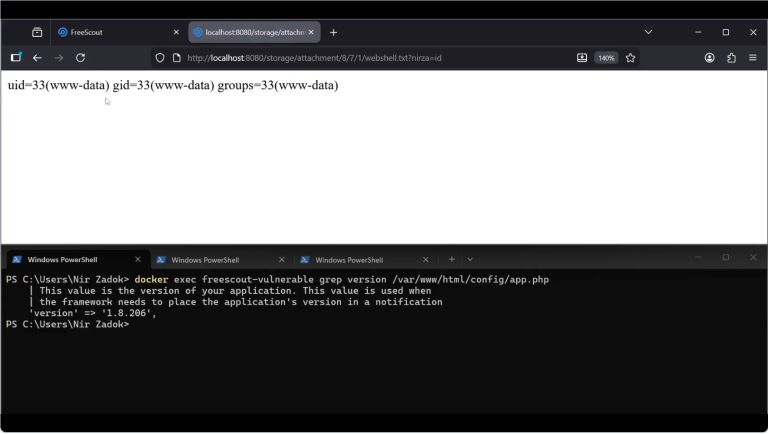
A critical 10.0 CVSS unauthenticated remote code execution flaw (CVE-2026-28289) in FreeScout allows full server takeover via an invisible character exploit.
Acronis fixes 3 critical flaws (CVSS 10.0) in Cyber Protect. Attackers can manipulate backups without auth. Update to v16 Update 4 immediately.

Microsoft warns of critical flaw CVE-2026-25592 (CVSS 10.0) in Semantic Kernel SDK. AI agents can overwrite system files. Update to v1.70.0 now.