
 Do Son
Patch CVE-2026-16338 immediately. Learn how this 9.9 CVSS flaw allows arbitrary file write attacks in IBM DataStage and how to secure your data today.
CVSS 9.9
A critical 9.9 CVSS IDOR flaw in Comet Backup allows complete cross-tenant account takeovers. Self-hosted administrators must patch servers immediately!
Jakob Wolffhechel reveals "Shittrix," 89 critical flaws in Citrix XenServer & XCP-ng. CVSS 9.9 bugs allow full host takeover. Assume compromise today.
Cisco alerts on a critical 9.9 CVSS flaw in ISE. Even "Read-Only" admins can escalate to root and trigger a total network lockout. Patch immediately.

Critical BeyondTrust flaw CVE-2026-1731 (CVSS 9.9) allows unauthenticated RCE on Remote Support & PRA appliances. Update to v25.3.2 immediately.

GitLab patches critical flaw CVE-2026-1868 (CVSS 9.9) in self-hosted AI Gateway. Vulnerability allows RCE via insecure templates. Update to v18.8.1 now.

Avaya CMS hit by CVSS 9.9 flaw allowing remote command execution via web request. Affected versions must upgrade to avoid system compromise.
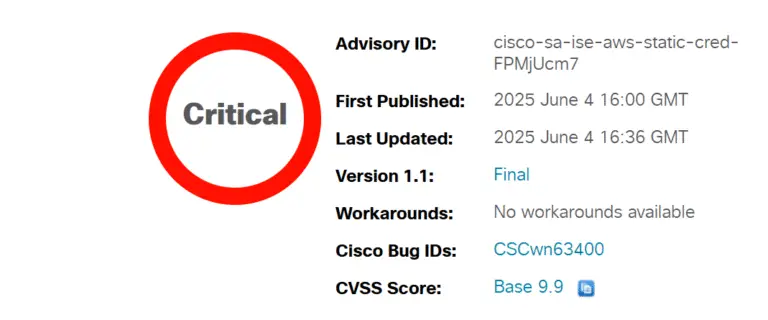
CVSS 9.9 flaw in Cisco ISE cloud deployments with public PoC exploit enables remote attacks on AWS, Azure, and OCI. Patch now.

Siemens RUGGEDCOM devices face CVSS 9.9 command injection flaws. Authenticated users can execute root-level code via web tools. Patch to V2.16.5 now.