
 Do Son
Microsoft exposes North Korea’s Jasper Sleet (Storm-0287) using AI-enhanced deepfakes and fake personas to secure remote IT jobs at 300+ US firms, funding the DPRK regime and stealing data.
Cybercrime

The DOJ dismantled a North Korean scheme exploiting remote IT jobs at 100+ U.S. firms, using stolen identities and laundering millions to fund DPRK weapons programs.

Trustwave exposes Blind Eagle (APT-C-36) leveraging exposed infrastructure and VBS malware in phishing campaigns, targeting Colombian banks with blatant disregard for concealment.

Europol and allies arrested 5, dismantling a global crypto investment fraud ring that laundered €460M from 5,000+ victims, exploiting Hong Kong banking networks.

Notorious hacker "IntelBroker" (Kai West) has been arrested, traced by the FBI through his crypto transactions. He's charged with stealing and selling data, causing $25M in damages.

Taiwan's BitoPro exchange confirms North Korea's Lazarus Group stole $11.5M in crypto via phishing an employee and bypassing MFA on AWS infrastructure.
A hacker is allegedly selling 16 billion login credentials, likely aggregated from past breaches via info-stealing malware, impacting major tech platforms. Use MFA to stay safe!

Qilin ransomware is rapidly dominating the RaaS landscape, as rivals like RansomHub and LockBit face collapse, internal chaos, and public defacements by "XOXO from Prague."

Hackers leaked 7.4 million Paraguayan citizen records on the dark web, demanding a $7.4M ransom. The breach likely stems from infostealer malware, sparking national security concerns.
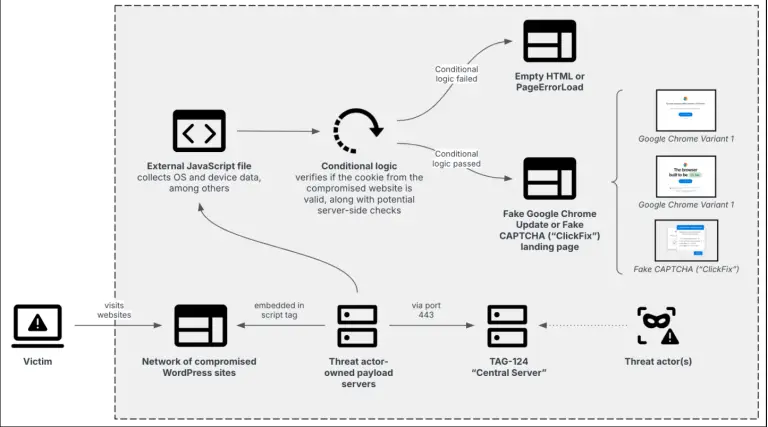
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.

Anubis, a new RaaS, combines ECIES encryption with a "wipe mode" that permanently destroys files. It's actively targeting healthcare, construction, and engineering sectors.

Infoblox unmasks VexTrio, a sprawling malicious adtech ecosystem intertwined with DNS-based malware campaigns and global website compromises, fueled by commercial operators
Attackers are hijacking expired Discord invite links, redirecting users to malicious servers that deploy AsyncRAT and crypto-stealing Skuld Stealer via clever social engineering.

Symantec reports a Fog ransomware attack on an Asian bank that used unusual tools like employee monitoring software and an APT-linked backdoor, suggesting possible espionage.

HelloTDS is a sophisticated traffic direction system delivering millions to FakeCaptcha and other malware via advanced fingerprinting and evasive tactics.

Interpol and Asian law enforcement blocked 20,000 malicious IPs and seized 41 servers in a major takedown of information-stealing malware infrastructure.

A new Sekoia report reveals a surge in AitM phishing, leveraging industrialized PhaaS kits to bypass MFA and compromise Microsoft 365 and Google accounts.

CyberEye, a modular .NET RAT, offers widespread data theft and surveillance using a builder, Telegram C2, and anti-analysis features, making it a new threat.

Rapid7 reveals BlackSuit ransomware affiliates are adopting Black Basta tactics, using email bombing, fake Quick Assist scams, and evolving Java RATs.

A new report reveals over 40,000 internet-connected security cameras are exposed online, streaming live footage without protection, risking privacy globally.
DanaBot's "DanaBleed" memory leak, active for 3 years, exposed C2 server data, aiding law enforcement in Operation Endgame takedown.

Silent Push uncovers "GhostVendors," a massive online fraud operation using 4,000+ fake domains and Facebook ads to impersonate brands and scam consumers.