
 Do Son
A new report reveals DSLRoot, a residential proxy network operated by a Belarusian national that uses hardware planted in U.S. homes, enabling foreign operators to bypass security.
Cybercrime
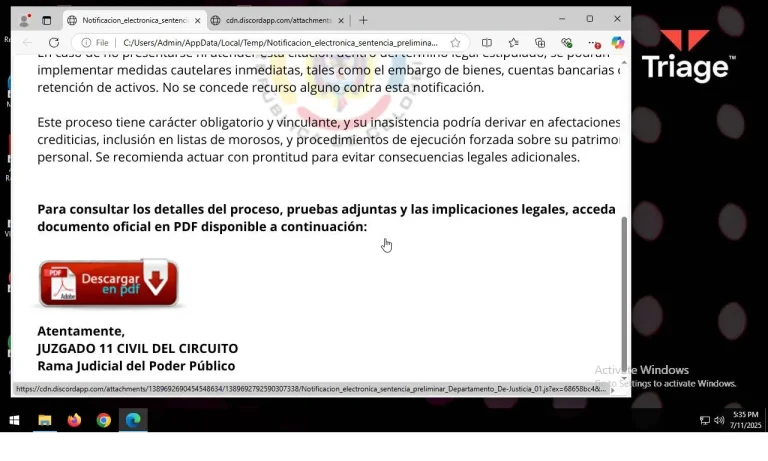
A new report reveals the Blind Eagle hacking group is using spearphishing and commodity RATs to conduct cyber espionage against Colombian government and private sector targets.

A new report reveals a mobile malware campaign in Indonesia impersonating the state pension fund TASPEN to steal financial and personal data from civil servants.

A new report reveals a widespread data theft campaign targeting Salesforce instances. Attackers used compromised OAuth tokens from a third-party app to steal data and credentials.

A new phishing campaign called ZipLine reverses the attack by tricking victims into initiating contact. It targets supply chains and deploys a custom in-memory implant.

A new report reveals a SpyNote Android RAT campaign using fake Google Play Store clones to steal data, with the malware abusing Accessibility Services for control.

A new ransomware strain called Cephalus is using compromised RDP, DLL sideloading, and abused security tools to bypass defenses and intimidate victims.

A new report from AhnLab reveals the Underground ransomware gang is back with a global campaign that uses sophisticated multi-layered encryption and customized malware.

A new report reveals that a phishing attack on a Salesforce vendor has led to a data breach at Farmers Insurance, exposing the data of over 1.1 million customers.

A new report reveals a rapidly growing global phishing campaign using fake voicemails and purchase orders to distribute UpCrypter, a sophisticated malware loader.
A new report reveals that Android droppers are evolving. They are now being re-engineered to bypass Google Play Protect and deliver a wide range of malware.

A new report reveals that potentially unwanted programs are evolving into malicious software that turns victims' computers into residential proxies for a profit.

Ex-Eaton programmer Davis Lu sentenced for planting a malicious “kill switch” that sabotaged company servers and caused massive financial losses.

Following a breach tied to an insider, Coinbase is restricting remote work and requiring U.S. citizenship for key roles to combat infiltration by North Korean hackers.

A new report reveals the Anatsa banking trojan is now targeting over 831 financial institutions worldwide. The malware is distributed via fake apps on Google Play.

A new report reveals the return of Gayfemboy, a Mirai-based IoT malware strain. It now uses advanced evasion techniques and targets multiple vendors to launch attacks.

A new RaaS operation called BQTLock is targeting victims with sophisticated malware, aggressive ransom demands, and a tiered subscription model for affiliates.
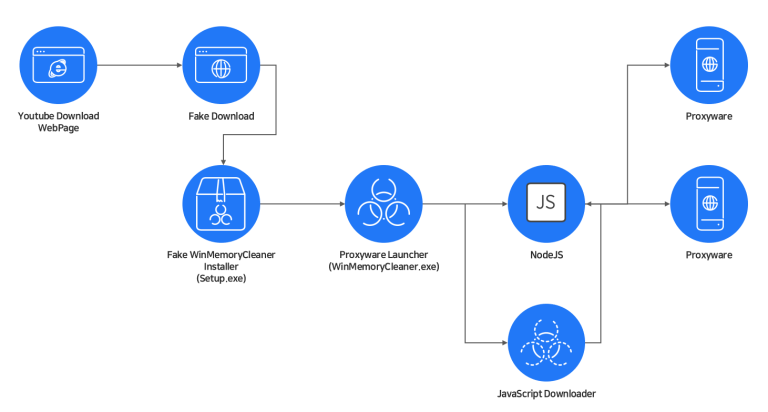
A new report reveals that malicious YouTube video downloader sites are tricking users into installing Proxyware, a type of malware that hijacks network bandwidth.

A dangerous Go package, disguised as a fast SSH brute-force tool, is secretly stealing login credentials and sending them to an attacker via a Telegram bot.

A new report reveals a stealthy attack on GeoServer using a critical RCE flaw. Instead of ransomware, attackers are hijacking servers to earn passive income.
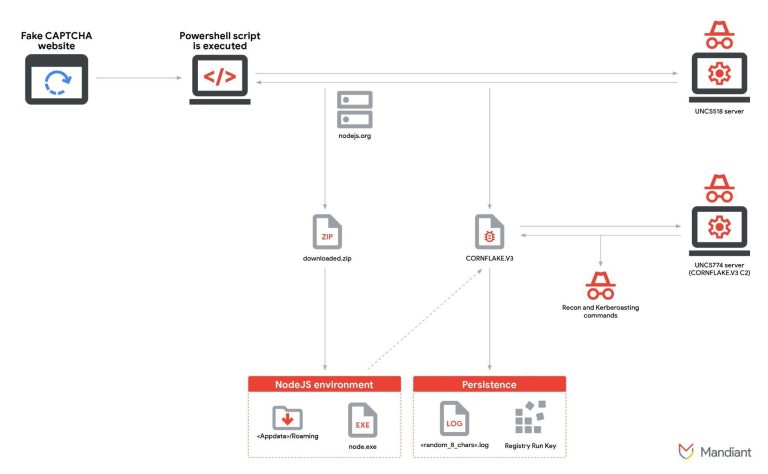
UNC5518 is using "ClickFix," a new technique that weaponizes fake CAPTCHAs to trick users into launching malware and providing access to other criminal groups.
A 22-year-old Oregon man has been charged with operating the RapperBot botnet, a network of 10,000s of devices that launched over 370,000 attacks.