 Do Son
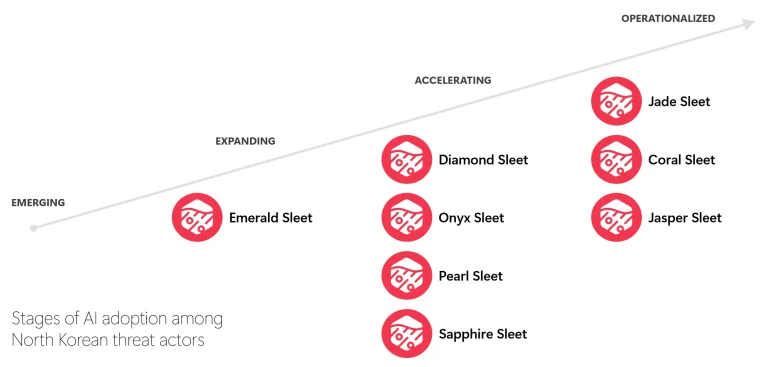
Microsoft reveals how North Korean threat actors use tools like ARTEX. See how AI-enabled North Korean threat actors speed up cyber operations.
Cybercrime
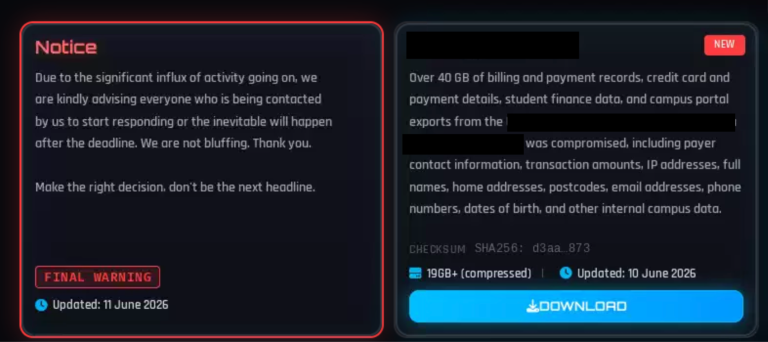
A ShinyHunters hacker arrest in Jordan may aid the FBI, as an alleged member reportedly shares devices and chats. Here is what we know.
Security researchers uncovered the new PAPERMILL cybercrime cluster. Learn how the PAPERMILL cybercrime cluster uses tax lures to deploy VenomRAT.
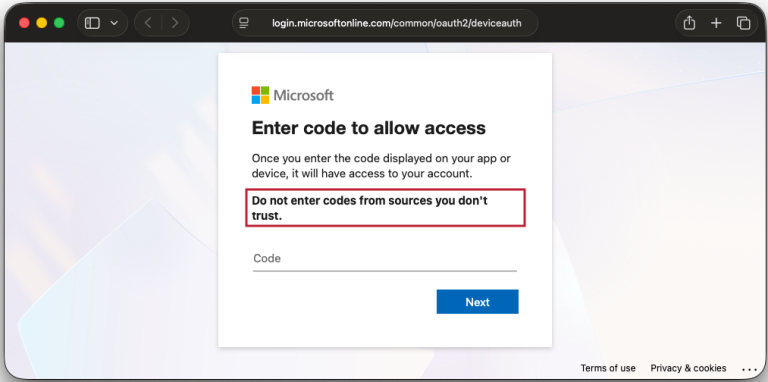
Security researchers uncovered a new GhostCode phishing kit. Learn how the GhostCode phishing kit bypasses MFA to hijack enterprise Microsoft 365 accounts.
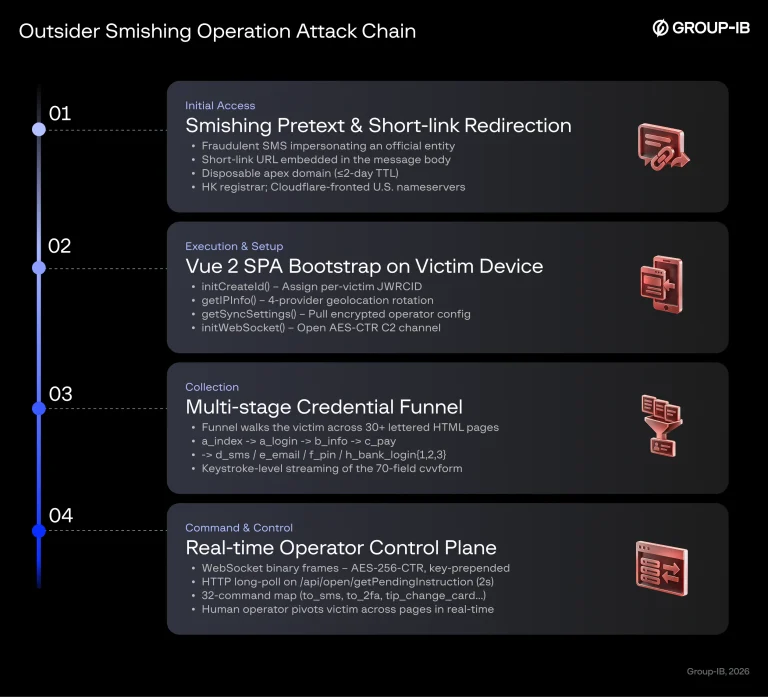
Group-IB exposed a new Smishing Triad phishing kit used by Outsider. Learn how this Smishing Triad phishing kit steals financial data worldwide.
Silent Push uncovered a North Korean IT worker scam recruiting proxies. Learn how a North Korean IT worker uses Discord to bypass corporate hiring filters.
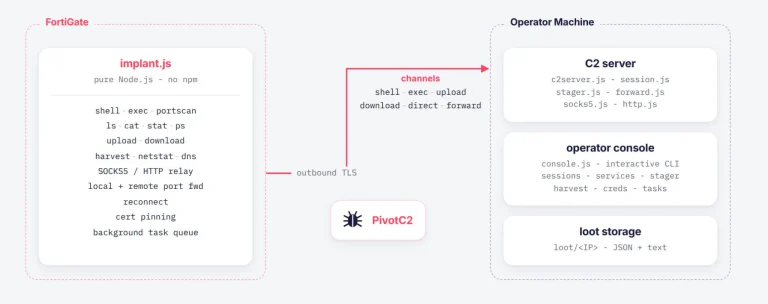
Discover how the PivotC2 FortiGate RAT uses CVE-2025-25249 exploitation to harvest credentials and tunnel traffic across corporate network environments.
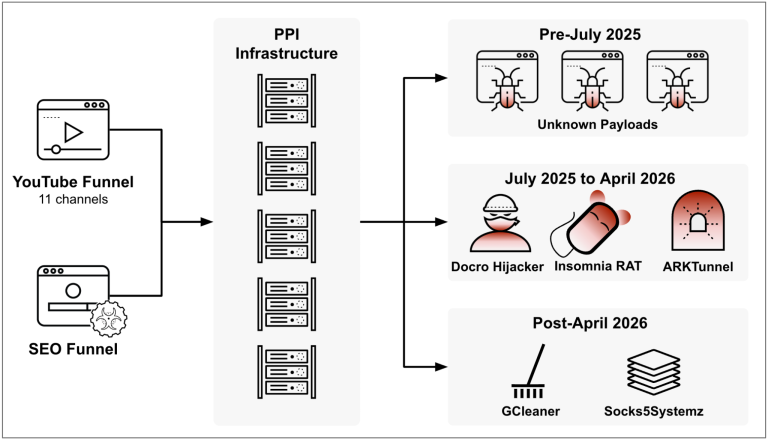
Unit 42 uncovered a large OfferLoader malware campaign distributing backdoors. Discover how OfferLoader malware abuses YouTube to compromise endpoints.
Defend against the CVE-2026-51990 Sogou exploit. Discover how hackers use this one-click flaw to drop backdoors and how to secure your systems today.

A Conti ransomware developer sentenced to prison for wire fraud conspiracy. Learn how this Conti ransomware developer faces justice.
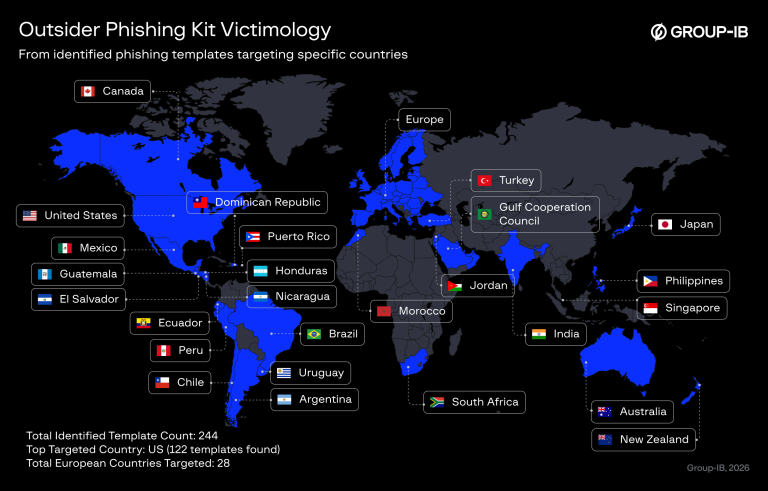
The Outsider Phishing Kit persists despite the Operation Ghost Hook takedown. Discover how the ChenLun Outsider PhaaS kit bypasses MFA via AiTM attacks.
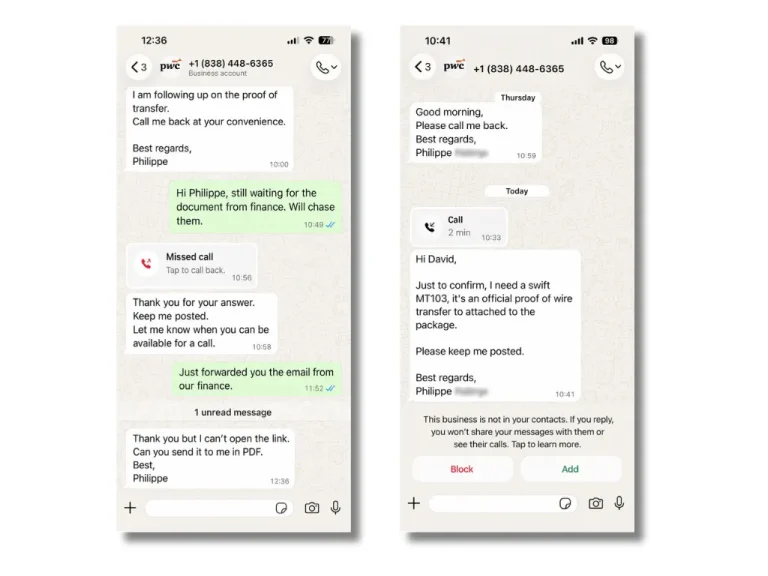
The Phantom Deal campaign uses fake acquisition documents to target executives. Gen exposed the Phantom Deal fraud after tracking bogus payment demands.
The Gambling Goblin campaign turns Brazilian government websites into an SEO weapon. Suspected Gambling Goblin operators push illicit gambling pages.
A Russian national indicted for malware faces trial. This Russian national indicted targeted 80,000 freelancers with malicious Excel attachments.
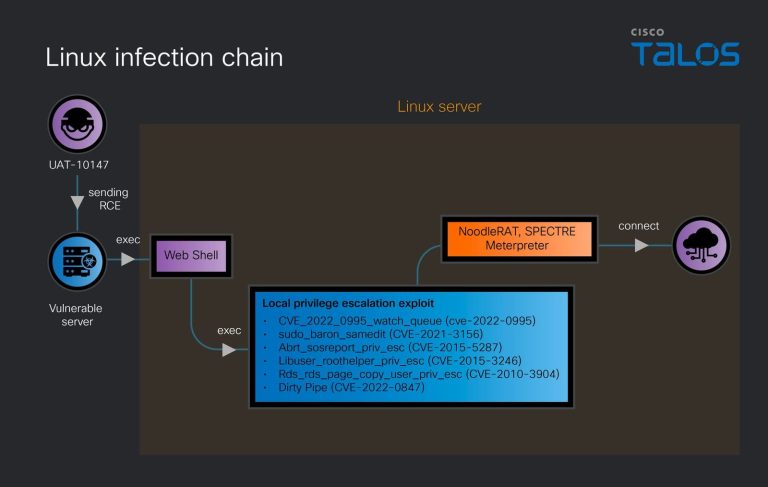
Cisco Talos revealed how UAT-10147 agentic AI attacks target global servers. Learn how UAT-10147 agentic AI tools automate intrusions and data theft.

A Canadian man pleaded guilty to a cloud hacking extortion scheme that hit 165 companies and stole billions of records. DOJ confirms the plea.

DOJ charged a Chinese national with wire fraud conspiracy in a gift card fraud scheme that shipped electronics from a New Hampshire warehouse to China.

A new GST phishing campaign targets Indian taxpayers. This operation delivers Remcos RAT malware using an embedded bitmap payload to steal user credentials.

Discover how the Mycelium Framework transforms infected machines into a malicious AI-as-a-Service botnet for distributed computing and automated exploits.
Following a Scattered Spider arrest, Peter Stokes faces extradition to the US for his alleged role in a $100M cyber extortion and hacking scheme.

A massive cloud DNS takeover campaign exploits abandoned enterprise domains to serve Thai gambling content. 163 organizations are currently compromised.

A massive Conti ransomware guilty plea reveals how these devastating ransomware attacks extorted $150 million from thousands of global victims.