
 Do Son
Read this Proofpoint cybercrime analysis on the surge of TA4922 malware campaigns targeting organizations globally with advanced evasion tactics.
Cybercrime

A Romanian hacker sentenced to prison following an identity theft conviction and selling access to a US government network infrastructure.

Europol completely dismantles 'First VPN,' seizing 33 servers and uncovering an underground database used by thousands of global ransomware operators.
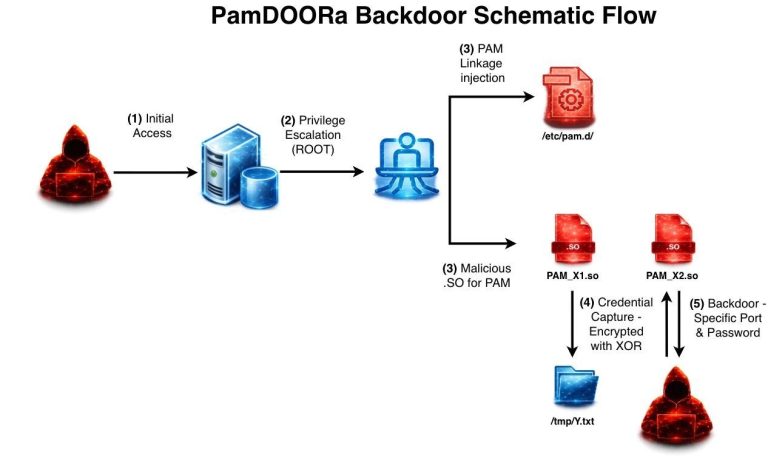
Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.
Job seekers beware: The JobStealer trojan poses as video meeting apps to hijack 300+ crypto wallets and Telegram data. Learn how to spot this 2026 threat.

Google AppSheet is being abused by "AccountDumpling" to steal 30,000 Facebook accounts. Learn how this Vietnamese-linked group bypasses SPF/DKIM filters.
Two US cybersecurity professionals get 4 years in prison for acting as ALPHV BlackCat ransomware affiliates, extorting victims and leaking patient data.

The alleged mastermind behind the massive "Versus Project" dark web market has been extradited to the US. He faces life in prison for cybercrime and drugs.
FBI, Dubai, and China dismantle 9 "pig-butchering" centers and arrest 276. Operation Level Up saves victims $562M in massive crypto fraud crackdown.

Former ransomware negotiator Angelo Martino pleaded guilty to working with BlackCat to extort his own clients. $10M in luxury assets seized. Facing 20 years.

Tyler Buchanan pleads guilty in US court for an $8M cyber heist. Discover how SMS phishing and SIM swapping bypassed 2FA to drain corporate & crypto assets.
RedLine architect Hambardzum Minasyan is extradited to the U.S. to face 50 years in prison for his role in the global malware empire and Operation Magnus.

The US DOJ, alongside Canada and Germany, has dismantled four massive IoT botnets responsible for record-breaking 30 Tbps DDoS attacks worldwide.
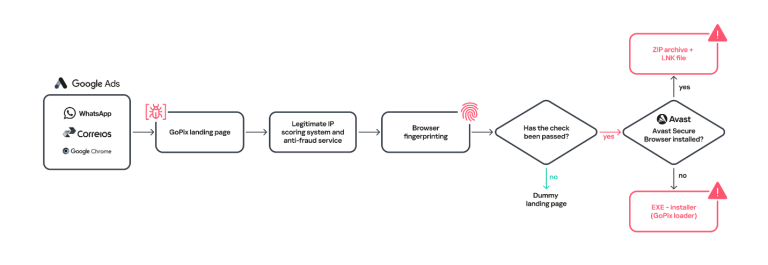
Kaspersky Labs details GoPix, a highly advanced Brazilian banking Trojan using memory-only implants and MitM attacks to target Pix and crypto.
Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground

Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground
Check Point Research reveals Iranian state hackers (Void Manticore) are weaponizing RaaS and criminal malware like Rhadamanthys for plausible deniability.

Following the Lumma takedown, the sophisticated AuraStealer malware is rapidly gaining ground, using TikTok scams and stealth to harvest data.

Cyfirma reveals how Telegram has replaced the dark web as the ultimate digital black market, making tools like malware and data theft available to anyone.

Varonis uncovers 1Campaign, a sophisticated tool by 'DuppyMeister' that helps hackers bypass Google Ads security to deliver phishing and crypto drainers.
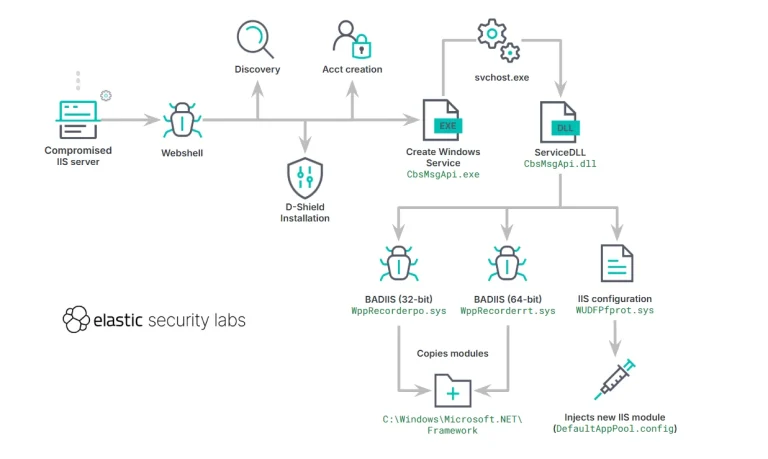
Elastic Security Labs uncovers BADIIS malware compromising 1,800+ IIS servers. Attackers use SEO poisoning to redirect users to illicit gambling sites.
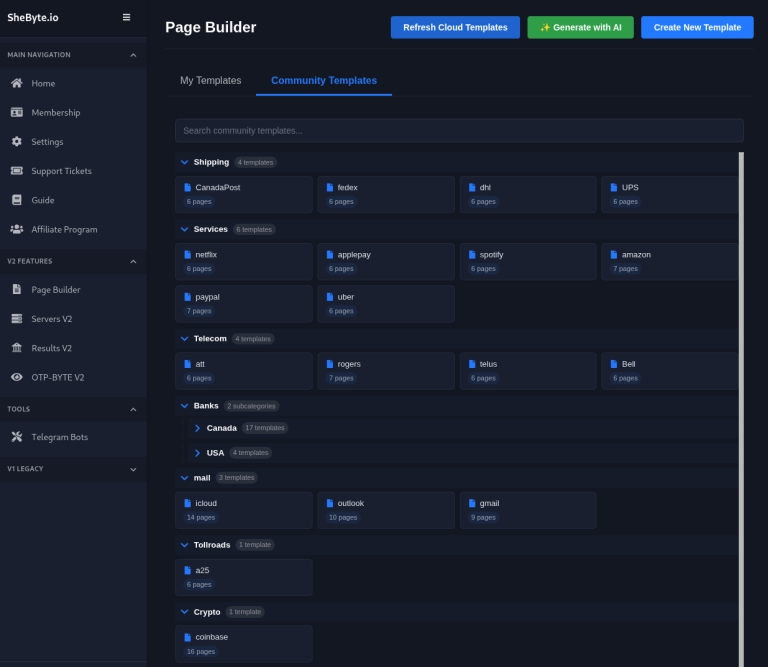
Rapid7 reveals how "Carding-as-a-Service" mimics legitimate e-commerce. Fraud markets now offer refunds & "Fullz" data. Learn about the new threat.

LockBit 5.0 launches with a unified codebase targeting Windows, Linux, and ESXi. Acronis reveals identical encryption and ties to SmokeLoader.
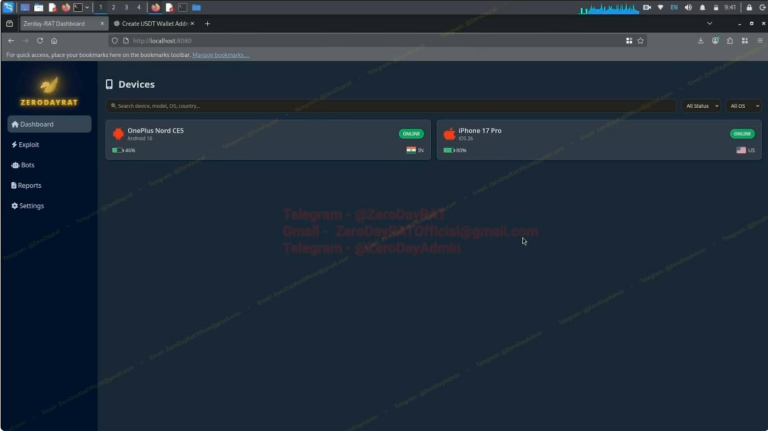
ZeroDayRAT mobile spyware is sold on Telegram. It offers full remote control of Android & iOS devices, including camera streaming & crypto theft.