
 Do Son
LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.
Cybercrime
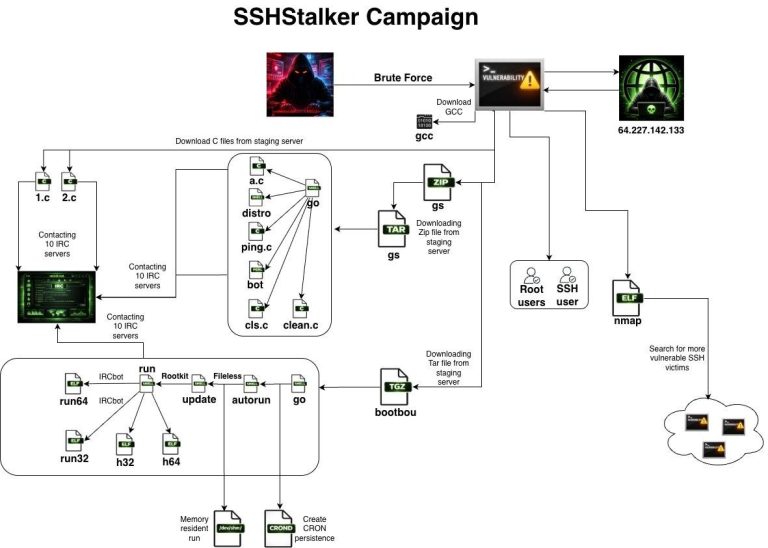
New SSHStalker botnet uses vintage IRC tactics & automated SSH brute-forcing to compromise Linux servers. Flare research reveals a "zombie army" in the making.

Zscaler reveals Marco Stealer, a new malware harvesting crypto & cloud files. It uses AES-256 encryption & kills analysis tools. Learn how to detect it.

Rublevka Team's "scam-as-a-service" has stolen $10M+ in crypto. Their automated Solana drainers target Phantom & Solflare wallets. Don't be next.
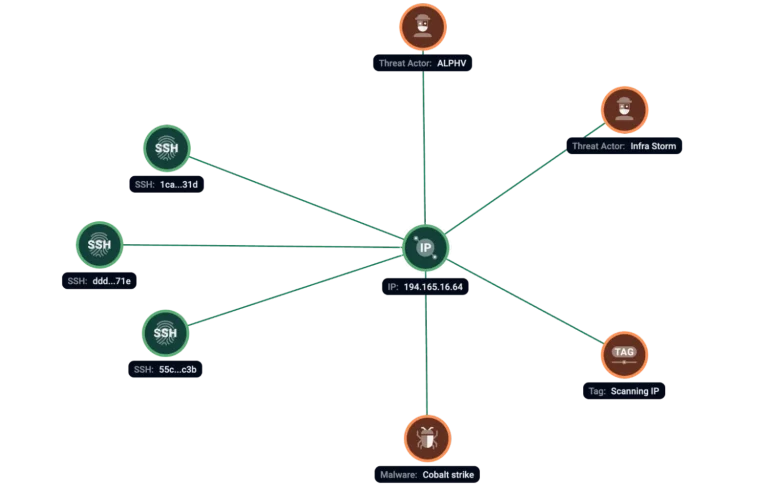
Group-IB reveals ShadowSyndicate is evolving. The cybercrime cluster now rotates SSH keys to hide its infrastructure. Is it a BPH or IAB?

In a troubling convergence of trusted developer infrastructure and cybercrime, Bitdefender researchers have uncovered a sophisticated Android...

New AI-generated malware campaign targets job seekers. Vietnamese actor "Huna" uses fake job offers to deliver PureRAT via Dropbox.
Jingliang Su sentenced to 46 months for laundering $36.9M in "pig butchering" proceeds. The scheme funneled crypto to Cambodian fraud hubs.

New "PayTool" fraud cluster targets Canadians via fake Gov & Air Canada sites. CloudSEK reveals how this PhaaS operation steals Interac logins.

LockBit 5.0 emerges with new "premium" criminal services. AhnLab analysis reveals how the top RaaS gang targets IT firms and churches alike.

New "Ghost Tap" malware lets hackers relay NFC signals from your Android phone to steal funds remotely. Learn how this sophisticated Group-IB discovery works.

Unit 42 unmasks VVS Stealer, a Python-based threat using Pyarmor obfuscation to bypass AV, hijack Discord sessions, and steal browser credentials.

Two US cybersecurity pros, Ryan Goldberg and Kevin Martin, plead guilty to moonlighting as ALPHV/BlackCat affiliates, extorting $1.2M from victims.

Intrinsec’s 2025 report unmasks "Fly," the elusive operator of Russian Market, linking the decade-old bazaar to early malware and BTC-E laundering.

Group-IB uncovers "Wonderland," a bidirectional Android SMS stealer in Uzbekistan that uses Telegram droppers to drain bank accounts and hijack sessions.
Nefilim's Artem Stryzhak pleads guilty to targeting $100M+ firms. As he faces 10 years, the DOJ offers an $11 million reward for leader Volodymyr Tymoshchuk.

The Gentlemen ransomware group rapidly emerged, targeting 17 countries with double extortion. It uses BYOVD and GPO manipulation to bypass security and hit manufacturing, healthcare, and insurance sectors.

Following a data leak, emails from the French Ministry of the Interior's domain invited hackers to the 'new' BreachForums. The community warns it is likely a highly sophisticated honeypot.

A military-grade backdoor, ValleyRAT, saw an 85% surge after its builder was leaked. The kernel-mode rootkit bypasses Windows 11 defenses and is now a dangerous commodity for cybercriminals.

A movie torrent scam uses a DiCaprio film lure to infect PCs with Agent Tesla RAT. The attack chain uses LNK files and malicious code hidden in a subtitle file to achieve fileless execution via LotL tools.

Makop ransomware operators now use GuLoader and BYOVD (ThrottleStop.sys) to bypass EDR and security. The "low-effort" campaign targets RDP-exposed networks, with 55% of attacks aimed at India.

Despite takedown, LockBit 5.0 resurges as a cross-platform threat. The new variant blinds Windows Event Tracing (ETW), uses Invisible Mode for stealth encryption, and overwrites free disk space.