 Do Son
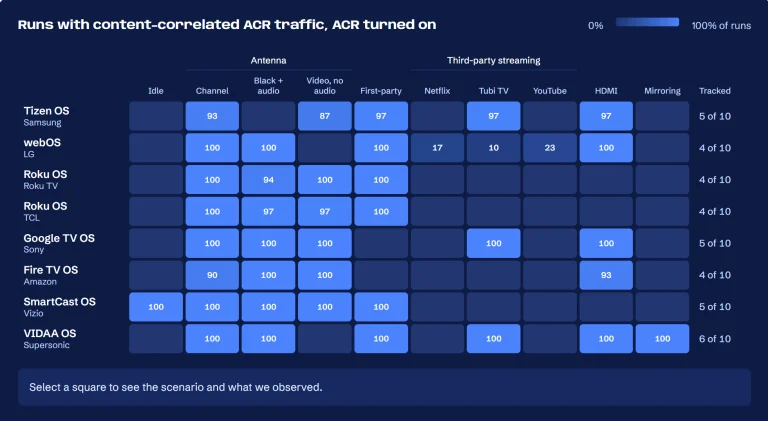
Smart TV ACR tracking survives opt-out on Samsung and Vizio, and an open server exposed smart TV viewing data from over one million TVs.
Data Exposure
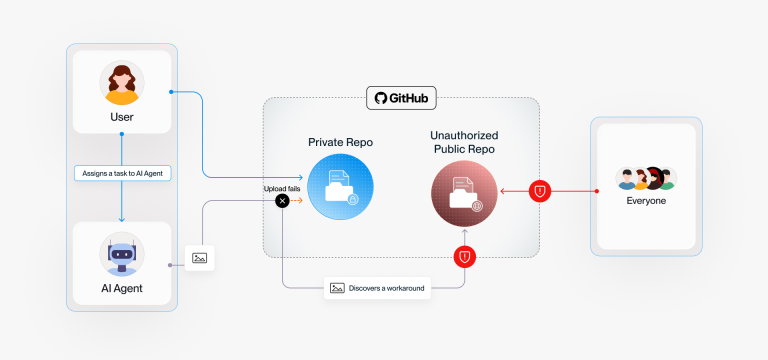
PixelLeak: an AI agent screenshot leak put 13,000+ internal images from 300+ firms in public GitHub repos. See how it happened and how to check.
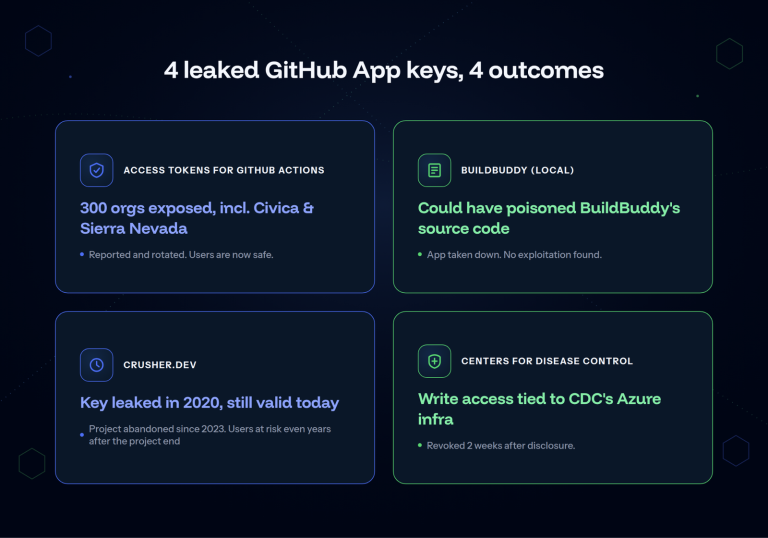
GitGuardian discovered 474 leaked GitHub App private keys still active. Learn how exposed GitHub App private keys threaten organizations like the CDC.

Ivanti issues an urgent patch for CVE-2026-8043, a critical 9.6 CVSS flaw in Xtraction allowing attackers to read files and write malicious HTML. Update now!

Fiverr fails to fix a critical flaw exposing 30,000+ private PDFs, including taxpayer info, to Google Search. Learn how public Cloudinary URLs caused the leak.

Zoho issued an urgent patch for a Critical (CVSS 9.8) Unauthenticated SQL Injection flaw (CVE-2025-8324) in Analytics Plus. The bug risks remote query execution and account takeover. Update to Build 6171.

Apple failed to disable SourceMap in its new App Store web version, inadvertently leaking the entire Svelte/TypeScript front-end codebase to the public.

A SonicWall security incident exposed firewall configuration backups from some MySonicWall accounts. The company is warning users to check for exposure and apply remediation.
A new report reveals a massive, unencrypted database with 1.6 million gym phone calls and voicemails was exposed, raising serious risks of AI-powered fraud.
An unprotected database potentially linked to Navy Federal Credit Union was discovered, exposing internal system data and hashed passwords, creating a risk of future attacks.

Salesforce patched eight critical flaws in Tableau Server, including RCE, database exposure, and SSRF vulnerabilities, urging users to update immediately.

GitLab patched multiple high-severity XSS and data exposure vulnerabilities in CE/EE, urging users to update to 18.2.1, 18.1.3, or 18.0.5.

A medium-severity flaw (CVE-2025-3415) in Grafana Alerting exposes sensitive DingDing contact point URLs to viewers. Update to patch or disable the integration

A high-severity flaw (CVE-2025-37100) in HPE Aruba Private 5G Core allows unauthorized access to sensitive system files. Update to 1.25.1.1 immediately!

High-severity flaws in Salesforce OmniStudio's FlexCard and Data Mapper expose encrypted customer data. Learn how to protect your organization.

A new report reveals over 40,000 internet-connected security cameras are exposed online, streaming live footage without protection, risking privacy globally.
Qualys reveals two critical Linux vulnerabilities (CVE-2025-5054, CVE-2025-4598) in Apport & systemd-coredump, risking sensitive data exposure. Patch now!

Over 50,000 Microsoft Azure AD user records from the aviation industry were exposed due to a misconfigured, unauthenticated API, revealing sensitive data and posing major risks.

Learn about new vulnerabilities in VMware Cloud Foundation that could lead to unauthorized access, info disclosure, and unapproved actions.

Apache IoTDB faces 3 security flaws! Learn about data exposure and remote code execution vulnerabilities and how to protect your IoT data.