
 Do Son
ShinyHunters PeopleSoft attacks are back. A one-letter WAF bypass lets the group exploit CVE-2026-35273 and plant web shells on unpatched servers.
data extortion
Discover how the PREY-0058 extortion campaign uses Microsoft 365 vishing attacks and AiTM tactics to bypass MFA, steal cloud data, and demand high ransoms.

A Canadian man pleaded guilty to a cloud hacking extortion scheme that hit 165 companies and stole billions of records. DOJ confirms the plea.
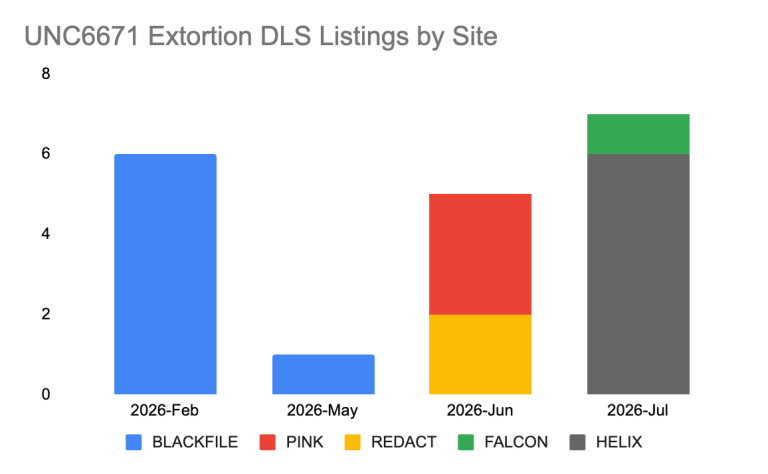
ReliaQuest links the new Helix data extortion group to BlackFile, using vishing and device code phishing to steal SharePoint data.
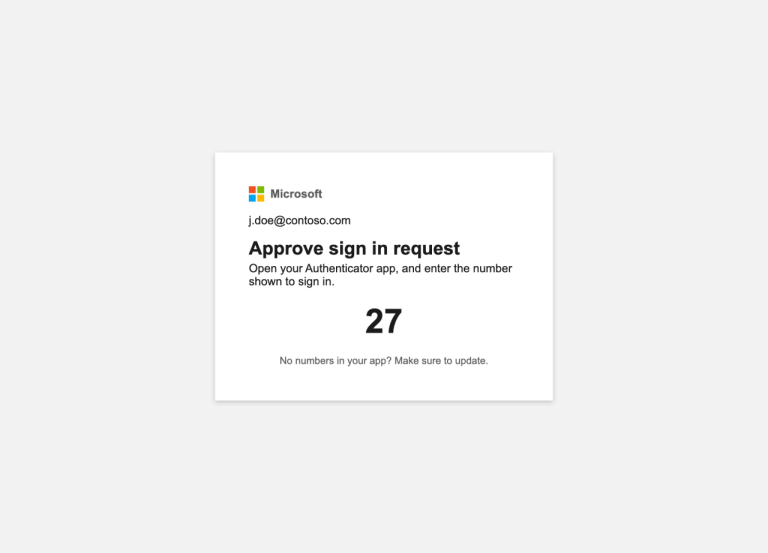
A vishing attack tricks Microsoft 365 users into passkey phishing, letting O-UNC-066 enroll its own passkey and hijack Entra accounts for extortion.
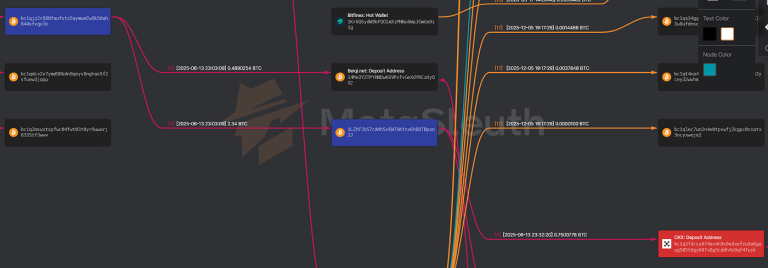
A case study on Kairos ransomware data extortion highlights the futility of paying a $1 million ransom without data encryption.

Yarix exposes the new Qilin-LockBit-DragonForce cartel. Is it a powerful merger or a desperate PR stunt for a "dead" LockBit? Find out.

A consortium of LAPSUS$/ShinyHunters hackers launched an EaaS campaign, claiming 1 billion records stolen from 39 Salesforce customers, and demanded a ransom before an October 10 deadline.

The "Trinity of Chaos" alliance (Lapsus$, Scattered Spider, ShinyHunters) launched a DLS, listing 39 firms, including Google and Cisco, and claiming 1.5 billion stolen records.

Sekoia TDR reveals Interlock ransomware's evolving tactics, including ClickFix social engineering, to evade detection and steal data.