Skip to content
September 14, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Debian 13

Debian 13

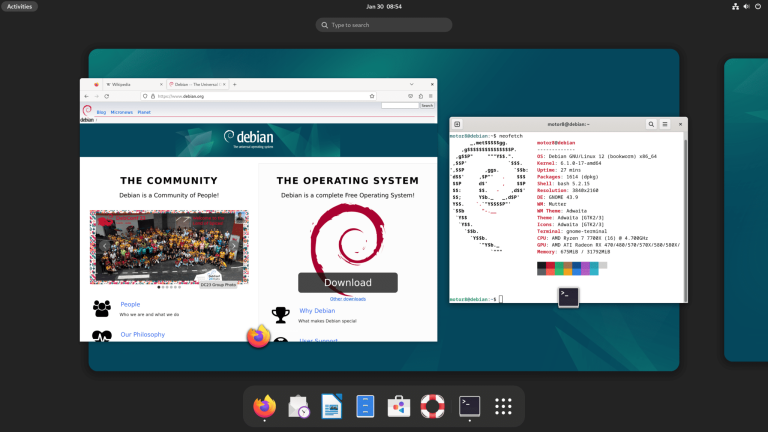
Debian 13.7 Released With 107 Security Updates Debian 13.7 point release desktop with security updates and Linux Kernel 6.12 LTS
  • Linux

Debian 13.7 Released With 107 Security Updates

Do Son September 14, 2026 0
The Debian Linux project recently released version 13.7, the seventh security-maintenance update in the Debian 13.x series....
Read More Read more about Debian 13.7 Released With 107 Security Updates
CERN to Move 2,200 Accelerator Control Machines to Debian 13 CERN Debian migration of accelerator control computers from Red Hat to Debian 13
  • Linux

CERN to Move 2,200 Accelerator Control Machines to Debian 13

Do Son September 4, 2026 0
The European Organization for Nuclear Research, which operates the Large Hadron Collider, recently announced that it will...
Read More Read more about CERN to Move 2,200 Accelerator Control Machines to Debian 13
Debian 13 Kernel Update Fixes 68 Flaws, Four Rated Critical Debian 13 Linux kernel security update DSA-6405-1 fixing 68 vulnerabilities including four critical use-after-free flaws in net/sched, NVMe/TCP, and SMC-R
  • Linux

Debian 13 Kernel Update Fixes 68 Flaws, Four Rated Critical

Do Son August 3, 2026 0
The Debian project has published security advisory DSA-6405-1, delivering a new Linux kernel update for Debian 13....
Read More Read more about Debian 13 Kernel Update Fixes 68 Flaws, Four Rated Critical
Debian 13 “Trixie” Nears Release with Official RISC-V Architecture Support Year 2038 Problem, Debian Linux Debian 11.2 Debian 13, RISC-V Support
  • Linux

Debian 13 “Trixie” Nears Release with Official RISC-V Architecture Support

Do Son July 21, 2025 0
The renowned open-source operating system Debian is currently undergoing final testing for its forthcoming release, Debian 13...
Read More Read more about Debian 13 “Trixie” Nears Release with Official RISC-V Architecture Support

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-51990
    A critical remote code execution vulnerability in Sogou Input Method, one of the most widely used Chinese-language input...
    Admin intel📅 Updated: Sep 12, 2026
  • CVE-2026-85706CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, an unauthenticated user could have read arbitrary files from...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42016CVSS 8.1
    JFrog Artifactory (Self Hosted) versions before 7.133.11 are vulnerable to a privilege escalation attack due to a validation...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42018CVSS 7.5
    JFrog Artifactory could return an internal anonymous-user token to an unauthenticated caller when anonymous access is disabled, potentially...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-84869CVSS 9.9
    A condition in the ScreenConnect client may allow files to be transferred and executed through an active remote...
    CISA KEV📅 Added to KEV: Sep 11, 2026
  • CVE-2026-20079CVSS 10.0
    A vulnerability in the web interface of Cisco Secure Firewall Management Center (FMC) Software could allow an unauthenticated,...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
  • CVE-2025-25249CVSS 8.1
    A heap-based buffer overflow vulnerability in Fortinet FortiOS 7.6.0 through 7.6.3, FortiOS 7.4.0 through 7.4.8, FortiOS 7.2.0 through...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
  • CVE-2026-87491
    Out of bounds write in V8 in Google Chrome prior to 153.0.8010.36 allowed a remote attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
Powered by CVE Watchtower

🔴 Live Critical Threats

  • CVE-2026-90703CVSS 9.1
    A vulnerability has been found in D-Link DWR-M921 1.1.52. The affected element...
  • CVE-2026-90702CVSS 9.1
    A flaw has been found in D-Link DWR-M921 1.1.52. Impacted is the...
  • CVE-2026-90699CVSS 9.9
    A weakness has been identified in D-Link DWR-M920 1.1.7. This issue affects...
  • CVE-2026-90693CVSS 9.9
    A flaw has been found in D-Link DIR-878 120B05. This impacts the...
  • CVE-2026-90692CVSS 9.9
    A vulnerability was detected in D-Link DIR-878 120B05. This affects the function...
  • CVE-2026-82787CVSS 9.8
    Missing authentication for critical function vulnerability exists in CPSL-08P1EN. If this vulnerability...
  • CVE-2026-90680CVSS 9.9
    A security flaw has been discovered in D-Link DIR-823G 1.0.2B05_20181207. The impacted...
  • CVE-2026-90608CVSS 9.9
    A flaw has been found in Totolink A3002MU Hh-B20211125.1046. The affected element...
  • CVE-2026-90607CVSS 9.9
    A vulnerability was detected in Totolink A3002MU Hh-B20211125.1046. Impacted is the function...
  • CVE-2026-90606CVSS 9.9
    A security vulnerability has been detected in Totolink A3002MU Hh-B20211125.1046. This issue...
Powered by CVE WATCHTOWER

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.