 Do Son
Apache Roller vulnerability CVE-2026-129448 (CVSS 9.8) allows unauthenticated RCE and is actively exploited. Upgrade to 6.1.6 or later now.
Deserialization
Gradle 9.9.1 and 8.14.7 fix three Gradle vulnerabilities, including a CVSS 9.3 version catalog code injection that runs during builds and IDE sync.
18 Apache Airflow vulnerabilities, including Celery code execution CVE-2026-68982, are fixed in Airflow 3.4.0, plus two Apache Storm flaws.
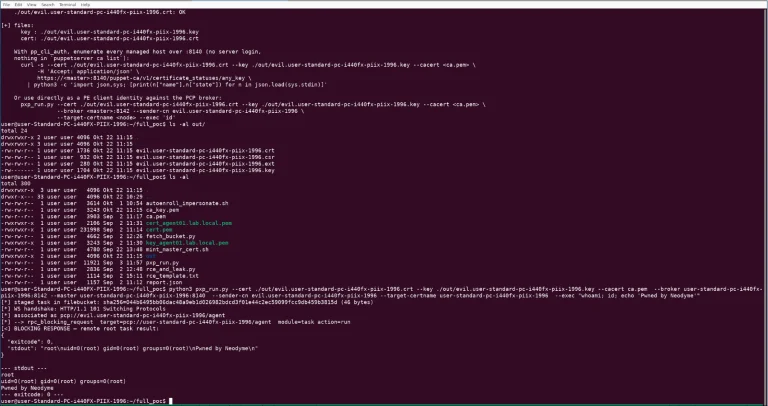
Puppet Server RCE CVE-2026-115731 (CVSS 9.4) now has a public proof-of-concept exploit. Update OpenVox and Puppet Enterprise to patched versions.
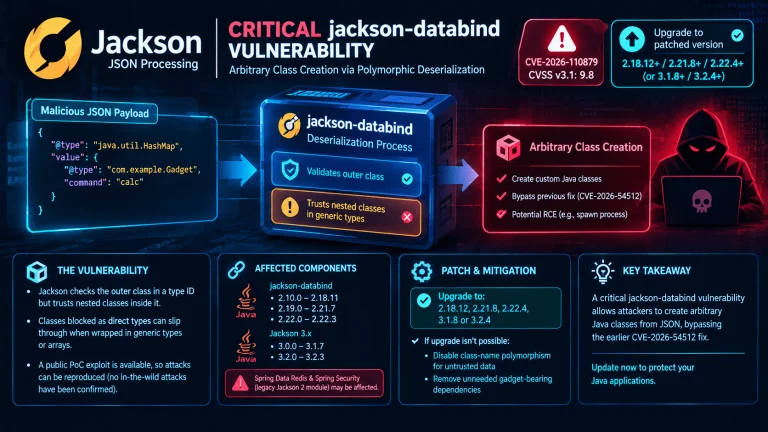
Details and a PoC exploit are public for jackson-databind vulnerability CVE-2026-110879 (CVSS 9.8), a bypass of the CVE-2026-54512 fix. Patch now.
Jenkins fixed a deserialization flaw leading to remote code execution, plus over 30 more CVEs across core and popular plugins. Update now.
An unpatched Log4j RCE vulnerability was publicly disclosed on Apache's issue tracker. No CVE is assigned and no fix exists yet. Workaround inside.
CVE-2026-69836 is a CVSS 10 Entra ID remote code execution flaw exploited in the wild. Microsoft has fully mitigated it server-side.

Splunk patches CVE-2026-76404, a critical remote code execution flaw in the MCP Server app, plus 16 more bugs across its apps and add-ons.

Critical Jenkins vulnerability CVE-2026-70426 lets attackers bypass the JEP-200 filter and run code on the controller. Patch now.
Four OpenAM vulnerabilities are fixed in 16.1.2. CVE-2026-62379 (CVSS 9.8) allows unauthenticated remote code execution; CVE-2026-62261 scores 9.9.

Four OpenDJ vulnerabilities are patched in 5.1.2. They include a CVSS 9.6 authorization bypass and an unauthenticated SSRF scoring CVSS 9.4.

Apache Fory vulnerabilities hit Java, C++, and Rust deserialization, including CVE-2026-64606. Upgrade to Fory 1.4.0 to fix all four flaws.
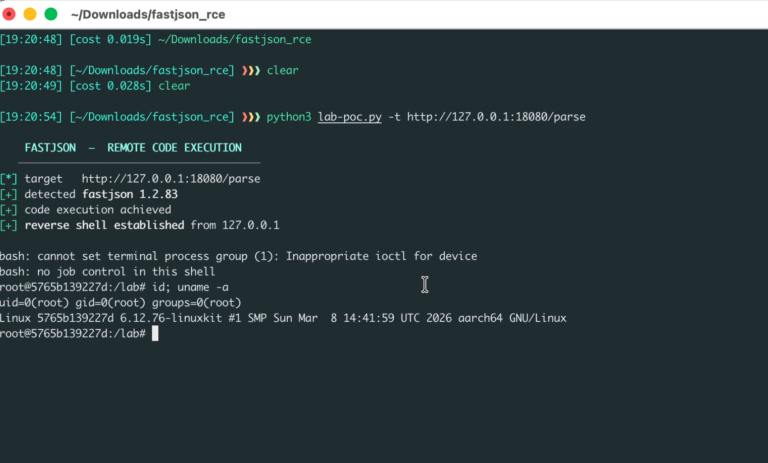
FastJson RCE vulnerability CVE-2026-16723 is exploited in the wild. Details and PoC exploit code are public for this critical remote code execution flaw.
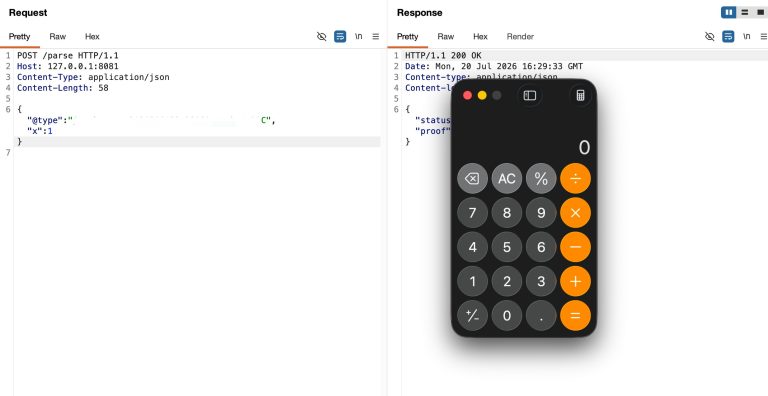
A fastjson RCE hits versions 1.2.68 to 1.2.83 under stock defaults. Details and public PoC code are out, so enable SafeMode or move to fastjson2.
CVE-2026-50522, a critical SharePoint RCE flaw, is exploited in the wild. A public PoC exploit is out, so admins should patch SharePoint now.
Metabase patched CVE-2026-59827 (CVSS 9.9) and CVE-2026-59826 (CVSS 9.1). These flaws enable remote code execution via unsafe H2 deserialization.

A SharePoint remote code execution flaw (CVE-2026-33112) is now public with full details and PoC. A low-privilege user can run code. Patch now.

CISA flags an actively exploited SharePoint vulnerability (CVE-2026-45659) enabling remote code execution. Patch SharePoint Server 2016 now.

A critical iba deserialization vulnerability (CVE-2026-8024) lets unauthenticated attackers gain remote code execution on ibaPDA and ibaDatCoordinator.
Three NVIDIA NeMo vulnerabilities (CVE-2026-24155, CVE-2026-24252, CVE-2026-24228) enable code execution. Update NeMo Framework to v2.7.3 now.

A Jenkins RCE vulnerability (CVE-2026-53435) is under active exploitation. Honeypots are seeing attacks now, so patch your Jenkins controller fast.