 Do Son
OpenTelemetry patches a critical 9.3 RCE flaw (CVE-2026-33701) in its Java agent. Unfiltered RMI deserialization allows full system takeover. Update to 2.26.1.
Deserialization

Apache Camel patches critical flaws in Keycloak (CVE-2026-23552) and LevelDB (CVE-2026-25747) components that allow auth bypass and RCE. Update to 4.18.0.

Apache Karaf Decanter flaw CVE-2026-24656 allows unauthenticated attackers to crash the log collector via deserialization. Update to v2.12.0 immediately.

Apache NiFi patches a High-severity flaw (CVE-2025-66524) in the GetAsanaObject processor. Unfiltered deserialization risks system compromise. Update now!

NVIDIA issued a Critical (CVSS 9.0) patch for Isaac Lab and the NeMo Framework, fixing flaws that allow code execution and data tampering in AI models.

NVIDIA patched High-severity (CVSS 8.8) deserialization flaws in Merlin's NVTabular and Transformers4Rec on Linux. Exploitation risks RCE, DoS, and data tampering in AI recommendation pipelines.

A Critical RCE (CVSS 10.0) flaw, React2Shell, in React/Next.js's Flight protocol allows unauthenticated system takeover. North Korean and Chinese state actors are actively exploiting the deserialization bug.

Developers using the modern stack of Next.js and React are facing a “red alert” situation today. A...

SAP released its Patch Day update fixing 18 flaws, including two Critical (CVSS 10.0) vulnerabilities: RMI-P4 RCE and Hard-Coded Credentials in SQL Anywhere Monitor, risking unauthenticated takeover.

A Critical RCE flaw (CVE-2025-59287, CVSS 9.8) in WSUS allows unauthenticated attackers SYSTEM access via AuthorizationCookie deserialization. The issue was patched in the October update.

A Critical (CVSS 9.8) RCE flaw in Keras 3’s Torch backend (CVE-2025-49655) allows attackers to execute arbitrary code by loading a malicious model due to insecure deserialization.

Apache issued a critical fix for ActiveMQ NMS AMQP Client (CVE-2025-54539). The deserialization flaw allows untrusted AMQP servers to execute remote code on client systems.

A Critical (CVSS 10.0) zero-day RCE flaw (CVE-2025-10035) in GoAnywhere MFT is being actively exploited by the Medusa ransomware group, Storm-1175. Patch immediately.

Synacktiv exposed a critical flaw chain in Snipe-IT. A low-privileged user can exploit a Stored XSS (CVE-2025-59712) to hijack admin sessions and trigger RCE (CVE-2025-59713) via unsafe deserialization.

Apache Fory has a critical RCE vulnerability (CVE-2025-61622) in its pyfory module. An attacker can exploit an unguarded pickle fallback to execute arbitrary code.
CISA adds a critical deserialization flaw in Dassault Systèmes DELMIA Apriso (CVE-2025-5086) to its KEV catalog, with active exploitation confirmed.

Today, SAP released 21 new Security Notes and 4 updates as part of its monthly Security Patch...

A critical RCE flaw (CVE-2025-53772) in IIS Web Deploy allows an authenticated attacker to execute arbitrary code. A PoC is public, and patching is urgent.

A critical flaw (CVE-2025-6507) in the H2O-3 machine learning platform allows attackers to bypass security filters, leading to remote code execution.

Two critical flaws in the open-source BI tool DataEase allow attackers to achieve remote code execution and arbitrary file writes, exposing unpatched systems to compromise.

Axis warns of a critical flaw (CVE-2025-30023, CVSS 9.0) in Camera Station Pro/5 and Device Manager, allowing authenticated RCE via protocol deserialization. Update immediately.
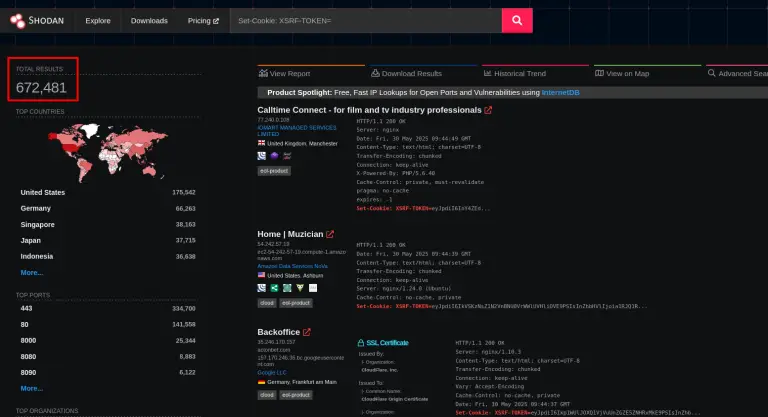
Synacktiv reveals Laravel’s APP_KEY vulnerability allows RCE via deserialization attacks when the key is leaked or guessable, risking full application compromise.