 Do Son
Jenkins fixes 15 vulnerabilities, including remote code execution flaws CVE-2026-117612 and CVE-2026-117614. Upgrade to 2.588 or LTS 2.580.2 now.
DevSecOps
An OVHcloud CLI attack swapped GitHub release files with a secret-stealing binary. Learn which versions are hit in this supply chain attack.
GitHub now expires npm trusted publishing setups that miss a first publish within 48 hours, closing a repo name reuse flaw in 1,500+ packages.
A GitLab critical vulnerability, CVE-2026-97229 (CVSS 10.0), allows unauthenticated arbitrary code execution. Upgrade to GitLab 19.4.2 now.
Four critical Argo CD vulnerabilities, including AppProject bypass CVE-2026-77459, threaten the repo-server and clusters. Upgrade to v3.5.4 now.
A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.
Progress DataDirect vulnerability CVE-2026-91140 enables command injection via crafted OpenAPI files in AI agents. Pull version 2.1 now.
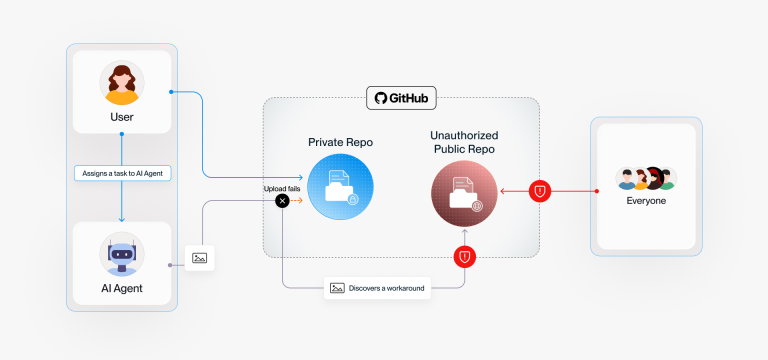
PixelLeak: an AI agent screenshot leak put 13,000+ internal images from 300+ firms in public GitHub repos. See how it happened and how to check.
A High-severity Octopus Server vulnerability, CVE-2026-101169, lets users with edit rights run code via insecure deserialization. Upgrade now.

The new GitLab patch release fixes 13 flaws, including high-severity XSS and authorization bugs. Update to 19.2.2, 19.1.4, or 19.0.6 now.

The latest GitLab patch release fixes 13 vulnerabilities, including CVE-2026-6267, a high-severity data exposure flaw. Update self-managed GitLab now.

Gitea vulnerability CVE-2026-58443 (CVSS 9.6) lets public-only tokens write to private repos. Details and PoC code are public. Update to v1.27.0.
The GitLab patch release fixes 8 flaws, including a high-severity cross-site scripting bug (CVE-2026-6896). Update to 19.1.2 now.

Multiple Fleet security vulnerabilities expose private environments to cross namespace secret disclosure and SSRF attacks. Patch your systems now.

Microsoft uncovers a massive npm dependency confusion attack targeting enterprise infrastructure. Learn how these malicious packages discovered run code.
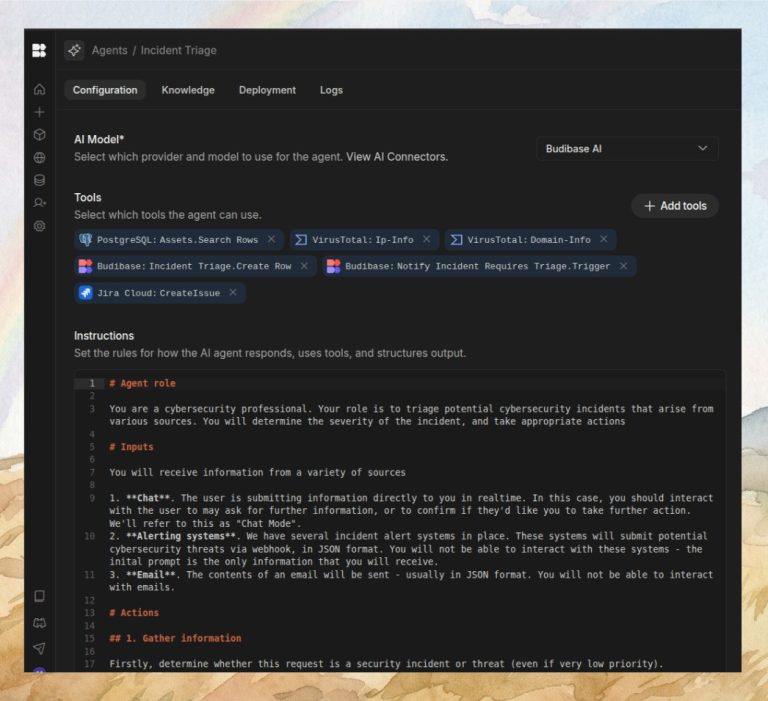
Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!
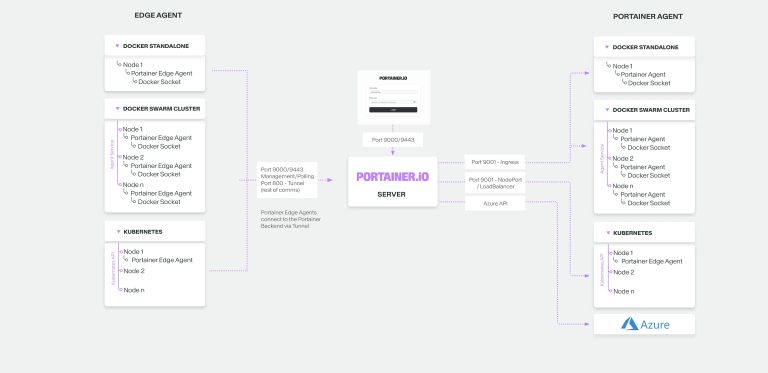
Portainer fixes two critical 9.4 CVSS flaws (CVE-2026-44848/49) allowing instant container escape to host root. Patch your environments now!

n8n fixes three critical 9.4 CVSS flaws (CVE-2026-44790/91/89). Authenticated users can break sandboxes for local file read and server-level RCE. Patch now!

Composer CVE-2026-45793 leaks GitHub tokens into CI/CD logs due to a validation error. Update to version 2.9.8 now and audit your GitHub Action logs.
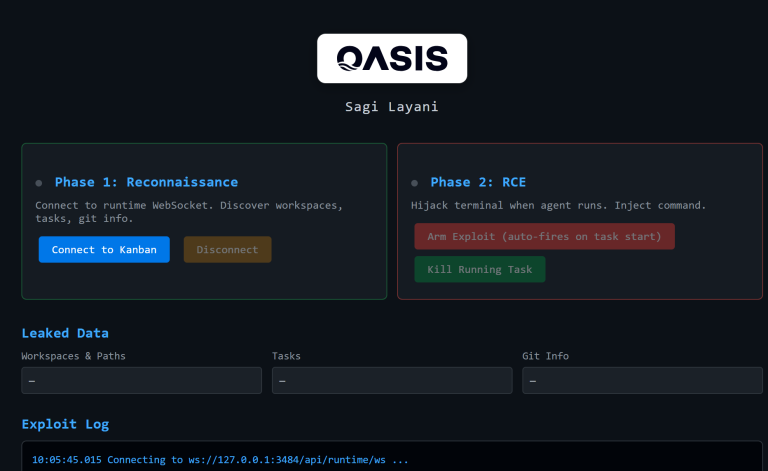
Critical Alert: CVE-2026-44211 (CVSS 9.6) in Cline AI allows malicious sites to hijack your terminal and steal data via WebSockets. Update your CLI tools now.
Protect your AI apps. Spring AI issues urgent patches for three critical vulnerabilities causing data destruction, memory poisoning, and user data leaks.

May 13 Deadline: Let’s Encrypt launches 45-day certs, freezes mTLS, and moves to Gen Y intermediates. Is your automation ready for the triple-threat update?