 Do Son
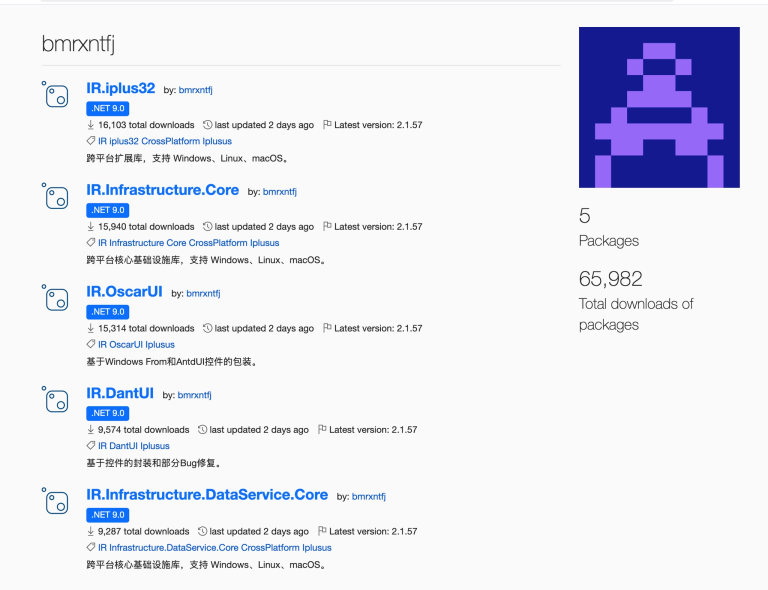
Critical alert: A stealth NuGet supply chain attack has hijacked 65,000 .NET workstations. Audit your CI/CD for malicious IR.* packages immediately.
DevSecOps

A malicious unscoped "tanstack" npm package used live-debugged postinstall scripts to steal .env secrets via Svix webhooks. Check your dependencies now.

Jenkins patches high-severity RCE in Credentials Binding and XSS in GitHub/HTML Publisher plugins. Secure your CI/CD pipeline by upgrading today.

AWS and OpenAI expand their alliance, bringing GPT models, Codex, and managed AI agents to Amazon Bedrock with enterprise-grade security and consolidated billing.

PHPUnit CVE-2026-41570 allows RCE via invisible newline injection in CI/CD pipelines. Secure your build servers—update to 12.5.22 or 13.1.6 today.

GitLab fixes high-severity GraphQL CSRF and Web IDE vulnerabilities in versions 18.11.1, 18.10.4, and 18.9.6. Protect your sessions and projects—patch now!

Two critical CVSS 10.0 RCE flaws in Spinnaker's Clouddriver and Echo services allow full JVM and shell access. Patch your multi-cloud pipelines immediately.
Sonatype Nexus Repository (CVE-2026-5189) faces a critical 9.2 CVSS flaw. A hardcoded database credential grants full host access. Patch to v3.71.0 now!
GoHarbor's Harbor faces a critical 9.4 CVSS flaw (CVE-2026-4404). Default admin passwords allow total registry compromise and image poisoning. Update now.
Jenkins patches critical flaws (CVE-2026-33001 & CVE-2026-33002) allowing remote code execution and full CI/CD pipeline compromise. Update to 2.555 now.

Atlassian warns of a high-severity RCE vulnerability (CVE-2026-21570) in Bamboo Data Center. Patch now to secure your CI/CD pipelines from malicious code.
A critical 9.4 CVSS tag poisoning attack (CVE-2026-31976) hit the xygeni-action GitHub Action, injecting a C2 backdoor into CI/CD pipelines. Update now.
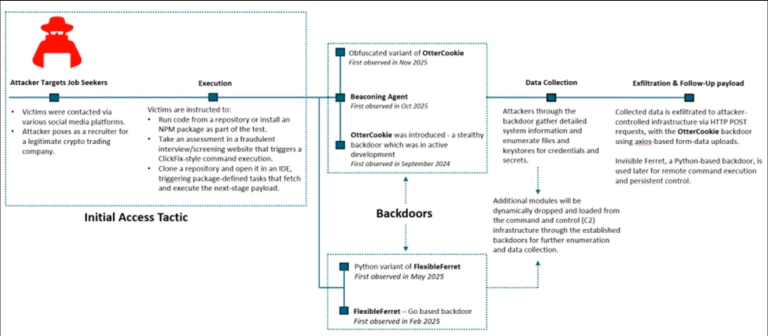
Microsoft exposes the "Contagious Interview" campaign. Fake recruiters trick developers into installing Invisible Ferret malware during coding tests.

GitLab issues urgent security updates (18.9.2, 18.8.6, 18.7.6) fixing critical XSS (CVE-2026-1090) and DoS flaws. Patch self-managed instances today.
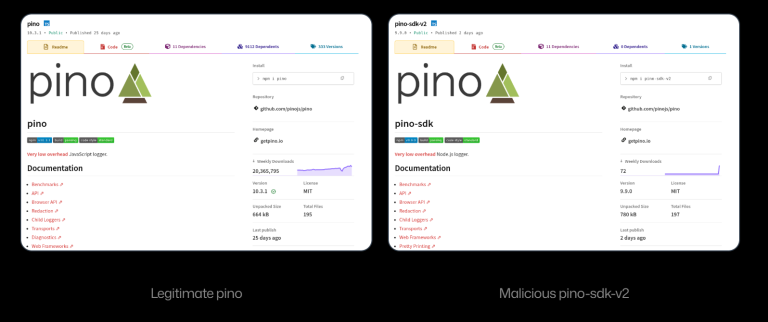
SafeDep uncovers pino-sdk-v2, a malicious npm package impersonating the pino logger to silently steal .env secrets and exfiltrate them via Discord.
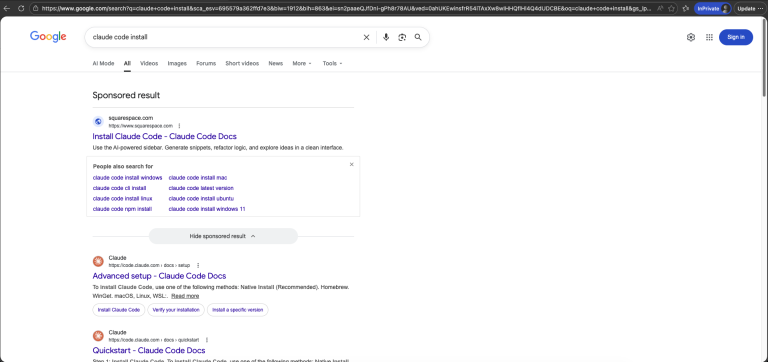
Hackers are targeting AI developers with a fake Claude Code "InstallFix" malvertising campaign, using malicious terminal commands to drop Amatera malware.
OpenAI launches Codex Security, an advanced AI agent that uses reasoning to find and fix complex vulnerabilities without the noise of false positives.

Socket reveals how an AI bot hijacked the Aqua Trivy VS Code extension, using prompt injection to turn developer AI assistants into stealthy data thieves.

OpenSSF warns of "hackerbot-claw," an autonomous AI bot exploiting GitHub Actions to hijack repositories. Secure your CI/CD pipeline before it’s too late.

Microsoft warns of critical flaw CVE-2026-25592 (CVSS 10.0) in Semantic Kernel SDK. AI agents can overwrite system files. Update to v1.70.0 now.

GitLab patches critical flaw CVE-2026-1868 (CVSS 9.9) in self-hosted AI Gateway. Vulnerability allows RCE via insecure templates. Update to v18.8.1 now.

VulnCheck reveals CVE-2025-11953 (Metro4Shell) was exploited in the wild since Dec 2025. Attackers target Windows & Linux dev servers. Patch now.