 Do Son
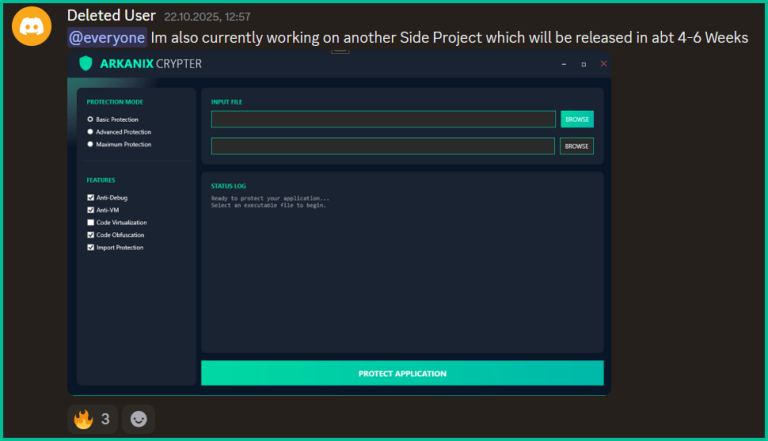
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
Discord C2

Zscaler detects NodeCordRAT, a new malware in malicious npm packages. It uses Discord as a C2 server to loot crypto wallets and Chrome data.
China-linked APT UNC5174 is using a Go-based backdoor that abuses the Discord API as a covert C2 channel. This method allows the lightweight malware to execute arbitrary commands and evade traditional firewall monitoring.