 Do Son
Nine Apache ActiveMQ vulnerabilities allow denial of service and a temporary destination takeover (CVE-2026-54475). Upgrade to 6.2.7 now.
dos

GitLab patches high-severity XSS (8.7 CVSS) and unauthenticated DoS flaws in versions 18.11.3, 18.10.6, and 18.9.7. Secure your DevOps pipeline now!

Protect your app from CVE-2026-23870. Learn how this high-severity React Server Components DoS flaw crashes servers and how to patch your React 19 build today.
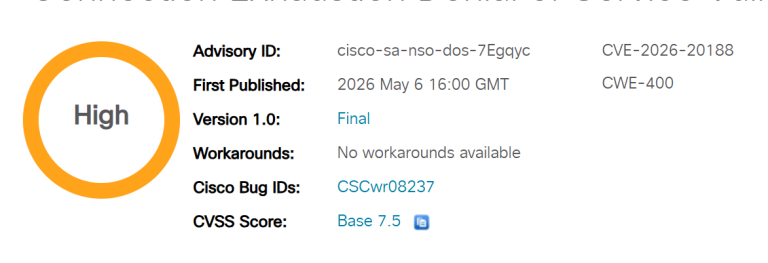
Cisco warns of a critical DoS flaw (CVE-2026-20188) in CNC and NSO. Unauthenticated attackers can freeze network management. Patch to CNC 7.2 or NSO 6.4.1.3 now!
React patches a 7.5 CVSS DoS vulnerability in Server Components (CVE-2026-23869). Stop CPU exhaustion attacks—update your 19.x dependencies now!

Grafana patches a critical 9.1 RCE (CVE-2026-27876) in SQL expressions that allows SSH hijacking. Update to 12.4.2 now to secure your monitoring host.

BIND 9 patches 3 flaws including a sneaky ACL bypass (CVE-2026-3591) and a High-severity CPU exhaustion bug. Secure your DNS infrastructure now.

strongSwan fixes a high-severity DoS flaw (CVE-2026-25075) in eap-ttls. Unauthenticated actors can crash VPN gateways. Patch now to stay protected!
MariaDB patches a high-severity buffer overflow (CVE-2026-32710) in its JSON validation function. Upgrade to 11.4.10 or 11.8.6 to prevent server crashes.

Django releases security updates (6.0.3, 5.2.12, 4.2.29) to fix a Windows DoS flaw (CVE-2026-25673) and file permission risks. Upgrade your framework now.

Node.js DoS flaw CVE-2026-26278 in fast-xml-parser freezes event loops via XML entity expansion. 46M weekly downloads affected. Update to version 5.3.6.

Critical PAN-OS flaw CVE-2026-0229 allows unauthenticated attackers to trigger reboot loops & maintenance mode via malicious packets. Patch immediately.
Django patches 3 critical SQL injection flaws & DoS risks in versions 6.0.2, 5.2.11, & 4.2.28. Update immediately to secure your database.

Critical Kyverno flaw CVE-2026-22039 (CVSS 10) allows policy creators to gain cluster admin rights. Update to v1.16.3 to fix privilege escalation & DoS.
New React Server Components flaw CVE-2026-23864 (CVSS 7.5) exposes apps to DoS attacks. Previous patches were incomplete. Update to v19.0.4+ now.

CVE-2026-0994 (CVSS 8.2) in Google Protobuf Python allows DoS via nested "Any" messages. Recursion limit bypass causes crashes. Update now.

Apache Karaf Decanter flaw CVE-2026-24656 allows unauthenticated attackers to crash the log collector via deserialization. Update to v2.12.0 immediately.

libheif flaw CVE-2025-65586 causes app crashes via malformed HEIF images. Update to v1.21.0 now to prevent Denial of Service attacks.
aiohttp 3.13.3 patches 7 flaws including memory exhaustion (CVE-2025-69228) and infinite loops (CVE-2025-69227). Update your Python servers now!

A critical Linux KVM flaw allows guests using Intel AMX to trigger host kernel panics. Fixes are underway for modern kernels (5.17+) to prevent host DoS.
New flaws found in React Server Components risk a Server-Crashing DoS (CVSS 7.5) via infinite loop and Source Code Disclosure (CVE-2025-55183). Update to v19.0.3/19.1.4/19.2.3 immediately.

An Important DoS flaw (CVE-2025-64775) in Apache Struts 2 risks server crashes. Improper cleanup of multipart request files leads to disk exhaustion. Update to v6.8.0 or v7.1.1 immediately.