 Do Son
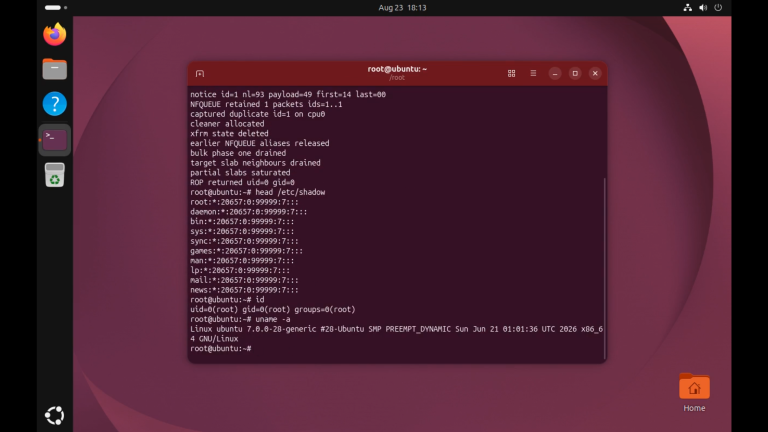
A public PoC exploit targets CVE-2026-72137, a CVSS 9.8 Linux kernel double-free that enables root privilege escalation. Patch now.
double-free
A public PoC now targets CVE-2026-66373, a Redis RCE double-free via RESTORE. See affected versions and upgrade to Redis 8.8.0 now.

Four libssh2 vulnerabilities let a malicious SSH server corrupt memory in connecting clients. Update past version 1.11.1 to stay protected.

A new strongSwan CVE-2026-47895 vulnerability allows remote code execution via a libstrongswan double-free exploit. Patch your VPN servers now!

Urgent: Public PoC for Apache CVE-2026-23918. A critical double-free in mod_http2 enables unauthenticated DoS and RCE. Update to Apache 2.4.67 immediately.

Apache releases v2.4.67 to fix an HTTP/2 Double Free RCE (CVE-2026-23918) and auth bypasses. Millions of servers are affected—upgrade your infrastructure now!

CERT/CC warns of critical flaws in the Hiawatha web server. The vulnerabilities could allow attackers to bypass authentication and hijack sessions.

CVE-2024-26809 affects Linux nftables with a double-free bug in nft_pipapo_destroy, enabling kernel-level exploitation and potential root access.