 Do Son
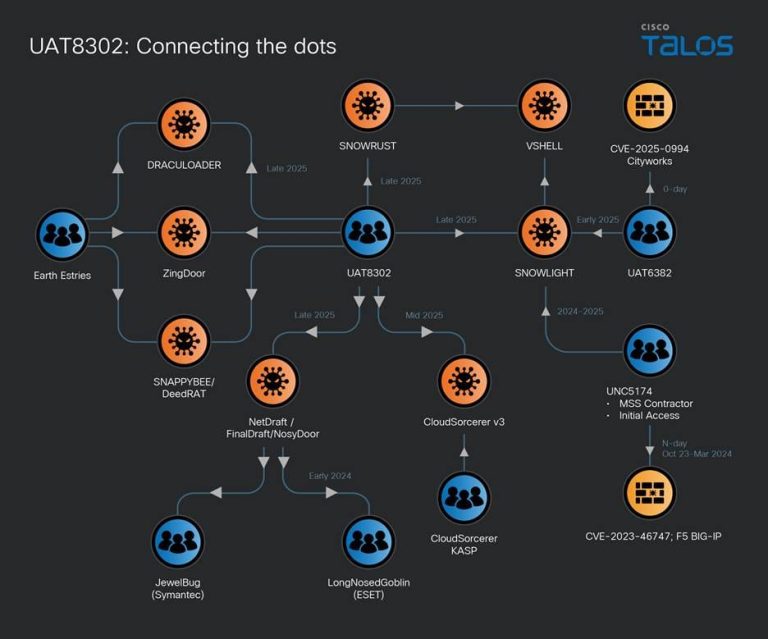
Cisco Talos exposes UAT-8302, a China-linked APT group infiltrating governments via NetDraft and CloudSorcerer. Learn how they share tools with notorious APTs.
Earth Estries

Darktrace dissects SnappyBee (Deed RAT), a stealthy Salt Typhoon backdoor. Learn how it uses DLL side-loading & memory hooking to evade modern AV.

Trend exposed "Premier Pass-as-a-Service," a model where Earth Estries (access broker) and Earth Naga (APT36) share compromised network access to deploy ShadowPad in a coordinated espionage campaign.

Learn about the Earth Estries APT group, a significant cyber espionage actor targeting critical sectors and industries worldwide.

Uncover the intricate cyberespionage campaign of Earth Estries. Learn how this group targets governments and technology firms with sophisticated attack chains.