 Do Son
Check Point details BTR.sys driver abuse: a signed Defender component turned into a kernel EDR/AV bypass with no exploit needed.
EDR Bypass

The GhostLock whitepaper exposes a critical blind spot in ransomware defense. Low-privilege users can freeze SMB shares with zero data encryption.
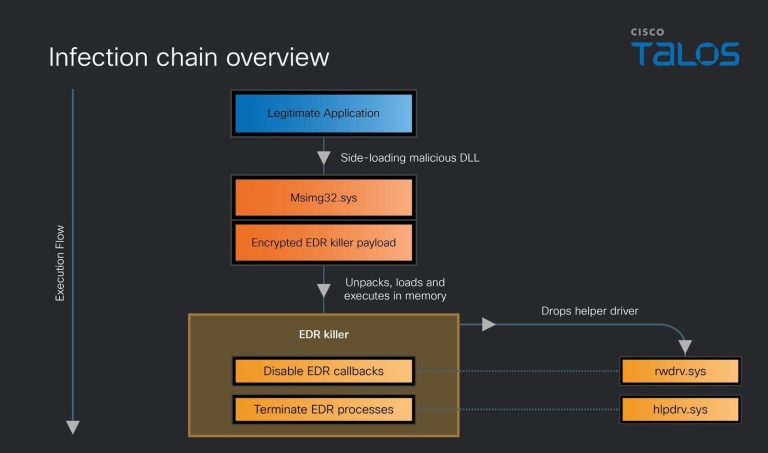
Cisco Talos unmasks a Qilin ransomware payload that terminates 300+ EDR drivers and manipulates the Windows kernel. See how this "EDR Killer" stays invisible.

Discover how attackers use shadow archives (CVE-2026-0866) to bypass AV and EDR by malforming ZIP metadata, keeping malware hidden but executable.

Storm-0249 IAB abuses the SentinelOne EDR process via DLL sideloading to evade detection. The group uses LoLBin tools for fileless execution and sells access to ransomware groups like LockBit.

A military-grade backdoor, ValleyRAT, saw an 85% surge after its builder was leaked. The kernel-mode rootkit bypasses Windows 11 defenses and is now a dangerous commodity for cybercriminals.

Acronis exposed DragonForce's evolution: the ransomware is compiled with MinGW, uses BYOVD drivers to terminate EDR, and contains fixes to prevent decryption of its Conti V3 derived codebase.

Bitdefender exposed Curly COMrades (Russian APT) using Hyper-V to run a hidden Alpine Linux VM. The VM hosts the CurlyShell backdoor, effectively bypassing host-based EDR for espionage.

Trend Research has uncovered a highly sophisticated ransomware campaign by the Agenda group, also known as Qilin,...