 Do Son
Five high-severity Electron vulnerabilities, including CVE-2026-102676, CVE-2026-102673 and CVE-2026-102674, weaken sandbox isolation. Update Electron now.
Electron
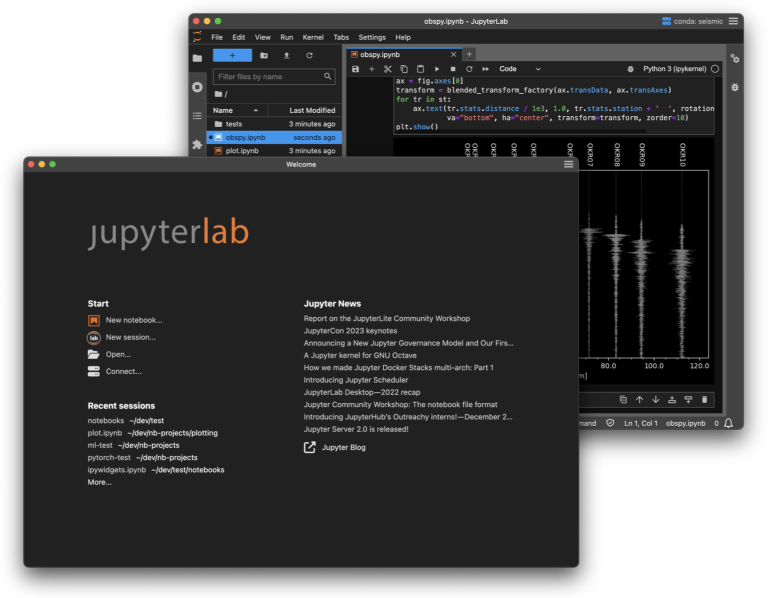
A JupyterLab Desktop vulnerability, CVE-2026-102530 (CVSS 9.4), turns a malicious server URL into remote code execution. Update to 4.6.2-1 now.

Electron patches 5 flaws (CVSS 7.0-8.4) allowing sandbox escapes and context isolation bypass. Update to v41, 40, or 39 to secure your desktop app now.

Intego exposes a malicious Ledger Live app for macOS. Using weaponized Electron ASAR archives and a TLS bypass, OSX/Amos silently siphons your seed phrases.

Elastic Security Labs exposes NOVABLIGHT, a NodeJS-based infostealer-botnet MaaS disguised as an "educational tool," actively distributed via Telegram and targeting victims with fake game installers.
Electron has critical flaws: CVE-2024-46993 allows RCE via image buffer overflow, and CVE-2024-46992 is an ASAR integrity bypass on Windows.

AhnLab Security Intelligence Center have revealed a growing trend of infostealer malware abusing the Electron framework

Electron team has stepped forward to challenge these assertions, shedding light on the intricacies of the vulnerabilities
On January 22, 2018, a known security vulnerability (CVE-2018-1000006) affecting Windows users of Electron-based programs (like discord) was...