
 Do Son
Zscaler exposed Matanbuchus v3.0, a MaaS downloader pivoting to ransomware. The stealthy C++ malware uses Protobufs for C2, QuickAssist for access, and time-wasting loops to bypass sandboxes.
evasion

Rhadamanthys stealer's v0.9.2 update adds new anti-analysis checks, a custom executable format, and uses noisy PNG files for payload delivery to bypass security tools.

A new DarkCloud infostealer variant uses VB6 obfuscation and anti-analysis techniques to steal credentials and crypto wallets from MetaMask, Exodus, and more.

A vulnerability dubbed "LNK Stomping" (CVE-2024-38217) is actively used to strip the 'Mark of the Web' from LNK files, bypassing Windows security policies.
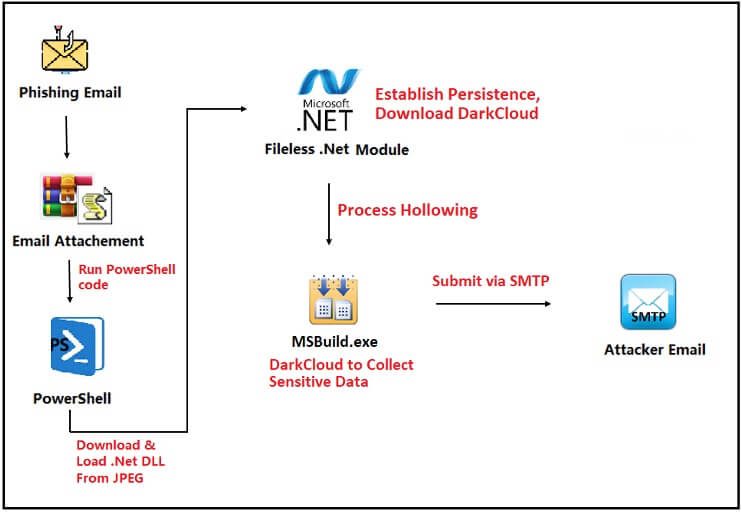
Fortinet uncovers a new DarkCloud stealer variant using a fileless, multi-stage attack chain with obfuscated PowerShell and process hollowing to evade detection and exfiltrate data.

Kaspersky exposes a new AV killer leveraging the legitimate ThrottleStop.sys driver to disable antivirus software and deploy MedusaLocker ransomware in a BYOVD attack.

SentinelLABS and Beazley expose PXA Stealer, a Python-based infostealer campaign targeting 62 countries with stealthy DLL sideloading, decoy files, and Telegram-based data exfiltration.

ThreatLabz reveals the evolution of Raspberry Robin malware, now featuring stronger encryption, complex obfuscation, and a new privilege escalation exploit to bypass detection.

Symantec's report reveals LockBit is using evolved tactics, including DLL sideloading and process masquerading with legitimate executables, to evade detection and deploy payloads.

Sophos uncovers a new infection chain for GOLD BLADE's RedLoader malware, combining LNK files, WebDAV, and DLL sideloading to bypass defenses and deploy payloads stealthily.

Trellix uncovers 0bj3ctivityStealer, a sophisticated info-stealer using phishing, custom PowerShell, and steganography to evade detection and exfiltrate sensitive data.

Netskope uncovers XWorm 6.0, a new variant using VBScript droppers, AMSI bypass, and critical process marking to evade detection and force system reboots if terminated.

Hybrid Analysis reveals SHUYAL, a new stealthy infostealer that harvests browser credentials, system data, and screenshots, exfiltrating it all via a Telegram bot.

CYFIRMA uncovers EdskManager RAT, a sophisticated remote access trojan using HVNC, multi-stage execution, and advanced persistence for covert, long-term system access.

Akamai confirms Coyote, a Latin America-focused banking trojan, is the first malware to exploit Microsoft's UI Automation (UIA) framework in the wild for credential theft.

AmateraStealer (formerly ACRStealer) has significantly evolved, using low-level NTAPIs, Heaven's Gate, and multi-layered encryption to evade detection and steal sensitive data.

eSentire uncovered a sophisticated attack on a US accounting firm, deploying PureRAT via the new Ghost Crypt crypter and a stealthy "Process Hypnosis" injection technique.

Katz Stealer is a dangerous MaaS info-stealer (starting at $100/month) that plunders digital identities, evades detection with stealthy techniques, and targets a vast array of sensitive data.


New email campaign uses tricky tactics and legitimate services to deliver the RATty Trojan in Spain, Italy, and Portugal. Stay alert for invoice scams!