 Do Son
A critical Artifactory authentication bypass flaw (CVE-2026-82329) is exploited in the wild, letting attackers obtain administrative privileges.
Exploit
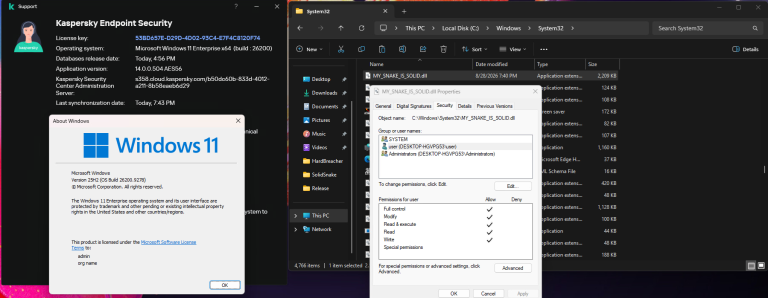
Discover the details of the experimental HardBreacher exploit targeting a potential zero-day vulnerability within Kaspersky Endpoint Security for privilege escalation.
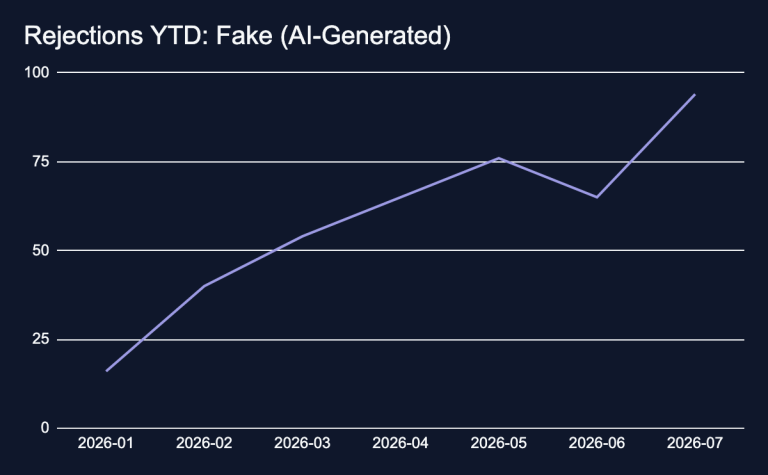
Fake AI PoCs and malicious code are taking over GitHub exploit repositories. Discover how researchers filter through the noise to find real vulnerabilities.

Discover the AutoJack AI agent exploit! We explore the AutoGen Studio vulnerability that allows remote code execution via local MCP WebSockets.
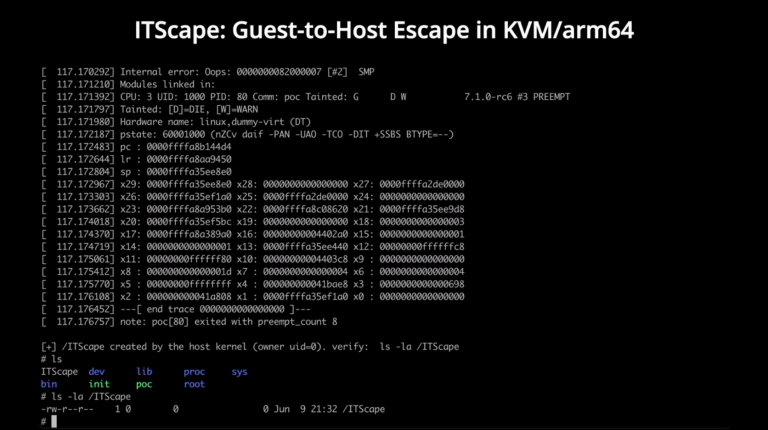
The ITScape KVM escape vulnerability (CVE-2026-46316) threatens arm64 clouds. Details and a guest-to-host escape exploit PoC are now publicly disclosed.

A critical PhpSpreadsheet RCE vulnerability impacts 312 million users. Learn how the CVE-2026-45034 exploit bypasses patches and triggers code execution.

CVE-2026-48095 (CVSS 8.8) is a heap buffer overflow in 7-Zip that a crafted archive can trigger. Update to the patched version now.
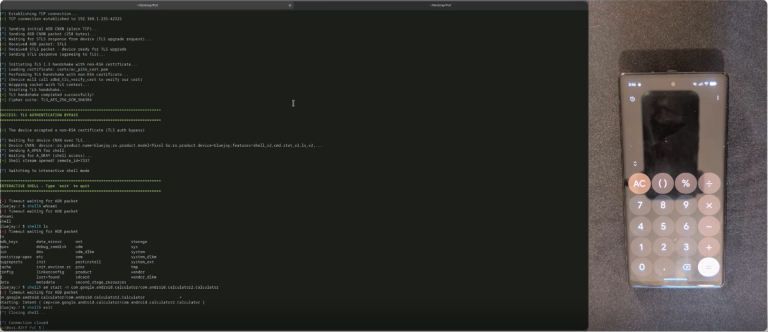
BARGHEST reveals CVE-2026-0073: a zero-click Android ADB bypass over Wi-Fi. Public PoC and exploit details are now live. Secure your mobile device today!
Critical 9.2 CVSS flaw in WattBox 800/820 controllers (CVE-2026-41446) allows root RCE using plaintext hardware labels. Upgrade to firmware v2.10.0.0 now.
LiteLLM CVE-2026-42208 is under active exploitation. Attackers are using SQL injection to steal AI credentials. Patch to v1.83.7 and rotate keys immediately.

A zero-day in Quake III Arena engines (ioquake3, OpenArena) allows attackers to read sensitive system files and target players. Check RCON access now!

CVE-2025-54918 allows attackers to gain SYSTEM privileges on Windows Server 2025 via a new NTLM relay attack that bypasses LDAP Channel Binding. Patch now.

A new report details a 0-click RCE exploit chain in the Linux kernel's ksmbd module that allows an authenticated user to gain root access. A PoC has been published.

Sangoma has issued an urgent security advisory for a FreePBX exploit. Admins with publicly exposed control panels are urged to lock down access immediately.
ImageMagick has patched four security vulnerabilities, including high-severity memory corruption bugs, that could affect applications using the toolkit.

Critical FortiSIEM flaw (CVE-2025-25256) allows remote unauthenticated command injection. Exploit code active in the wild—patch immediately.

A critical UAF flaw in the Linux kernel (CVE-2025-38236) allows for privilege escalation. A PoC exploit is now public, demonstrating how to escape the Chrome sandbox and gain kernel control.

A Windows CLFS zero-day (CVE-2025-29824) actively exploited by RansomEXX and Play ransomware gangs for privilege escalation, with a public PoC. Patch now!
CISA added CVE-2025-25257, a critical FortiWeb SQL injection vulnerability (CVSS 9.6), to its KEV Catalog, confirming active exploitation in the wild. Update immediately!

CISA has added CVE-2023-0386, a critical Linux kernel OverlayFS flaw, to its KEV Catalog, confirming active exploitation allowing local users to gain root privileges.

Two Windows Kernel vulnerabilities allow SYSTEM-level privilege escalation. PoC exploit code is publicly available.
CISA adds two critical vulnerabilities to KEV: Erlang/OTP (RCE) and Roundcube (XSS). Actively exploited, these flaws pose severe risks to systems and email accounts.