
 Do Son
UNC6671 vishing extortion group rebrands across five names, using AiTM credential phishing to hit financial services and enterprise cloud accounts.
Extortion
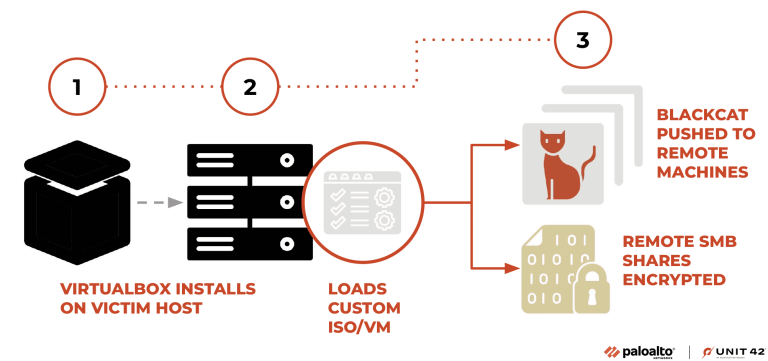
A Florida ransomware negotiator got 70 months for feeding clients' secrets to BlackCat ransomware actors. The DOJ seized over $10 million in proceeds.
Two US cybersecurity professionals get 4 years in prison for acting as ALPHV BlackCat ransomware affiliates, extorting victims and leaking patient data.
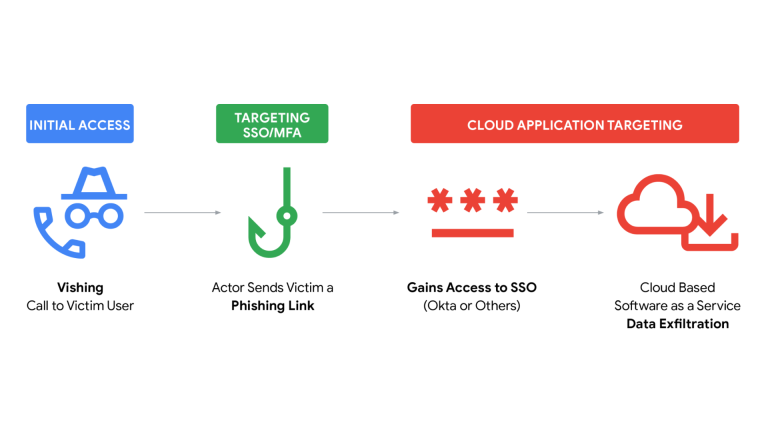
Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.

Nefilim's Artem Stryzhak pleads guilty to targeting $100M+ firms. As he faces 10 years, the DOJ offers an $11 million reward for leader Volodymyr Tymoshchuk.

Trend Research warns that ransomware is shifting to AWS S3, exploiting misconfigured IAM and SSE-C keys in five attack variants to cause irreversible data loss and cloud-native extortion.

A new report shows LAPSUS$, Scattered Spider, and ShinyHunters have formed a collaborative alliance, sharing tactics like social engineering and MFA bypass to launch global attacks.

The DOJ has charged Thalha Jubair, a UK national, for his role in the notorious Scattered Spider group's $115M cybercrime and extortion campaign.

The FBI has issued a FLASH Alert warning about UNC6040 and UNC6395, two groups actively compromising Salesforce via vishing and malicious OAuth apps to steal data.

A hacker group is extorting an art platform with a new threat: if the ransom isn't paid, they will feed the stolen artworks to AI training models.

The UK government is drafting new legislation to criminalize ransomware payments by public sector bodies (NHS, schools, councils) to deter attacks and cut off funding to cybercriminals.

A former US Army soldier, Cameron John Wagenius (kiberphant0m), pleaded guilty to hacking telecom companies, stealing data, and attempting to extort $1 million.

The DOJ is criminally investigating a former DigitalMint ransomware negotiator for allegedly colluding with hackers and taking a cut of ransom payments, a betrayal of client trust.

RapperBot botnet resurfaces with 50,000+ active bots, now demanding Monero extortion to halt DDoS attacks. The self-proclaimed "rapper" malware targets IoT devices globally.

Iranian national Sina Gholinejad pleaded guilty for his role in the Robbinhood ransomware attacks targeting U.S. cities like Baltimore.
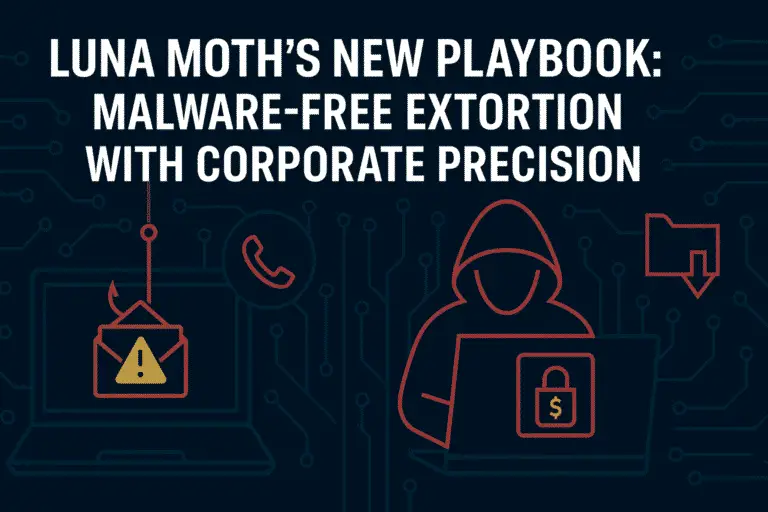
EclecticIQ report details Luna Moth's callback phishing attacks using legitimate RMM tools to breach US legal, financial firms for multi-million dollar ransoms.