
 Do Son
Urgent! DNN Platform has a Critical CVSS 10.0 flaw allowing unauthenticated users to overwrite files, leading to site defacement & XSS. Update to 10.1.1.
file upload
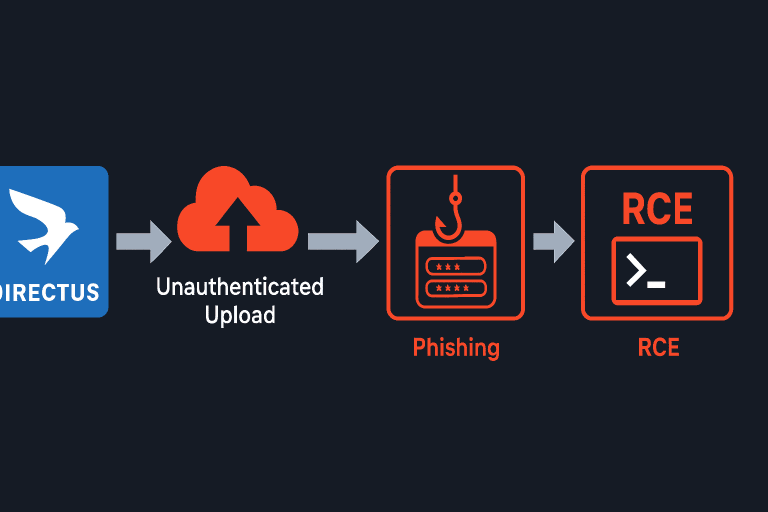
A critical vulnerability in the Directus API (CVE-2025-55746) allows unauthenticated attackers to silently upload and modify files, leading to webshells and RCE.

JPCERT/CC warns of critical flaws (CVSS 9.8) in SATO industrial label printers that allow unauthenticated remote attackers to upload malicious Lua scripts for root access.

Apache Tomcat 9.0.107 patches three critical DoS flaws (CVE-2025-52434, CVE-2025-52520, CVE-2025-53506) that can disrupt web services via HTTP/2, file uploads, and excessive streams.

Critical (CVSS 10) unpatched flaw in TI WooCommerce Wishlist allows unauthenticated RCE via file upload. Affects 100K+ sites.

Details on a zero-day vulnerability (CVE-2025-31324) in SAP NetWeaver that allows file uploads and its link to the Qilin ransomware group.

Two CVEs in TheGem WordPress theme let subscriber-level users upload malicious files and take over sites. Patch to version 5.10.3.1 now.

IBM patches CVE-2024-51466 and CVE-2024-40695 in Cognos Analytics to prevent system compromise, sensitive data leaks, and remote code execution.

A vulnerability (CVE-2024-12556) in Kibana allows code injection via prototype pollution, file upload, and path traversal. Upgrade to the latest version or disable the integration assistant to mitigate this high-severity security risk.