
 Do Son
PyStoreRAT, a new fileless RAT, is spreading via fake GitHub repositories targeting developers. It executes as a JS implant via mshta.exe and includes explicit evasion logic against CrowdStrike.
fileless

The JS#SMUGGLER campaign uses "Junk Code" JavaScript and fileless PowerShell executed via mshta.exe to bypass EDR. This multi-stage attack silently installs the NetSupport RAT.

Trend exposed the Water Saci worm, a self-propagating campaign that hijacks WhatsApp Web using Selenium/PowerShell. It uses a stealthy IMAP email C2 channel with HTTP fallback.
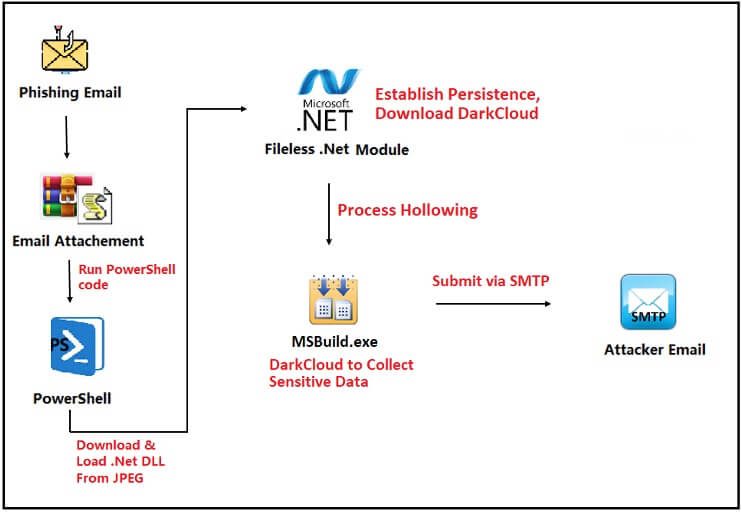
Fortinet uncovers a new DarkCloud stealer variant using a fileless, multi-stage attack chain with obfuscated PowerShell and process hollowing to evade detection and exfiltrate data.

A new stealthy campaign uses Windows LNK files to deploy the REMCOS backdoor via multi-stage PowerShell commands, bypassing antivirus and gaining full system control.

Huntress has recently uncovered a new wave of malicious activities involving the well-known SocGholish or FakeUpdates malware.

One of the most notable aspects of CLOUD#REVERSER is its use of Google Drive and Dropbox for C2 communication and data exfiltration