 Do Son
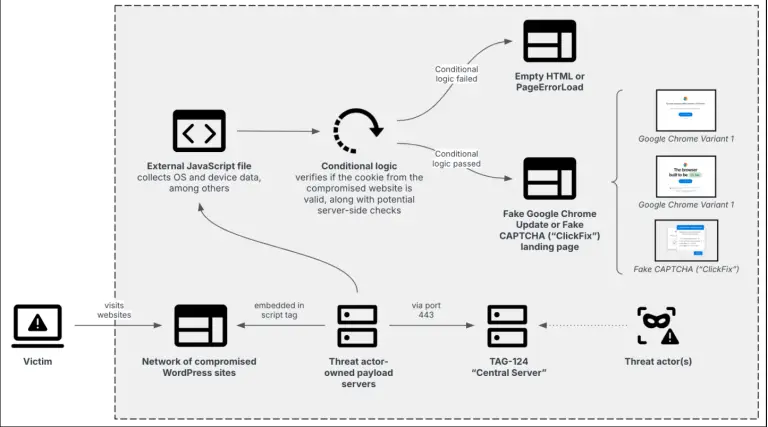
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.
FIN7

Discover AnubisBackdoor, a Python-based malware that allows full control over infected machines with advanced evasion techniques.

Explore the findings on BitLaunch hosting provider and its potential links to ransomware activities in the cybercrime ecosystem.

Sophos X-Ops uncovers ransomware campaigns STAC5143 and STAC5777 targeting Microsoft Office 365 and Teams. Learn how these campaigns exploit email bombing and vishing techniques.

Explore the in-depth analysis of PackXOR, a private packer used by threat actors, including FIN7, to evade detection and carry out malicious activities.

Researchers found advertisements offering a specialized tool for bypassing security systems called AvNeutralizer

Notably, DiceLoader has been actively used since 2021, with the malware often delivered via a PowerShell script.