 Do Son
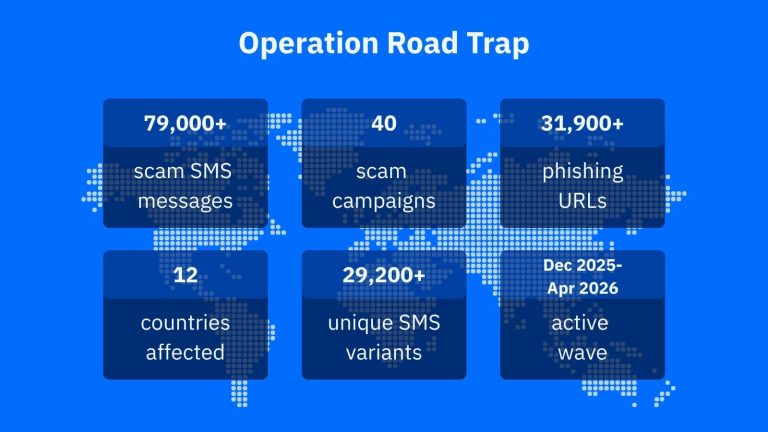
Bitdefender uncovers a massive smishing campaign targeting drivers with fake toll and parking fines. Over 79,000 messages sent across 12 countries.
financial fraud
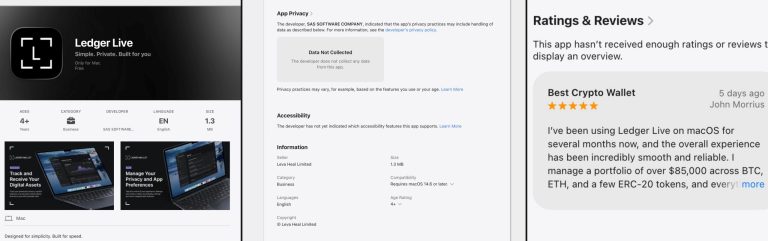
A malicious fake Ledger Live app on the Mac App Store has stolen $9.5M from users. Learn how the scam bypassed Apple's security and why your seed phrase is at risk.
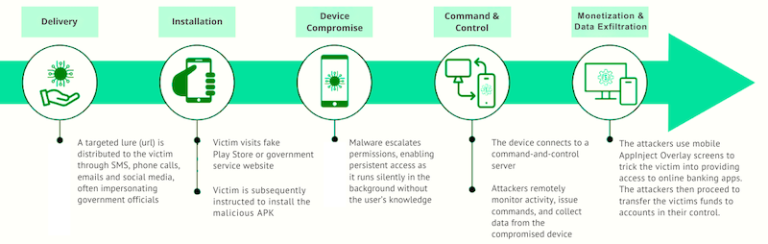
Infoblox uncovers the K99 compound: a brutal MaaS operation using human trafficking to power biometric hijacking and global Android banking fraud.

OFAC sanctions a North Korean IT worker network and global facilitators for defrauding U.S. businesses of nearly $800M to fund the regime's WMD programs.
The FBI warns of a massive surge in ATM jackpotting attacks. Cybercriminals are using Ploutus malware to bypass the XFS layer and drain cash reserves.
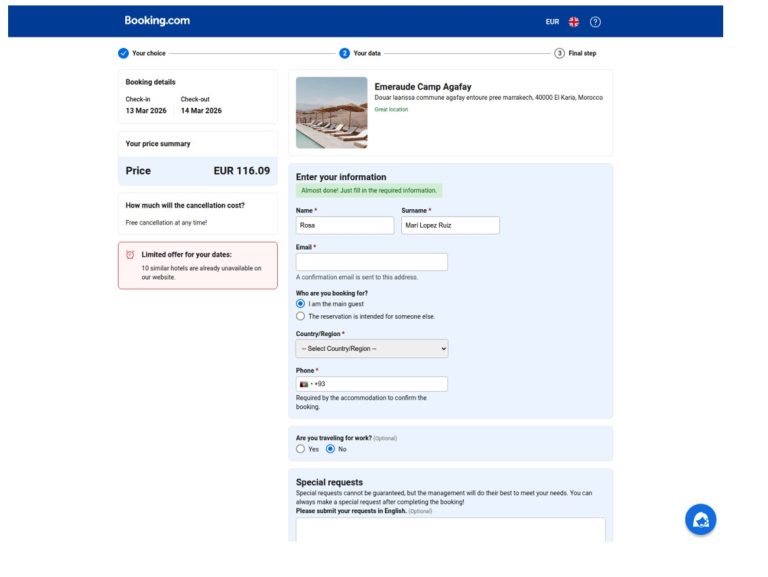
Bridewell warns of Russian hackers targeting Booking.com. Phishing kits steal hotel staff creds to scam guests with "I Paid Twice" messages.

Group-IB reveals a sophisticated loan phishing campaign in Peru. Scammers use the Luhn algorithm to validate stolen credit cards via fake ads.

Scammers target PNB MetLife users via mobile phishing. Attackers use Telegram bots to steal data & manipulate clipboards for UPI fraud.

New "Ghost Tap" malware lets hackers relay NFC signals from your Android phone to steal funds remotely. Learn how this sophisticated Group-IB discovery works.

SEQRITE Labs uncovers a China-linked campaign targeting Indian firms with fake tax notices to install persistent Remote Access Trojans.
Tap-and-Steal: Over 760 Android Apps Exploit NFC/HCE for Payment Card Theft in Global Financial Scam

Tap-and-Steal: Over 760 Android Apps Exploit NFC/HCE for Payment Card Theft in Global Financial Scam
Zimperium found 760+ Android apps exploiting NFC/HCE to steal payment data. The malware impersonates 20 banks across Russia, Poland, and Brazil, using Telegram for criminal coordination.

Trend Micro uncovered "Water Saci," a self-propagating malware (SORVEPOTEL) that hijacks WhatsApp Web sessions to spread aggressively and steal Brazilian banking credentials.

A new AI scam network is targeting Indian social media users. It uses deepfakes of celebrities and fake news sites to promote fraudulent investment schemes.

SikkahBot, a new Android malware, is impersonating scholarship apps to steal financial data and automate transactions from students in Bangladesh.

Cleafy uncovers PlayPraetor, a Chinese-speaking MaaS Android RAT that has infected 11,000+ devices, using real-time control via Accessibility Services to conduct on-device fraud.

Akamai confirms Coyote, a Latin America-focused banking trojan, is the first malware to exploit Microsoft's UI Automation (UIA) framework in the wild for credential theft.

Greedy Sponge, a financially motivated group, is back with an upgraded AllaKore RAT and SystemBC, targeting Mexican organizations for banking credentials and financial fraud.

Group-IB uncovers Qwizzserial, a new Android malware family stealing financial data from thousands in Uzbekistan by exploiting SMS-based 2FA via Telegram-distributed APKs.

AntiDot, an Android trojan from LARVA-398, is infecting thousands of devices via MaaS, using MediaProjection API and Accessibility Services to steal financial and personal data.

Silent Push uncovers crypto scam using Twitter ad loophole to spoof CNN and Apple, luring users into buying fake iTokens via misleading redirects.
Bitdefender uncovers a large network of convincing mystery box scams on social media stealing credit card data via hidden subscriptions. Watch out!
A Nigerian national received a 97-month sentence for a $6M inheritance scam targeting over 400 victims, many elderly. Learn about this fraud.