 Do Son
CVE-2026-46442 in Flowise allows authenticated users to escape the NodeVM sandbox and execute system commands. Secure your AI infrastructure now!
Flowise
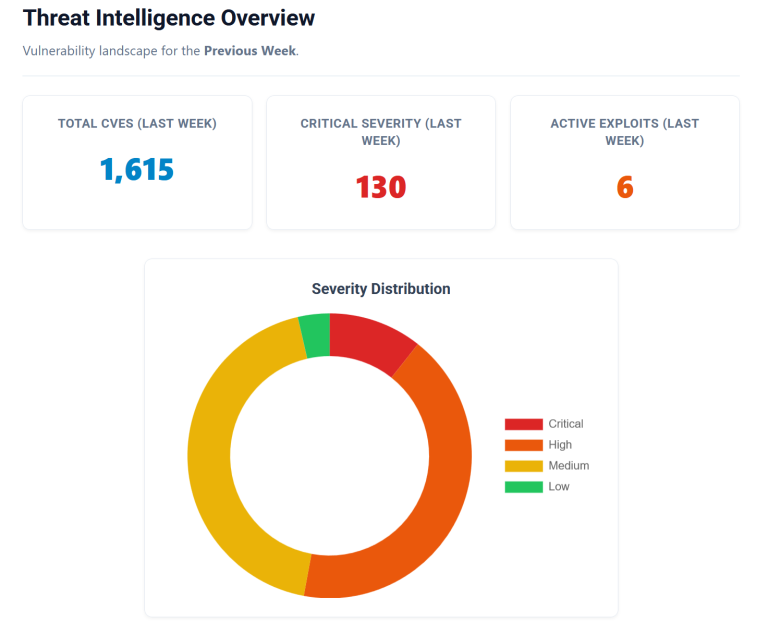
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.
Critical Flowise Flaw Allows Unauthenticated Remote Admin Takeover via Exposed Registration Endpoint

Critical Flowise Flaw Allows Unauthenticated Remote Admin Takeover via Exposed Registration Endpoint
The team behind Flowise—a popular open-source platform for building AI agents and LLM workflows—has issued an urgent...
Flowise patched a Critical (CVSS 10.0) RCE flaw (CVE-2025-61913) in WriteFileTool. Authenticated attackers can write arbitrary files to the filesystem to gain command execution.

Two critical remote code execution (RCE) vulnerabilities with CVSS scores of 9.8 were found in the open-source Flowise AI platform.

Explore the critical CVE-2025-26319 vulnerability in Flowise that allows attackers to exploit file uploads and compromise servers.

Discover the alarming findings of Legit Security's report on the security vulnerabilities of publicly accessible GenAI development services.